How does the Reveelium UEBA / Threat Hunting SIEM work?
The principles governing the operation of SIEM (Security Information and Event Management) tools have been established for years. The integration of artificial intelligence into cybersecurity tools is less widely understood. We aim to explain it clearly here, despite the extensive technical expertise usually required to fully grasp the inner workings of cutting-edge AI technologies.
The core building blocks:
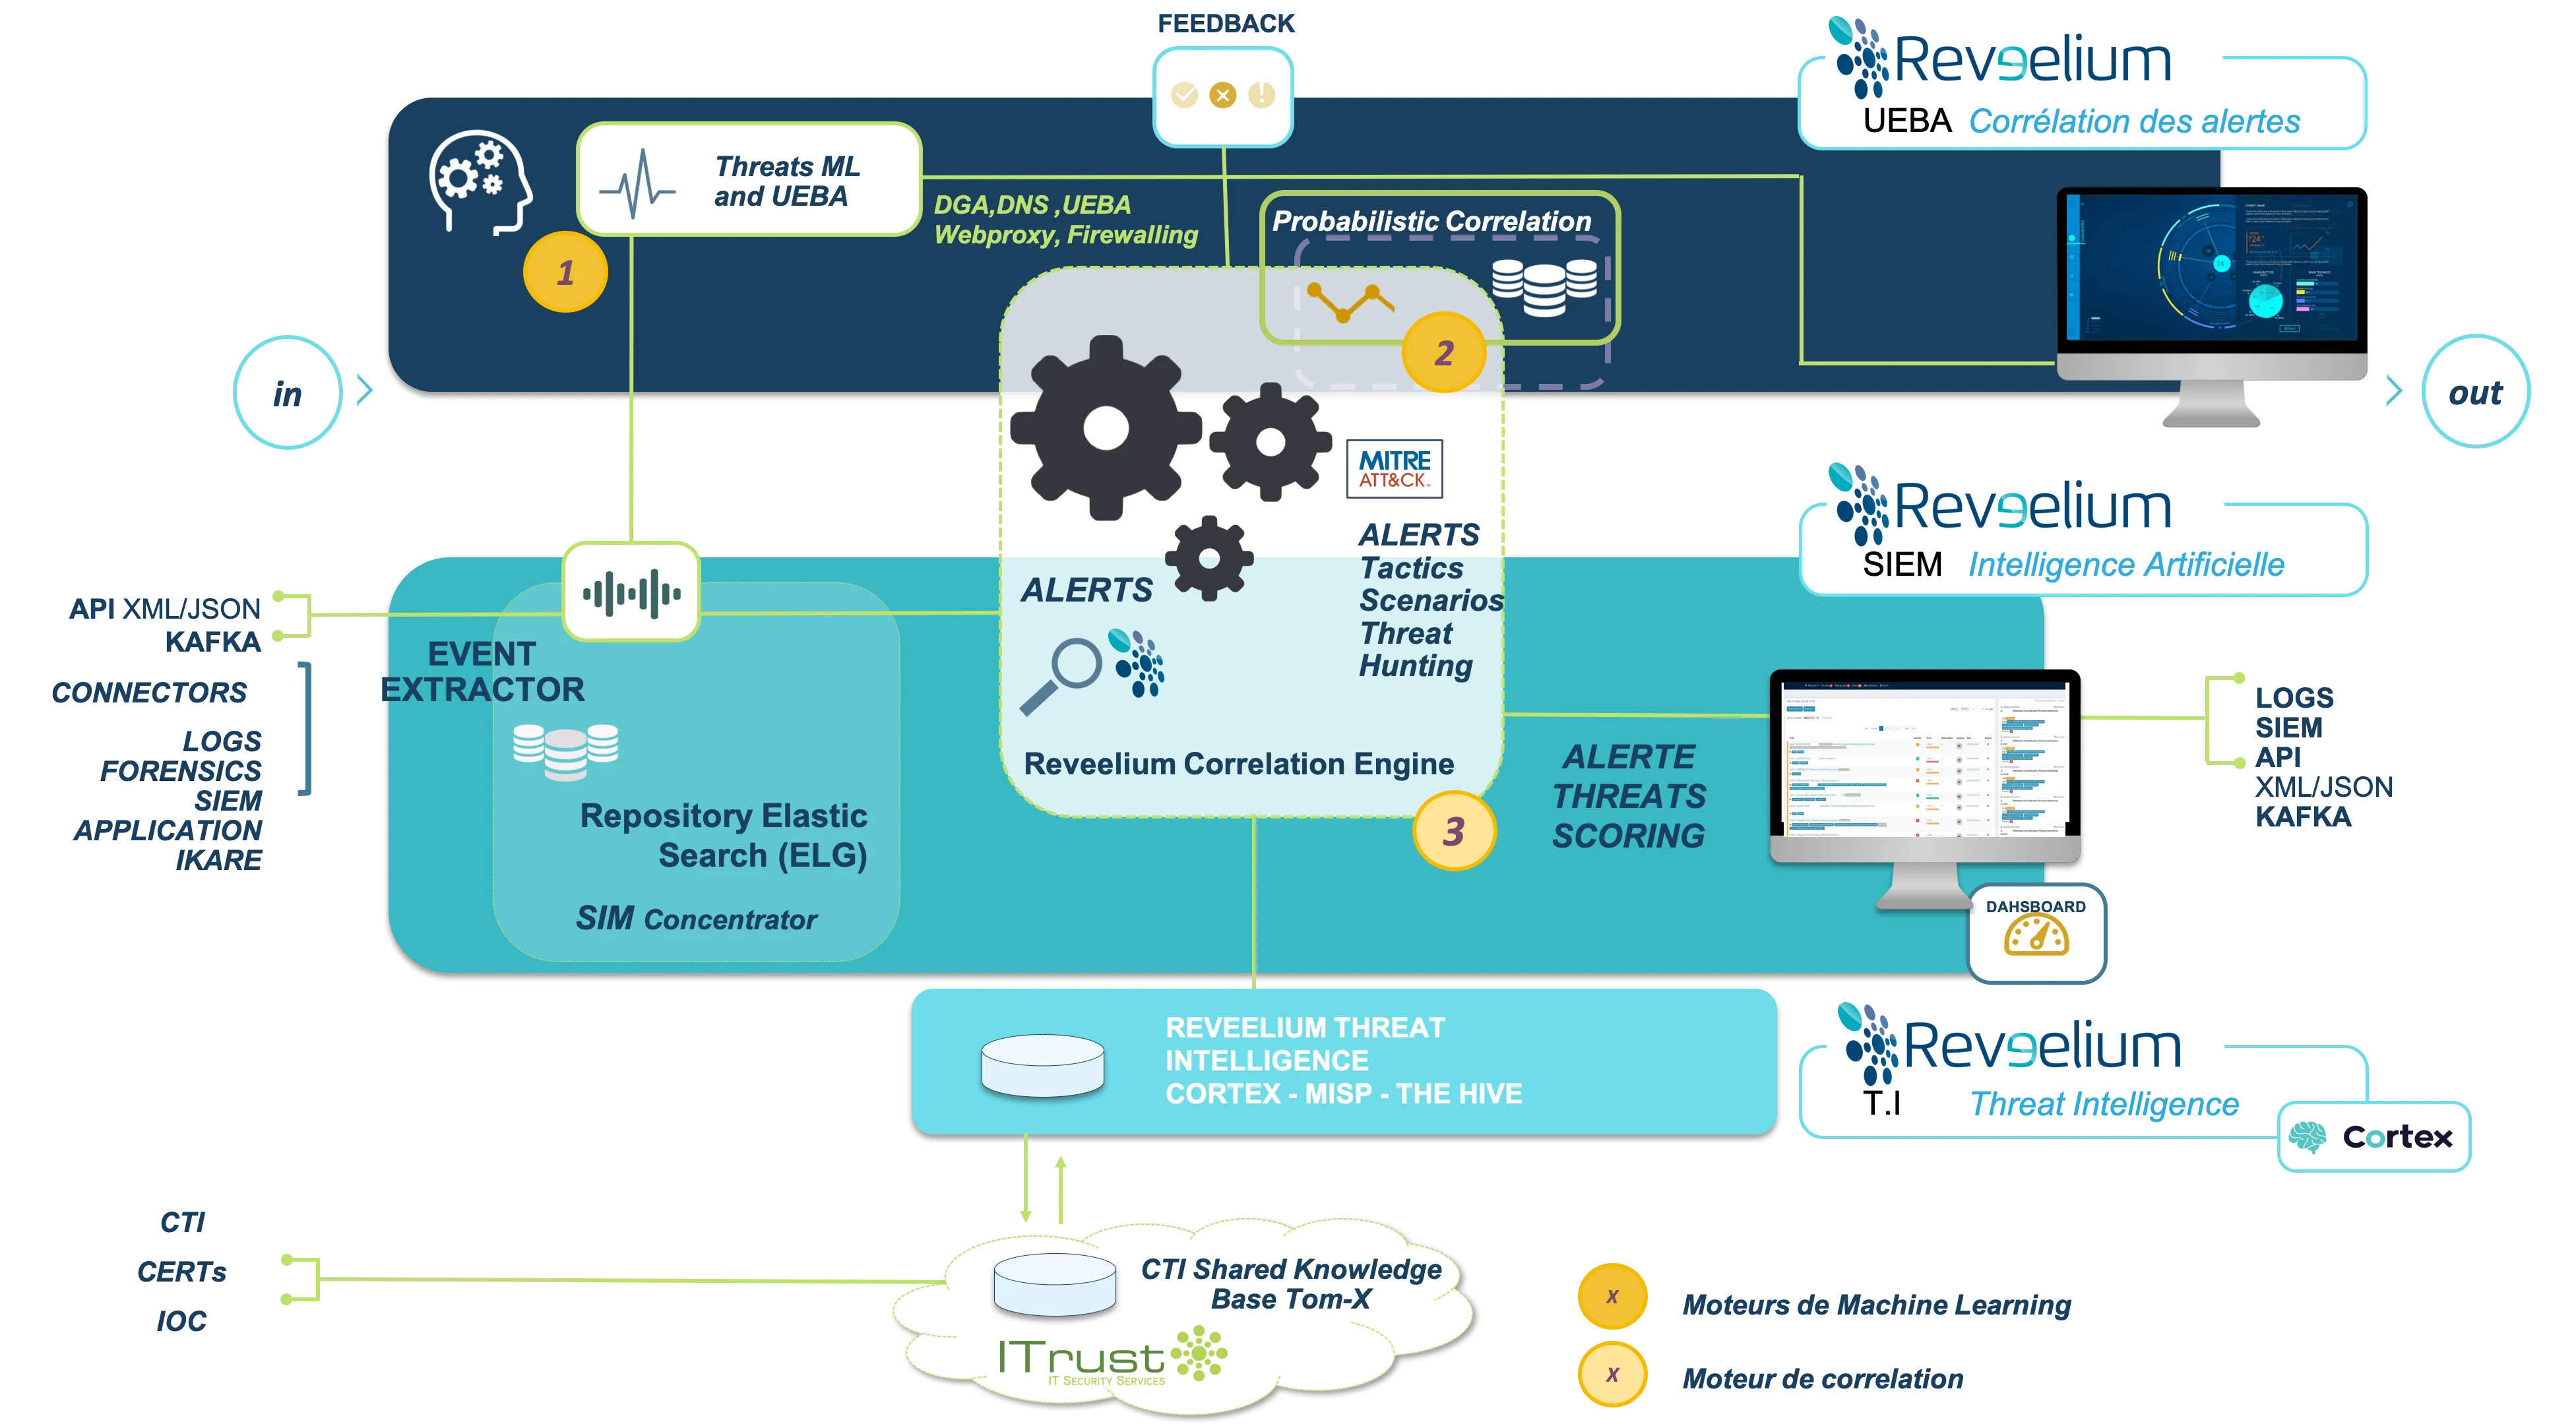
- A SIM: Security Information Management: centralizes and aggregates logs from applications, network devices, and security tools (firewalls, antivirus, proxies, etc.). An advanced SIM can generate alerts based on (simple) search criteria within databases. Within Reveelium, we leverage an Elasticsearch / Graylog database to centralize incoming data.
- Example: a high-risk Windows event, an antivirus detection event
- A Reveelium SIEM (which also incorporates the SIM): this tool correlates received events to detect attack tactics and/or techniques (cf. MITRE ATT&CK), or malicious activity, based on scenarios, threshold rules, or frequency counts.
- Example: A sequence of alerts matching a MITRE-classified threat pattern.
Reveelium's correlation engine (3) processes diverse inputs: events, logs, alerts, threats generated by the AI engine, probabilistic threat outputs, or threat intelligence feeds. Standard SIEMs on the market, by contrast, perform only basic correlation.
The Reveelium SIEM is paired with our proprietary AI / UEBA engine, enabling it to:
– detect weak signals that evade rules- or signature-based scenarios (such as ransomware, APTs, etc.).
– reduce false positives, thereby increasing SOC analyst productivity and eliminating background noise.
The challenge lies in processing massive volumes of data while delivering optimal, accurately scored, and prioritized detections with minimal false positives.
The Reveelium UEBA / Threat Hunting Engine: delivers robust machine learning processing power, enabling it to:
- Detect anomalous behavior (1) based on events and logs ingested from the SIM/SIEM.
For instance: abnormal user behavior through proxies, anomalous traffic on firewalls or DNS servers, indicating potential compromise.
In doing so, it qualifies attack techniques that bypass traditional signature- or scenario-based detection methods. Most UEBA SIEMs on the market lack advanced capabilities in these techniques. Reveelium is one of only 5 technologies globally that natively integrates such detection capabilities.- Example: detection of a DGA during the 2016 Petya outbreak, preventing the execution of the ransomware attack that targeted our client Saint-Gobain (€60M in potential losses avoided)
- Correlate (2) probabilistically (released late 2020) all alerts, detected techniques, and threats via a globally unique behavioral engine
- Example: Enables the detection of malicious behavior across vast amounts of events or alerts without relying on pre-set scenarios or signatures.
- Score and prioritize threats (encompassing all identified malicious techniques and tactics) to minimize analyst handling time, accelerate incident response, and empower the Blue Team's detection capabilities.
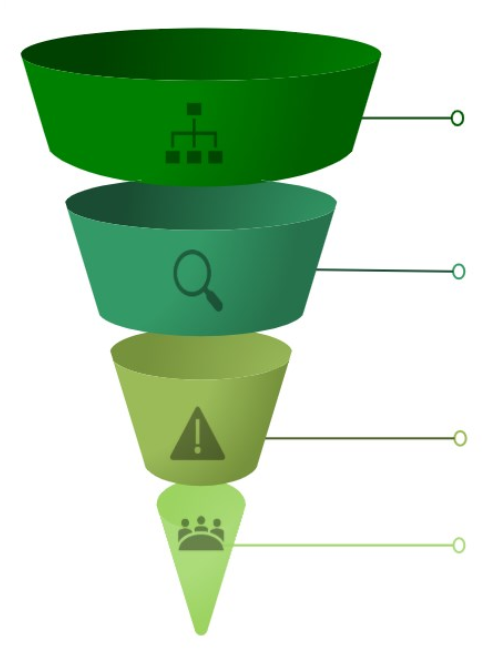
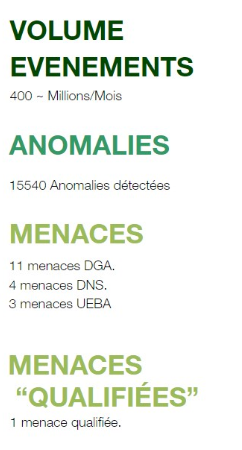
- Example: Petya resulted in 3 threats scored at 80/100 instead of 300 unmanageable alerts.
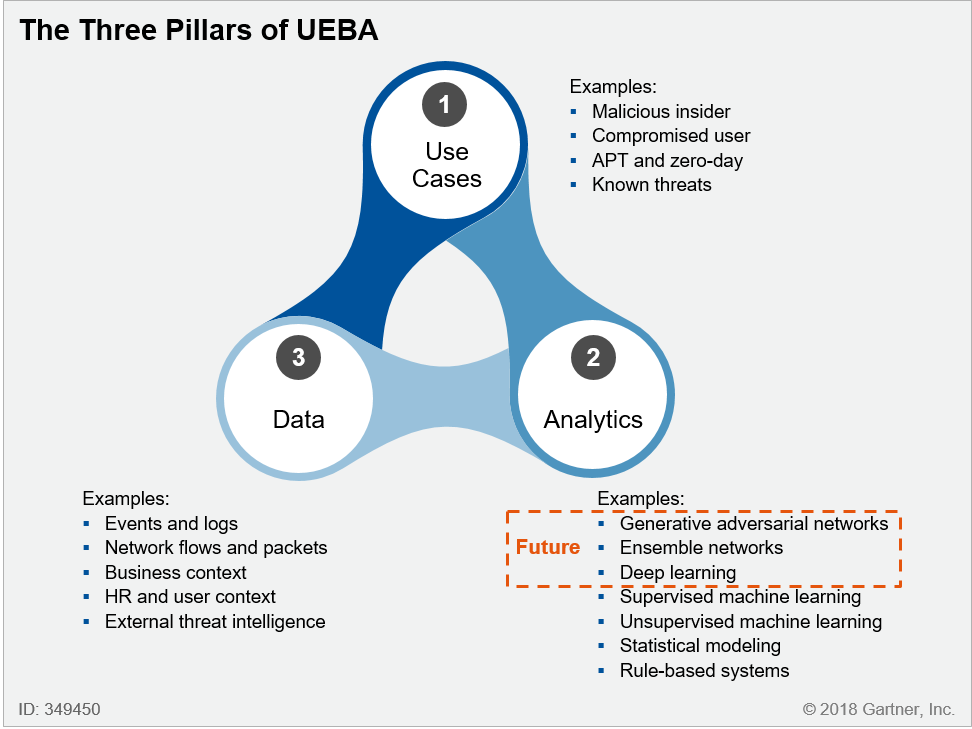
Correlation engines (2) and (3) address the critical challenge highlighted by Gartner and our enterprise clients:
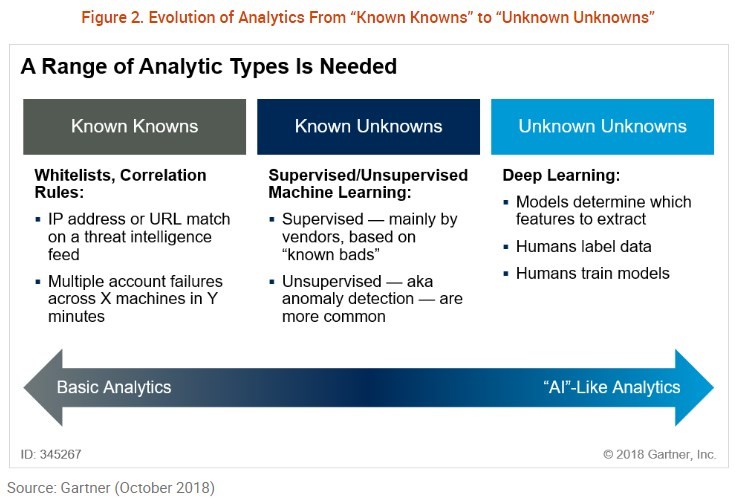
ITrust's AI-driven behavioral and probabilistic detection engine has been under active development since 2010. It is recognized across the industry as a disruptive technology (see industry awards)
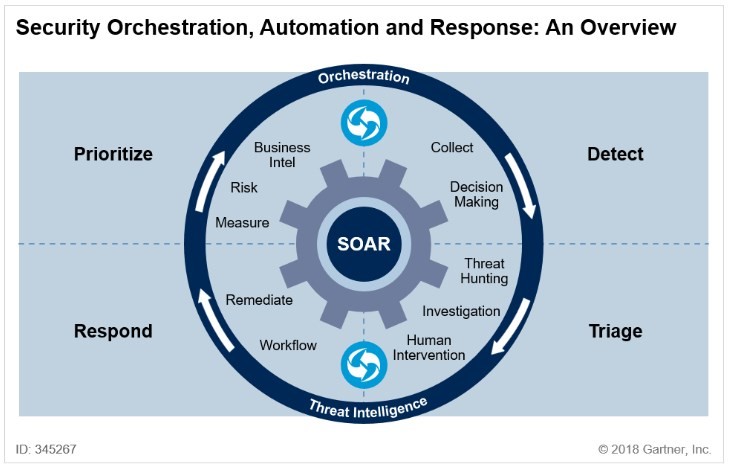
Reveelium SIEM and Reveelium UEBA/Threat Hunting operate seamlessly together, sharing the core SIEM correlation engine alongside the AI probabilistic correlation engine to power a high-performance SOC (Security Operations Center):
- optimized detection prioritization
- fewer false positives
- threat scoring mapped to the MITRE framework, maximizing analyst efficiency and detection capabilities, paving the way for SOAR integration (when paired with the ACSIA EDR module)
- an alerting framework (TheHive)
- a case management and workflow orchestration engine for streamlined incident investigation
- native integration capabilities with a vulnerability scanner (Ikare) and an EDR (ACSIA)
- comprehensive reporting modules to deliver activity-specific dashboards: Healthcare, PCI/DSS, regulatory compliance, etc.
- KPIs tailored to specific stakeholder profiles (managers, C-level executives, or security analysts)