
Above: Field feedback
CIOs, CISOs, or managers often ask us what best practices should be implemented to protect themselves effectively and swiftly.
The first answer I give them is to identify risks and establish a simple organization (CISO, DPO, ISSP) tailored to how the organization operates.
Within ITrust for 14 years, we have had the time to develop strong insight into best practices, correlating them with those identified by ANSSI, ENISA, or SANS. We hold solid convictions and wanted to corroborate them with a concise study based on recognized, independent standards.
The study is straightforward. We analyzed each attack technique used by hackers, malware, malicious insiders, and threat actors, evaluating whether the attack vector was detected and deflected by various technologies: Does an antivirus detect privilege escalation? Does a firewall detect a C2 server used by Emotet, etc.?
To ensure realistic results, we analyzed two comprehensive studies by RedCanary and Dark Reading that evaluate the attack techniques most frequently observed in recent 2020 attacks.
These conclusions were then compared against our field experience. We identified the attack techniques that ITrust encounters among its clients or across its network during major attacks or those causing the highest impact on organizations.
We reviewed this overview alongside our engineering teams to draw actionable conclusions.
Here is the MITRE matrix used, showing coverage rates by technology type.
We applied the same methodology to Antivirus, Firewalls, SIEM, etc.
For each protection technology type, we displayed its coverage percentage across different MITRE attack techniques. In the subsequent columns, we detailed their coverage based on their ability to detect the 10 and 3 most prevalent techniques currently leveraged by hackers and malware. Finally, the last column highlights their coverage rate against the most critical threats (APTs, ransomware, etc.) assessed by ITrust's Red Team and Threat Hunting teams.
Chart 1: Number of MITRE techniques covered
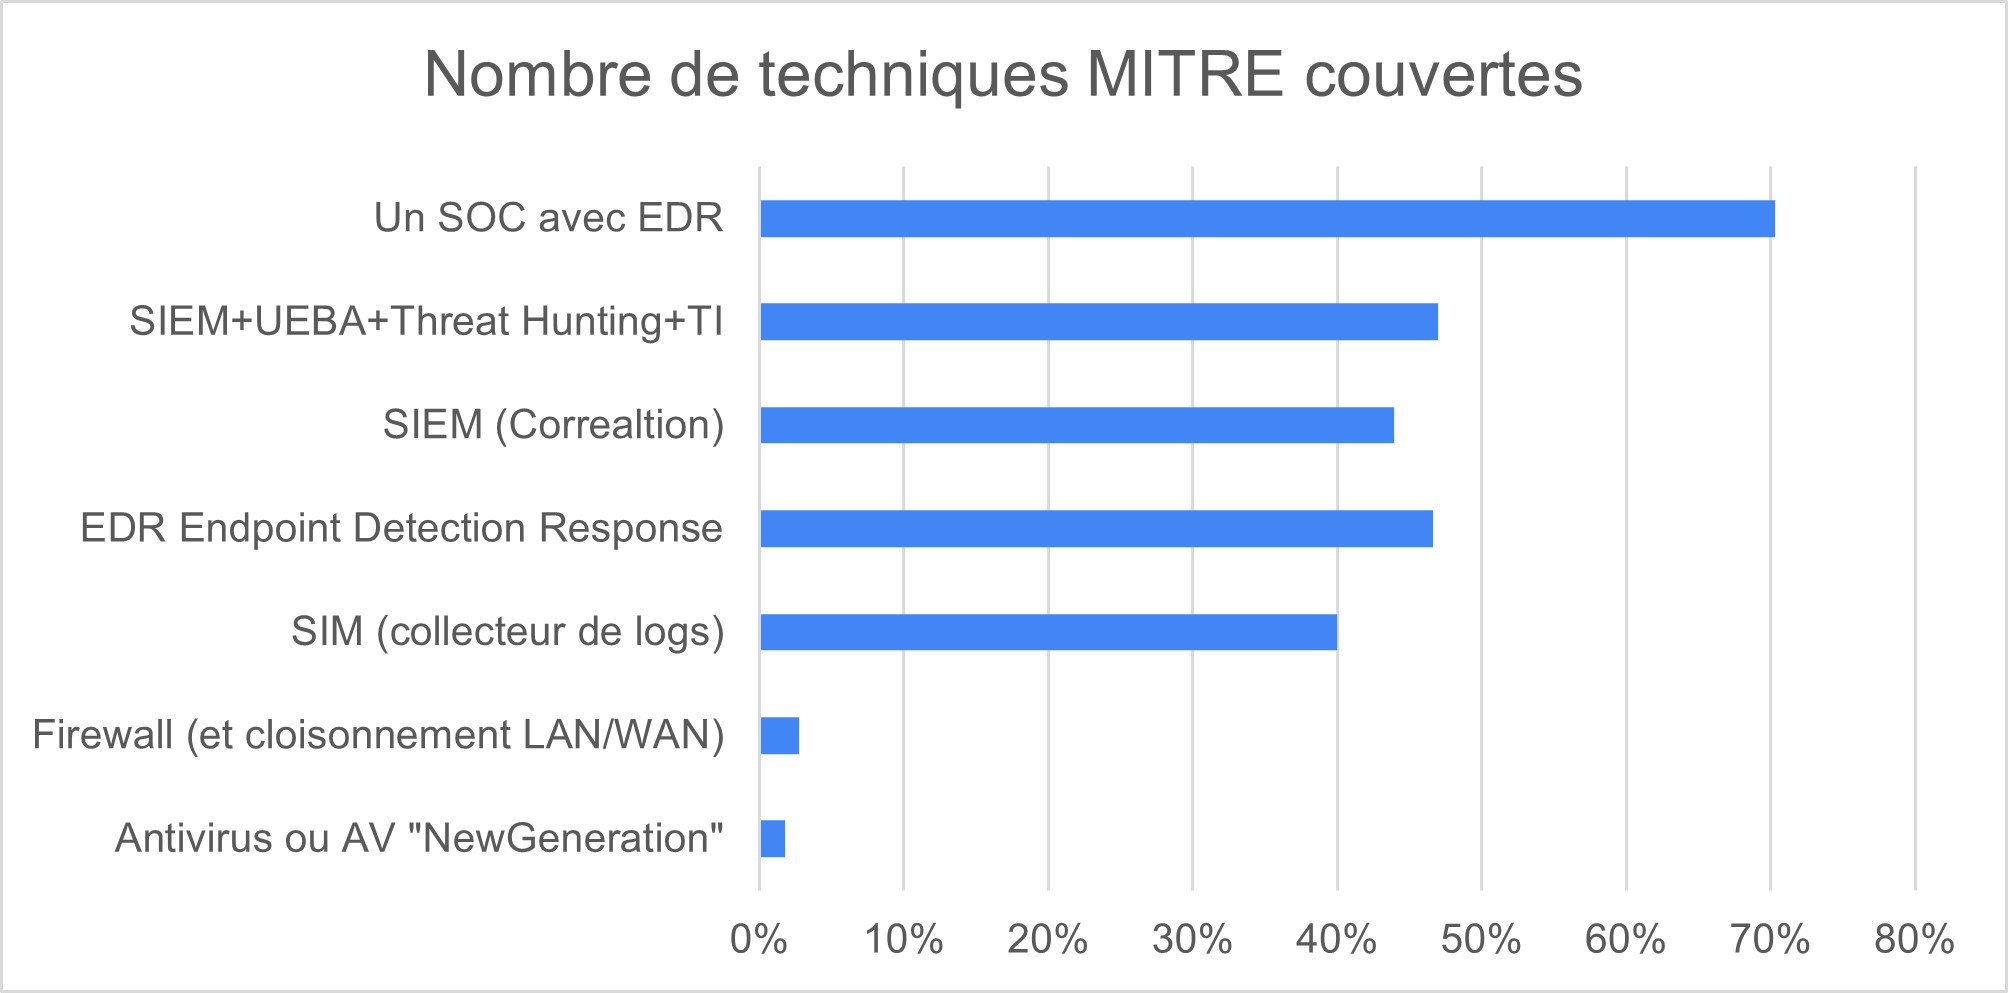
Chart 2: MITRE techniques covered, among the 3 most dangerous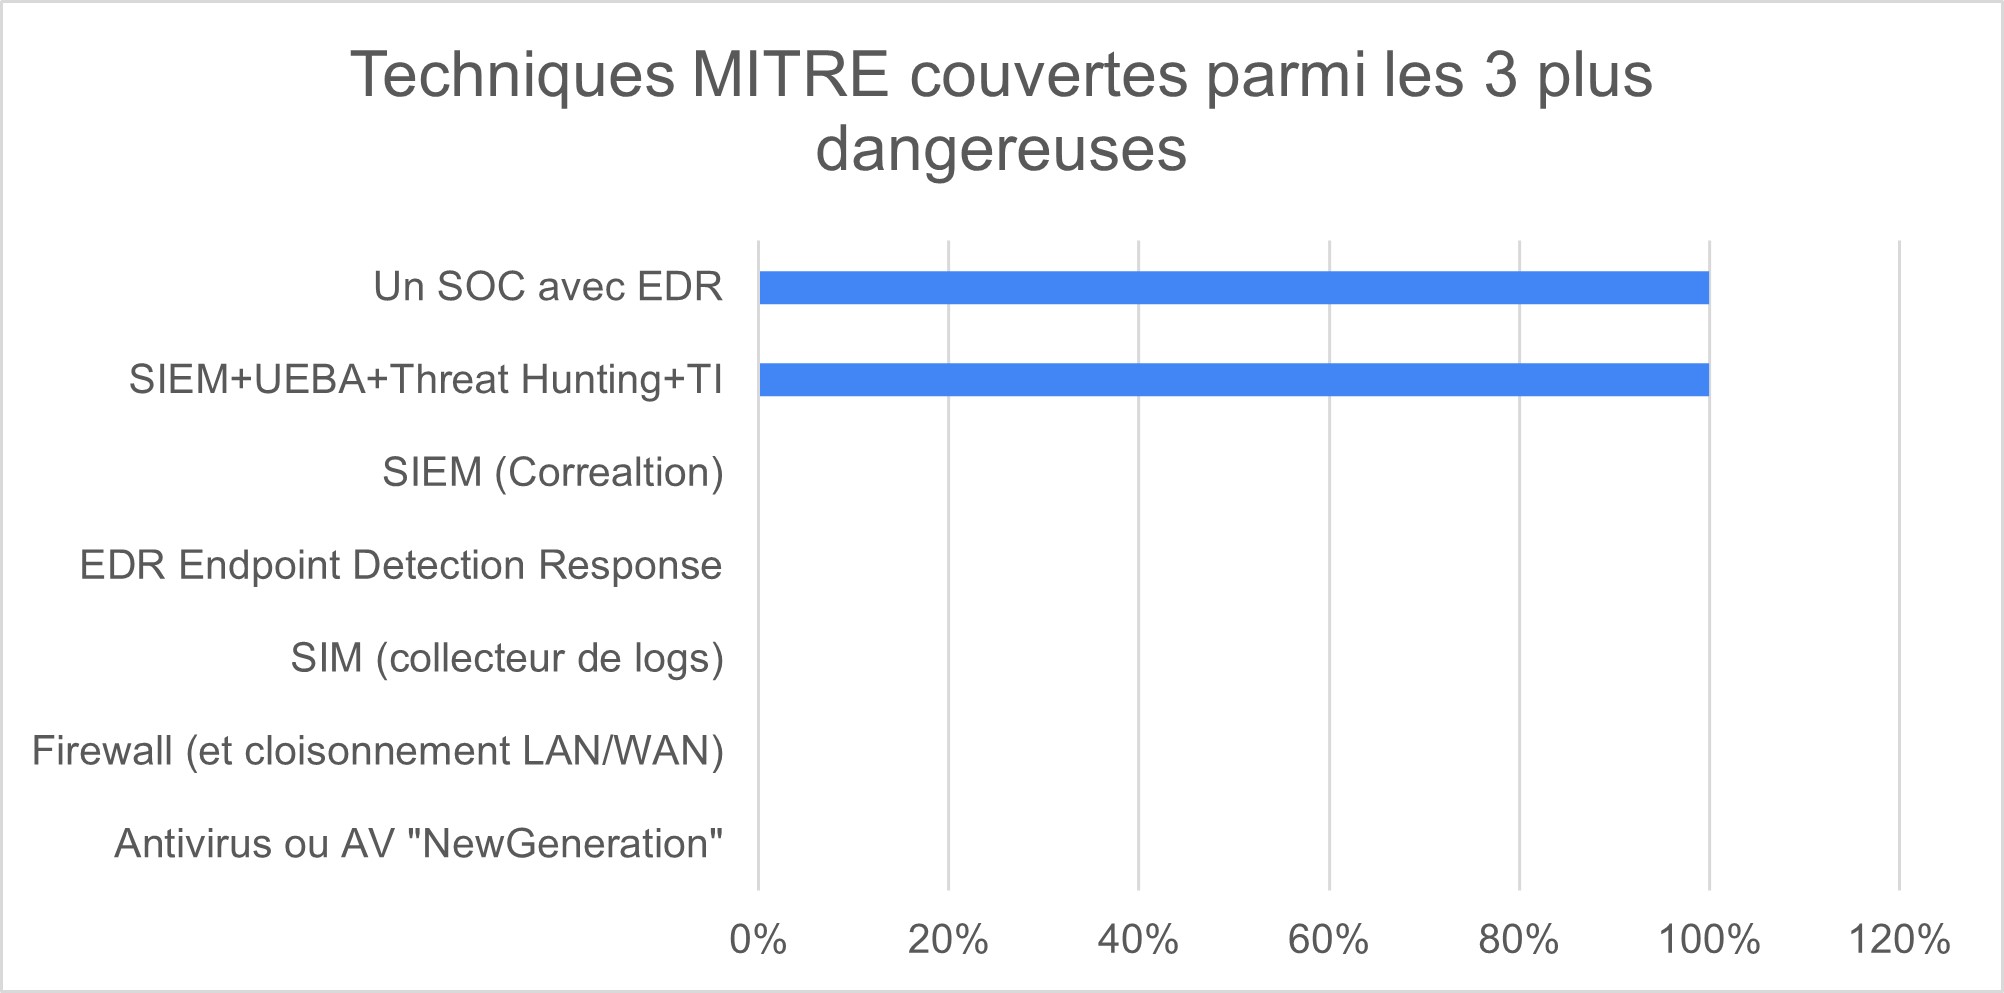
Chart 3: MITRE techniques covered, among the 10 most used by hackers/attackers 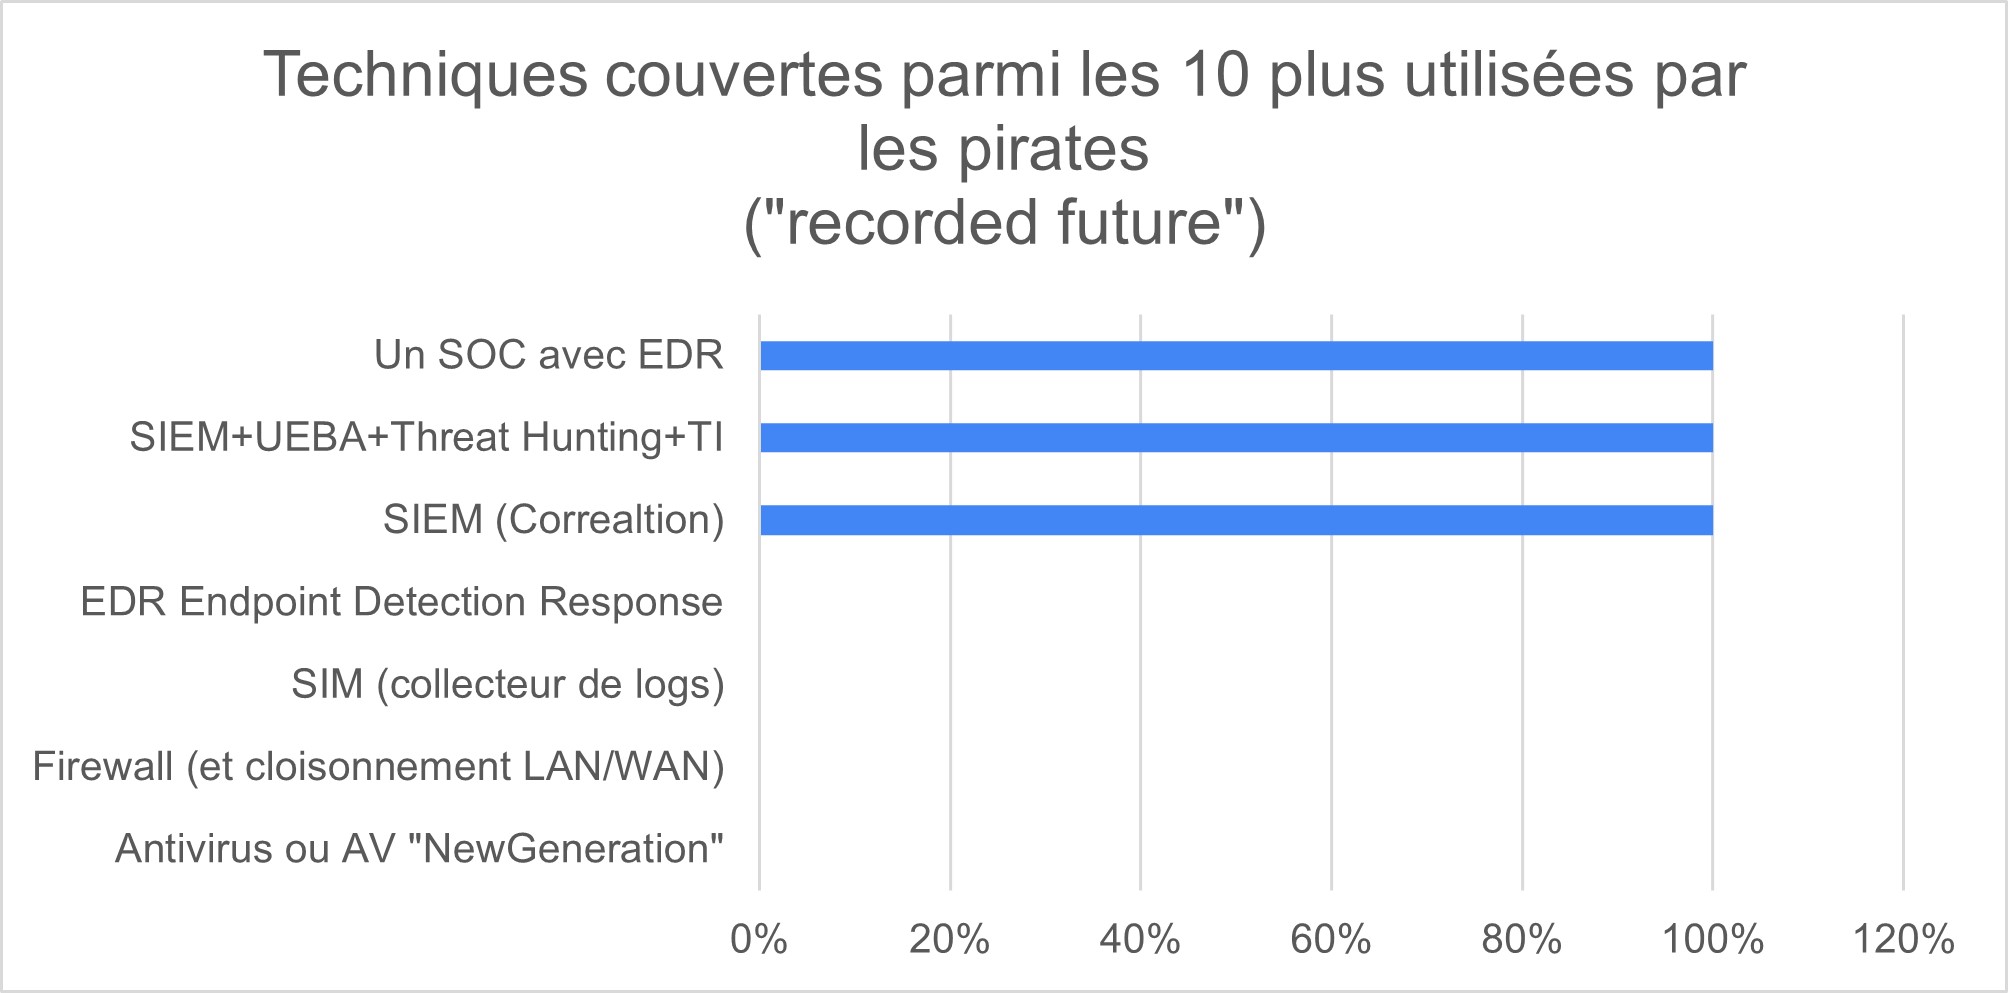
Executive Summary:We observe an almost non-existent coverage rate from firewalls and antiviruses (although they remain essential to mitigate baseline risks. To reiterate: having a firewall and antivirus is an absolute necessity!)
An EDR alone delivers a valuable detection rate, yet will rarely suffice to thwart advanced attacks on its own.
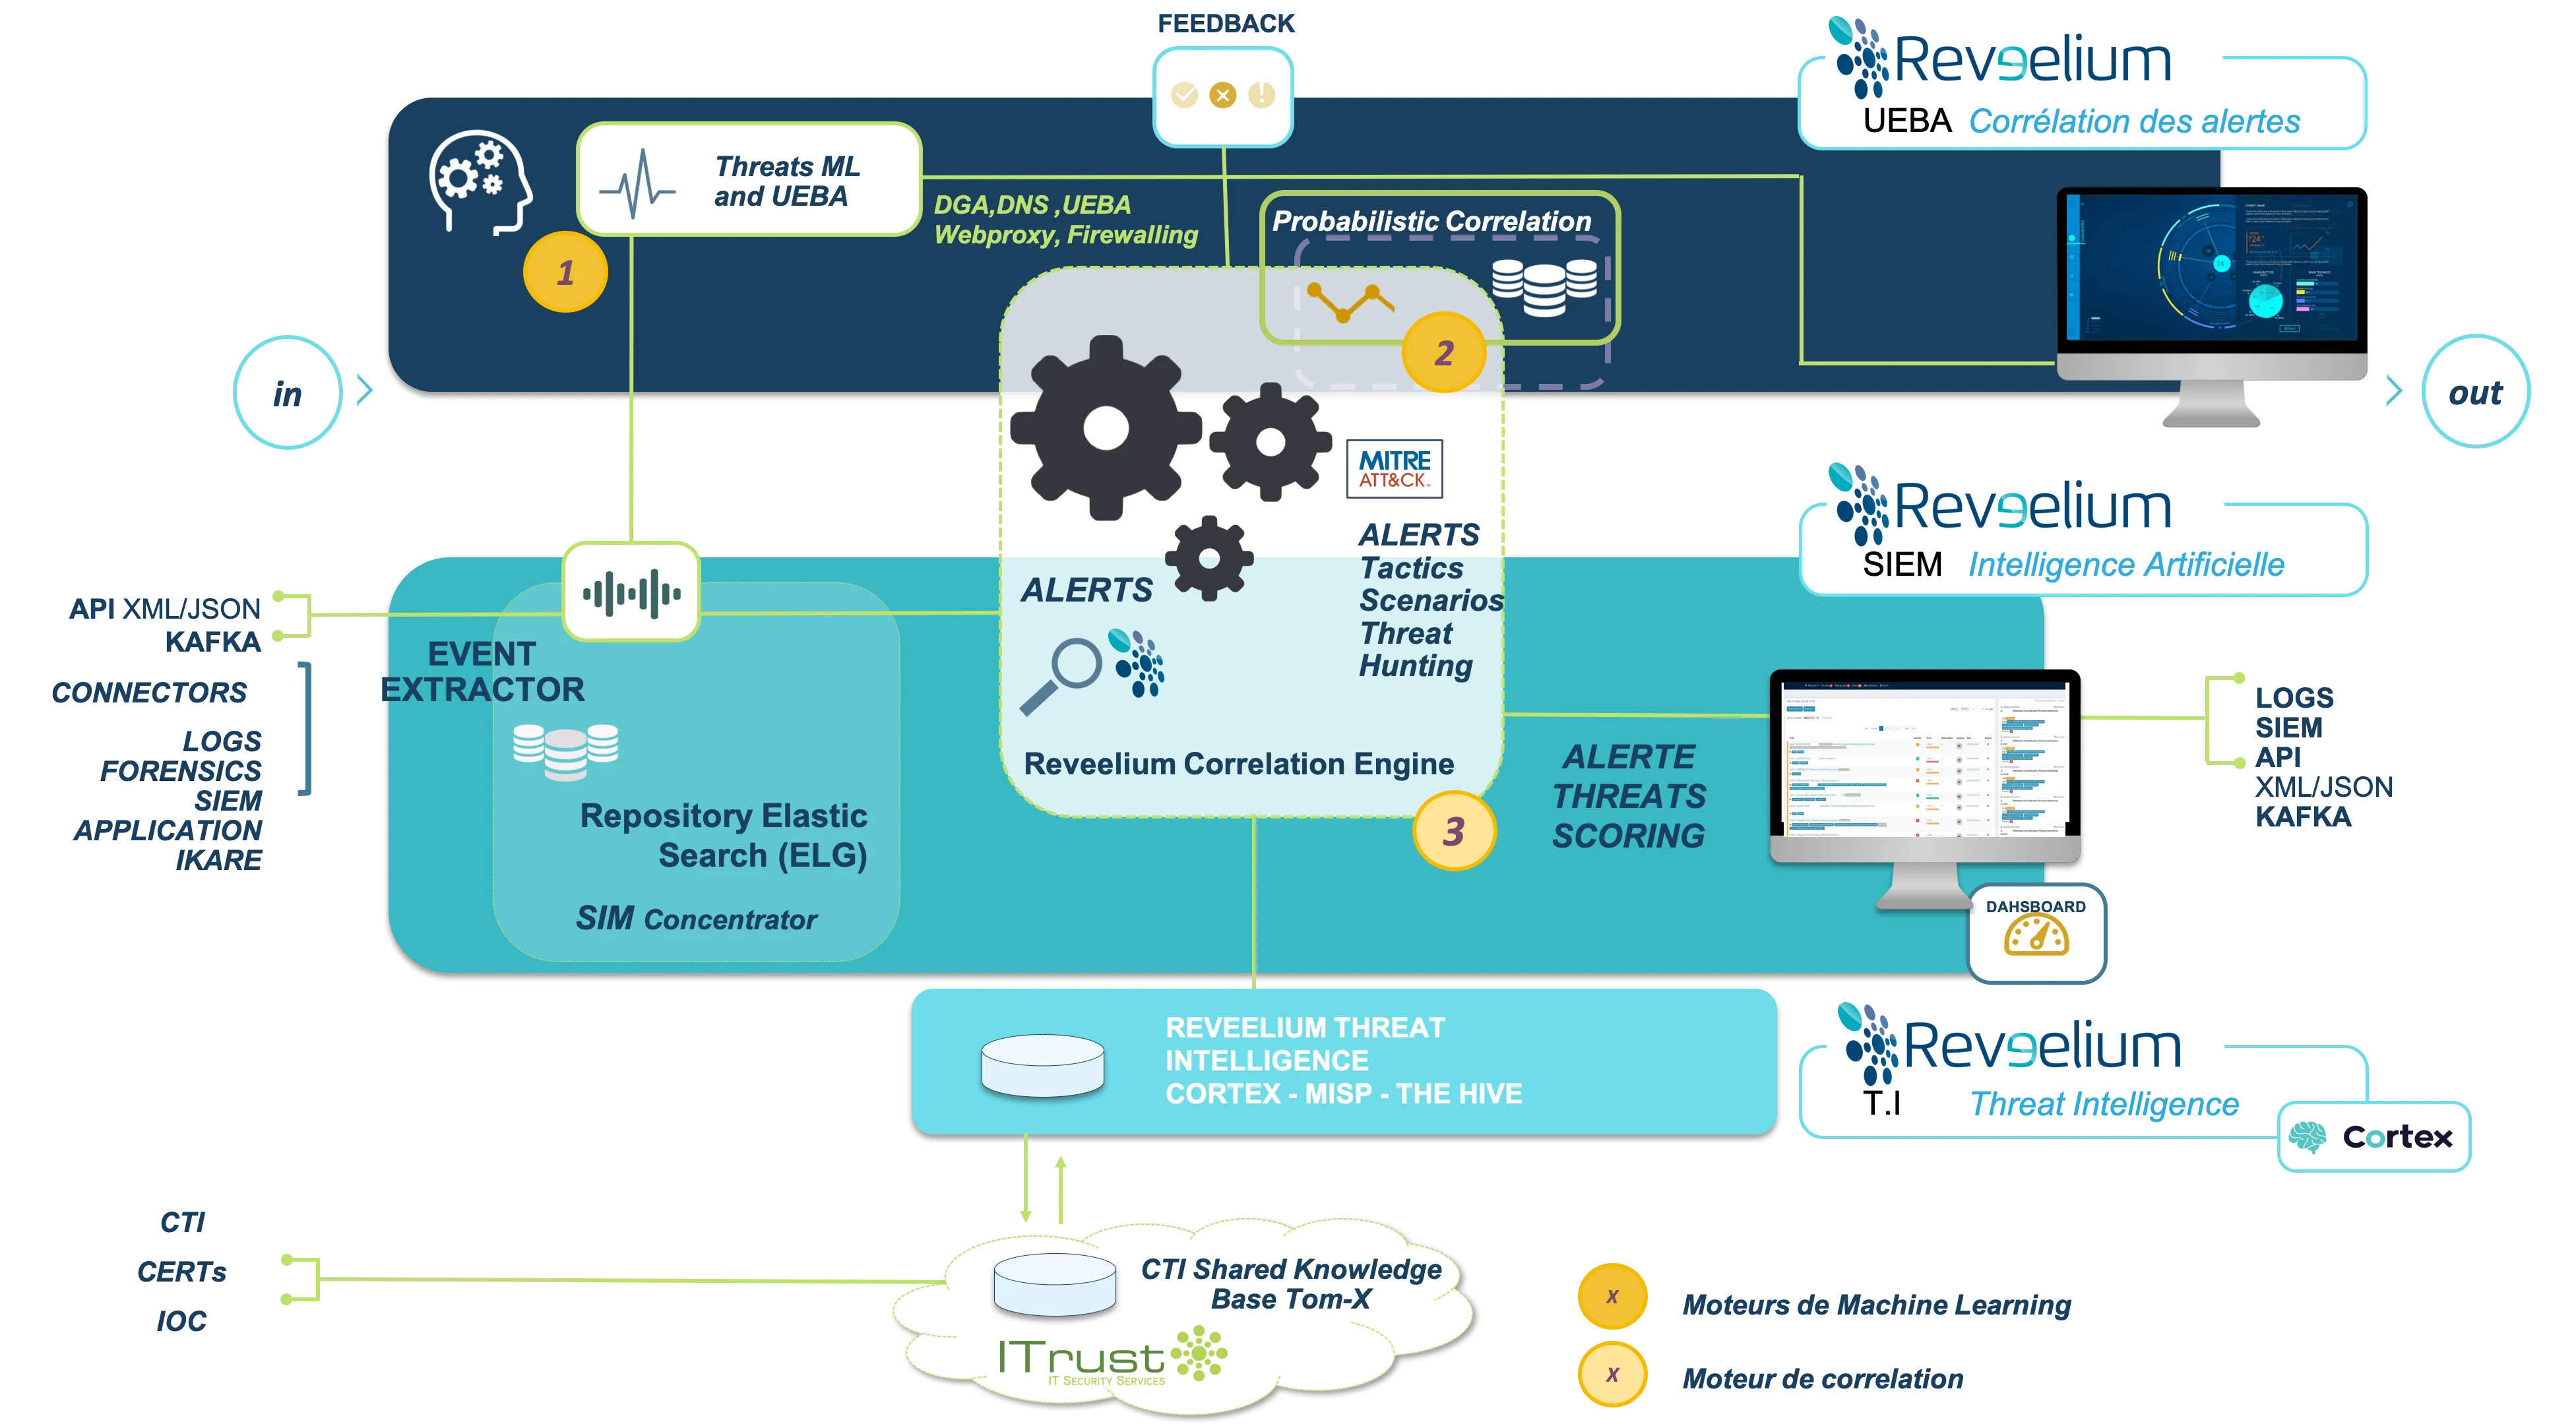
The highest coverage rate is achieved with a SOC powered by SIEM, UEBA, and Threat Hunting. Adding an EDR increases the detection rate by 10% based on the RedCanary study.
Field data and analysis also demonstrate that an anti-phishing/anti-spam solution provides crucial complementary protection. It is not depicted in this table.
A "traditional" corrective SIEM lacking UEBA, artificial intelligence, and Threat Hunting capabilities fails to protect against high-impact attacks.
Cybersecurity: Protection rates of different technology types, according to recent studies – 2020 / ITrust analysis

MITRE Matrix Rankings
MITRE Matrix Rankings by ITrust
Key Takeaways:
Traditional antivirus and firewall tools are no longer sufficient to protect against 2% of modern attacks.
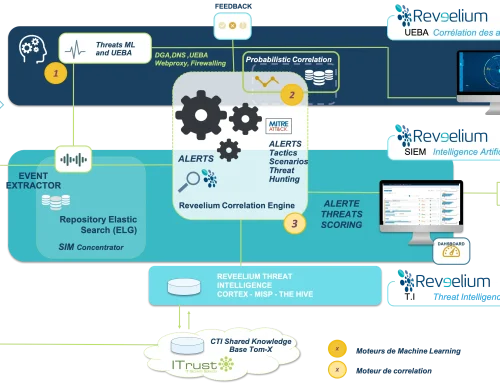
A SOC (Security Operations Center) integrated with a UEBA-enabled SIEM delivers the highest detection efficiency against modern attacks and globally provides the strongest coverage rate.
Complementing a UEBA-driven SOC with an EDR and anti-phishing capabilities is highly relevant. Augmenting a SOC with a vulnerability scanner has become an absolute necessity.
Based on the expertise of ITrust engineers, the recommended defense architecture for any enterprise is as follows:
– A streamlined risk analysis (simplified EBIOS RM)
– A tailored ISSP (Information Systems Security Policy), regularly reviewed and optimized within a continuous improvement cycle
– A dedicated CISO (Chief Information Security Officer)
– A managed SOC incorporating a SIEM with UEBA and Threat Hunting, supplemented by a continuous vulnerability scanner and an anti-phishing solution.
This forms a robust security bundle capable of safeguarding an organization at a very high standard (estimated at 100%. While 100% security is a theoretical metric since absolute zero-risk does not exist, we realistically estimate it at 99%).
We recommend regularly conducting penetration tests and security awareness training, segmenting the information system according to the findings of the risk analysis, adopting sovereign European cybersecurity solutions, and hosting sensitive assets with European cloud providers utilizing European tools and software. Dark web monitoring, vulnerability intelligence tracking, and establishing a relationship with a CERT provide valuable strategic depth to your security posture.
Be vigilant regarding common industry misconceptions: a SIM is not a SIEM; a next-generation antivirus is not an EDR (it merely identifies known signatures, unlike true EDR solutions); an XDR is not an entire SOC, etc.
Approach cyber insurance policies with caution: they currently exclude many threat scenarios and lack market maturity. They will warrant deeper re-evaluation in two years.
Note that 70% of modern SOCs fail to detect emerging threats, largely due to the technological gaps highlighted above, but also from lacking robust monitoring, escalation, and cross-team communication workflows. Robust processes account for 50% of security operational success, according to ITrust experts.
For benchmarking purposes, a standard cybersecurity budget typically represents 7% to 13% of the overall IT budget (varying by industry and enterprise scale). Below this threshold, ensuring reliable defense posture becomes mathematically unsustainable.
In short, an approach that is both simple and effective. We extend our gratitude to ITrust engineers and our clients for this valuable operational feedback.
While certain findings in this article are strictly empirical and substantiated by third-party research, others represent the technical evaluations and informed perspectives of our consultants and subject matter experts—which we welcome discussing. We firmly reiterate that every organization should maintain baseline antivirus and firewall defenses, accompanied by a structured risk analysis to pinpoint critical business assets and services. The objective is not to protect everything uniformly, but to render unauthorized access to high-value assets computationally and operationally prohibitive.
The ultimate goal is to dissuade threat actors, compelling them to redirect efforts toward softer, less-defended targets requiring far less adversary effort.