Since 2018 and the release of the 1st version of Reveelium, the team at ITrust has been convinced of the value of Artificial Intelligence for cybersecurity. In recent years, market trends have proven us right: from SMEs to industry giants, all rely on this technology to increase their threat detection capabilities tenfold.
But what do we mean by AI?
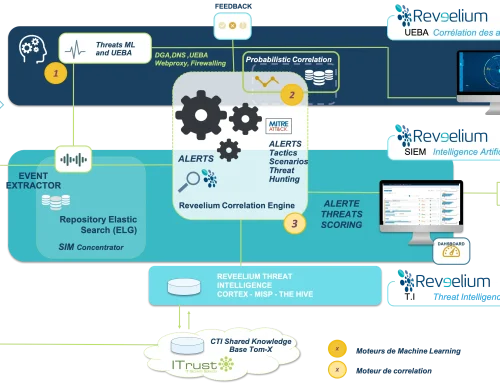
Reveelium is not yet able to think like a human, and therefore does not replace the expertise of an accomplished SOC analyst. That being said, the practice of AI at ITrust goes far beyond the IF/THEN rules, even optimized, that have long been the foundation of this heavily human-supervised decision system.
Making a decision in a predefined situation is not proof of intelligence. Traditionally, SIEM correlation rules are static and fixed. They do not adapt to new situations, nor do they learn from their mistakes.
However, this concept of learning is crucial to detect the multitude of new threats facing organizations, and to counter the increasingly complex and sophisticated attacks of cybercriminals.
In response to this reality, ITrust’s data scientists have been developing our own machine learning algorithms for several years. Their goal: to continuously enhance threat detection by identifying relationships across thousands of logs that a human would not necessarily see.
In a previous post, we discussed the Kryptis malware and how we managed to detect it using the triptych: SIEM UEBA / Threat Intelligence / Human Expertise.
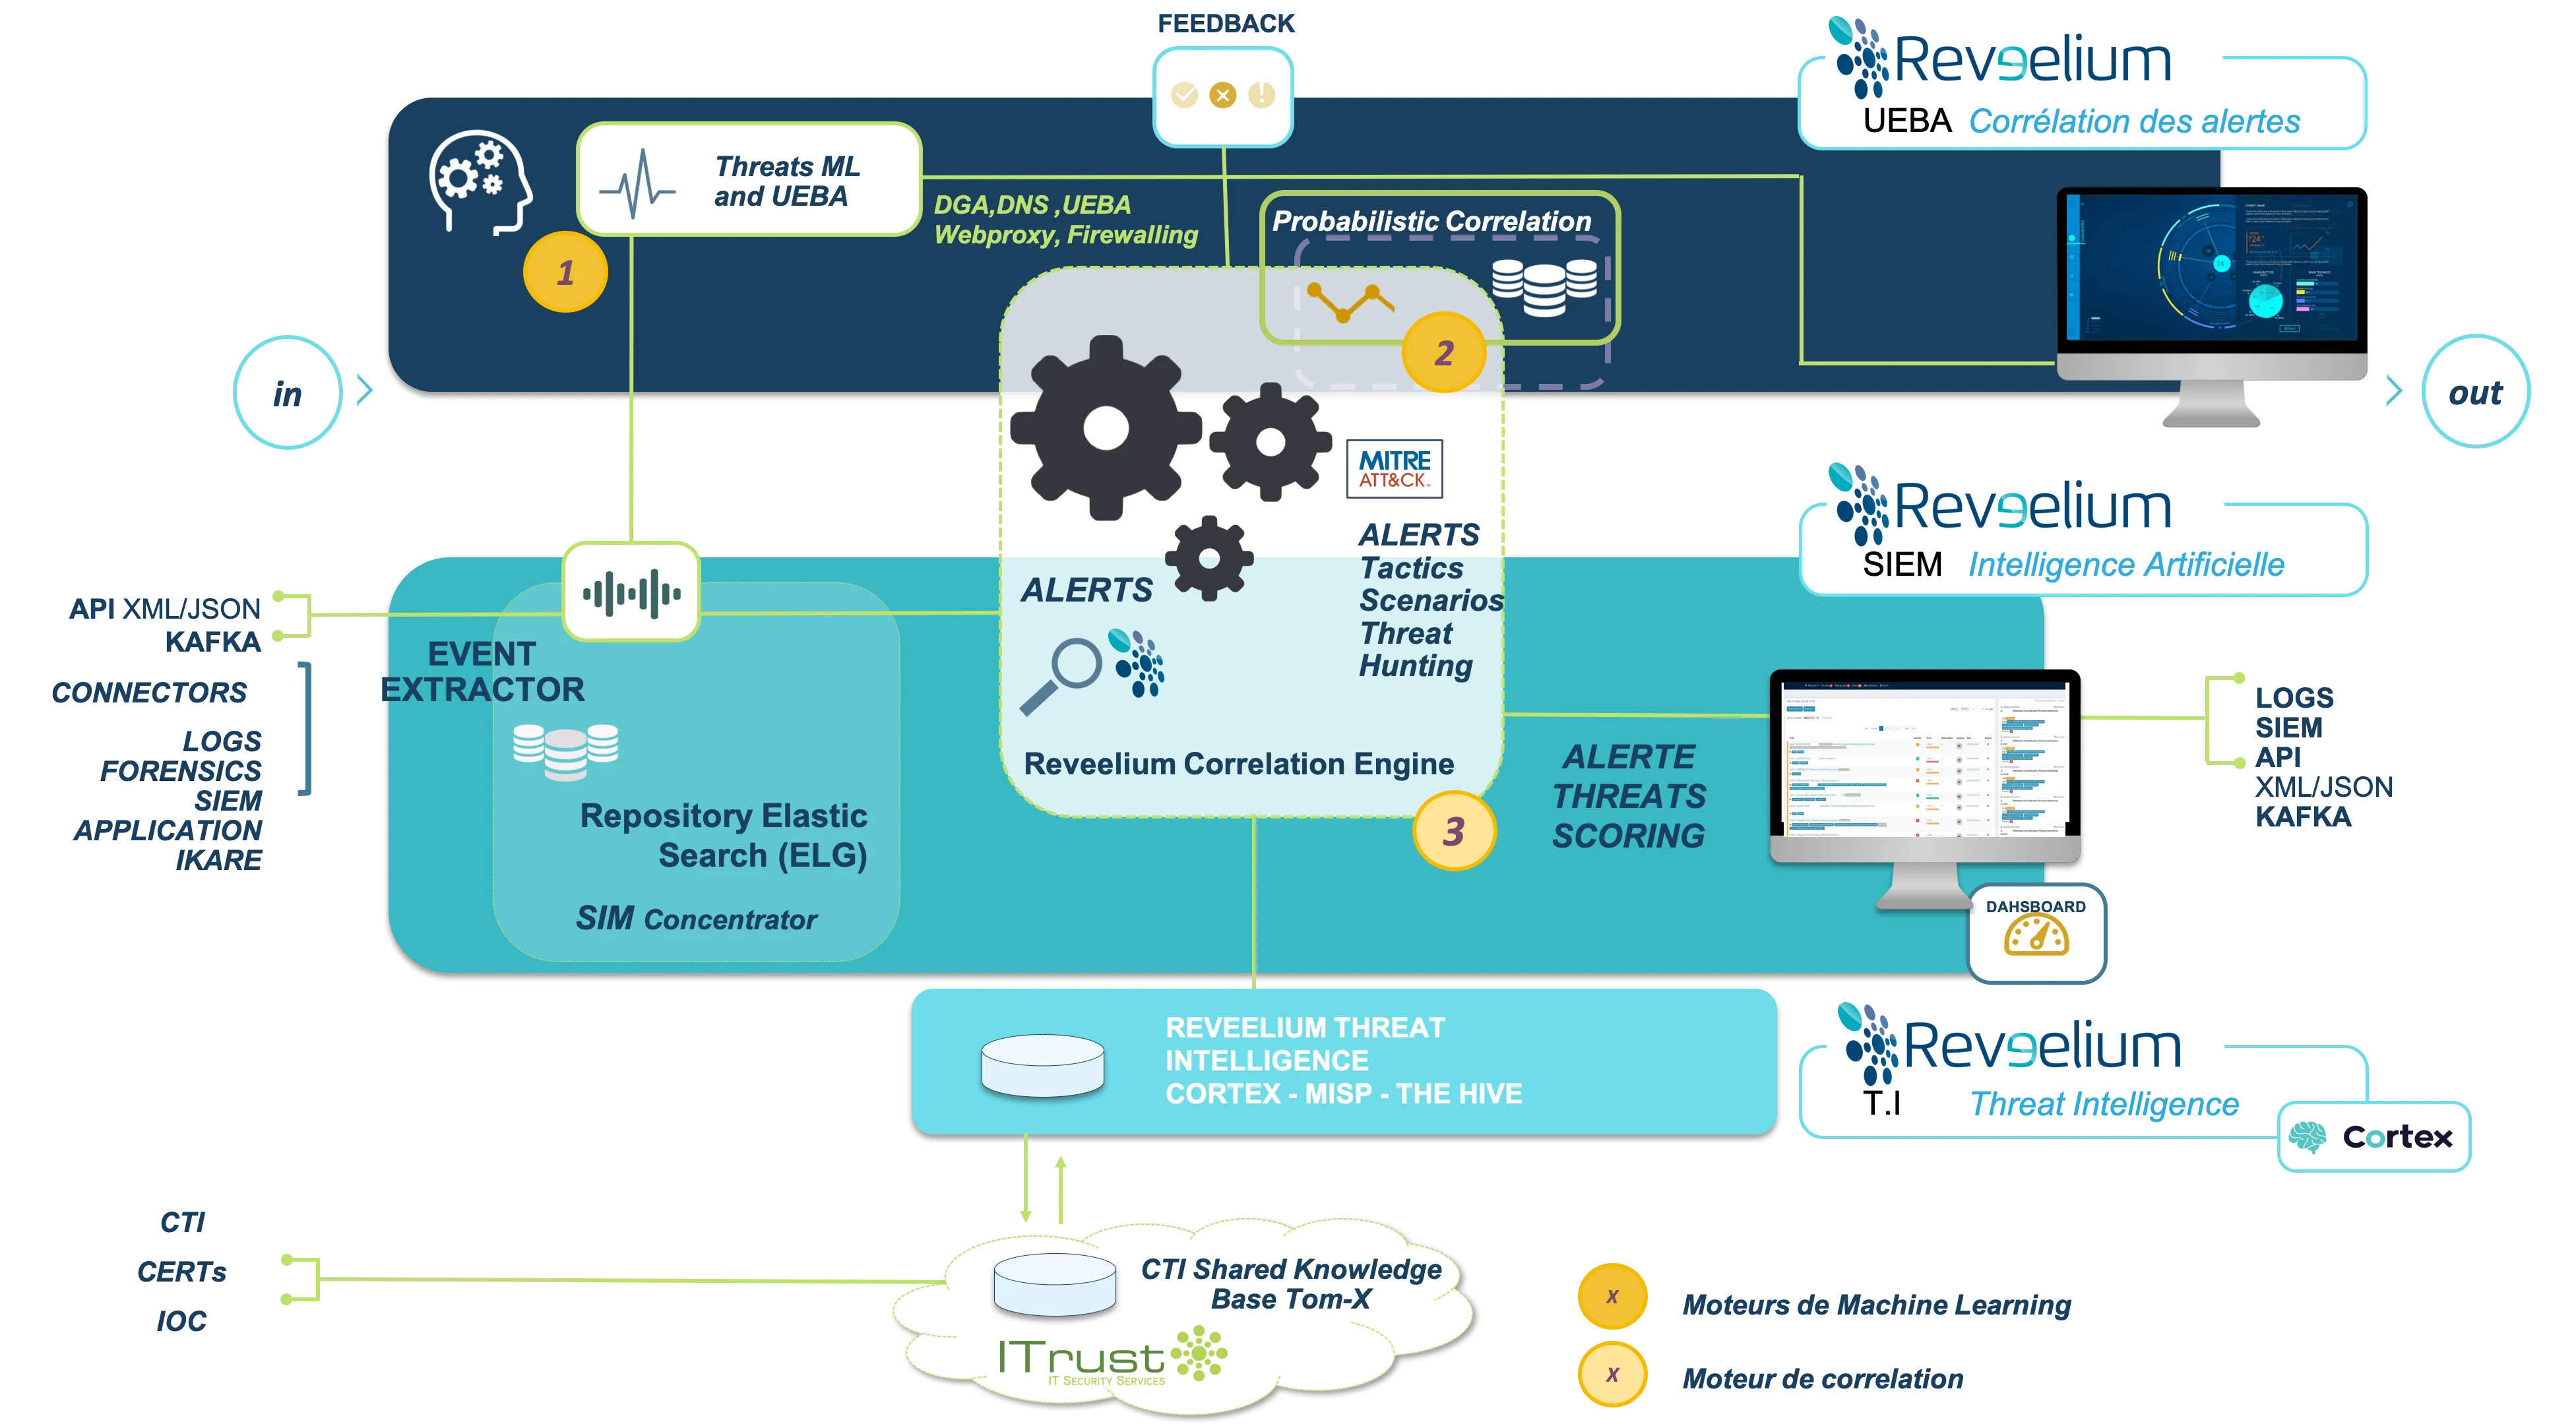
Today, we propose to focus on the UEBA engine of our Reveelium technology by presenting one of these algorithms: the DGA. Without detailing its exact inner workings, we simply explain the temporal and syntactic analysis methods that make this algorithm valuable for malware detection.
Reminder about Kryptis malware:
It is a Trojan (Trojan Horse) that, once installed, can be remotely controlled by the attacker (Command & Control). It is used to exfiltrate information such as usernames, passwords, or sensitive files (exfiltration). It can also capture screenshots, record keystrokes (keylogging), monitor network traffic, execute files… and transmit all this information to a remote server controlled by an attacker.
DGA:
In this cyberattack, our DGA detection algorithm identified the propagation of the Kryptis malware by correlating one of our alerts with SIEM alerts.
But what is a DGA?
A DGA (Domain Generation Algorithm) is a technique used by cyberattackers to generate new domain names for malware Command and Control servers. Detecting DGAs is a critical challenge, as it enables the early detection of both known and unknown malware.
What is the value of AI?
An important question arises: what is the benefit of AI in DGA detection? The answer is straightforward: AI enables a more advanced analysis of domain names. It performs both semantic and syntactic analysis of domain names, thereby allowing more accurate and efficient classification.
Semantic analysis:
Semantic analysis evaluates the pronounceability of a domain name. That is, determining whether the domain name under study is pronounceable or not—and above all, to what degree.
To carry out this semantic analysis, the most frequently used algorithms are deep learning models, specifically RNNs (Recurrent Neural Networks). RNNs are deep learning architectures (Neural Networks) that perform temporal (recurrent) data analysis. The key strength of this algorithm type is its ability to identify the recurrence of specific patterns.
The application of this algorithm in DGA detection is as follows: when examining certain words (from the French or English language) or domain names, patterns emerge, such as consonant/vowel alternation.
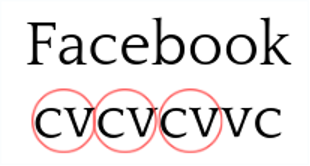
Observation of patterns in a normal domain name. c = consonant / v = vowel / red circle = pattern to observe
However, most of the time when analyzing DGAs, this vowel/consonant alternation pattern is absent.
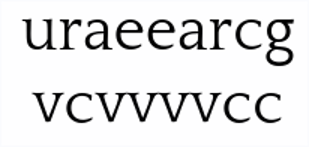
Example of a DGA where no pattern with consonant and vowel alternation is found. c = consonant / v = vowel
It is the presence (or absence) of this pattern that the RNN detects, enabling it to determine the pronounceability of words and, consequently, classify them—or not—as a DGA.
Syntactic analysis:
Another way to detect DGAs is through a syntactic approach. This approach enables the analysis of the domain name's content. Content analysis can be performed, for example, by counting the number of vowels or consonants it contains.
In this type of approach, we define a set of features that characterize the domain name. These features can be relatively simple, such as the vowel/consonant count in the domain name, or more complex. All these features are then fed into a machine learning algorithm that learns to distinguish legitimate domain names from DGA-generated domain names.
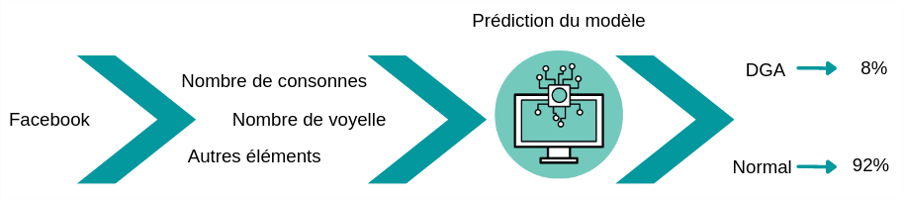
Our method:
ITrust’s algorithm combines both dimensions: semantic analysis and syntactic analysis. This means that, to detect DGAs, we perform a dual analysis ensuring no aspect of the domain names goes unmonitored.
Furthermore, our algorithms are trained on ITrust’s proprietary databases, ensuring high reliability for our algorithm results. The larger the volume of training data, the more robust the algorithms become.
AI: the cornerstone of contemporary cybersecurity
In conclusion, this post illustrates the value of machine learning techniques in cybersecurity. They enable an in-depth, multi-dimensional analysis of data (here, syntactic and semantic, to evaluate domain name structure and pronunciation). User demands and digital needs continue to grow, expanding the perimeters requiring supervision—which are increasingly exposed to vulnerabilities. Faced with this mounting complexity, the advantages of machine learning justify its phased replacement of traditional methods:
Analyzing massive volumes of data in an automated manner
Accelerating threat detection (a few days, compared to several months with legacy methods)
Identifying correlations within this data that an analyst might miss; uncovering unknown threats
Delivering significant time savings to focus on analyzing critical threats, while minor alerts are triaged by AI.
Author: J. Johann – Data Science Team at ITrust