Beyond the barrier gestures we know so well and practice daily to protect each other's health, there are some that concern the health of our… companies!
I will try to answer many of the current questions these companies have, using factual field data generated from the 350 clients of ITrust, the cybersecurity company I lead. This opinion piece may seem naive, but its primary ambition is educational.
The unprecedented and brutal economic and social situation, which could at the very least be described as tense, has created a new risk that has become glaringly obvious in recent months.
The number of attacks, data thefts, and viruses is literally skyrocketing. It is harder to find a company that has not been impacted than to find examples of affected organizations.
ITrust teams are observing a 400% increase in attacks compared to the same period in 2019.
ITrust's teams have observed a 400% increase in attacks compared to the same period in 2019.
Since early 2020, certain sectors have been especially targeted: healthcare, high-tech industry, government agencies, and law firms. Piracy, espionage, theft, and extortion attempts are the daily reality for these organizations, originating mostly from:
- Professional hacker groups—true “mafias” often shielded or tolerated by their host countries: Brazil, Russia, China, Korea, Indonesia, Pakistan, the United States, Vietnam, Iran.
- Opportunistic hacker groups: primarily specializing in phishing scams, often operating from Africa or South America.
- Individuals or small-scale entities specialized in spear-phishing or fake social media profiles.
- Nation-states themselves… (5 countries worldwide have an official offensive cyber force)
- Freelance hackers, students, rogue actors, activist experts, etc.
Most of them operate on behalf of governments or corporations. States leverage these “mafia” syndicates to serve their geopolitical interests, conduct subversive operations against competitors, steal technology, or weaken a target country. In the digital Caribbean seas, allies and enemies blur. Pirates, buccaneers, and privateers are best equipped to pillage colonies without facing state discipline.
Because… the piracy business is highly lucrative.
In 2017, the black market price of a digital medical record was $15, while a stolen credit card fetched €1.
In March, a hacker group demanded $6 million to avoid leaking data stolen from a well-known construction firm.
This business model can yield immense profit margins and, unlike our traditional companies, requires an initial investment of only a few thousand euros.
Assemble a small team of experts and the operation is set. Staggering net profits, completely tax-free, exempt from VAT… they even offer enticing promotions: a 10% discount for immediate payment! Not to mention an “original” after-sales service, to say the least: advice on how to avoid getting breached again! True professionals, indeed…
In the technology sector, we rely on concrete metrics, which is why we analyzed those of our own clients.
Concrete, real-world operational feedback.
100% of our clients are subject to continuous attacks. However, a clear distinction must be made between:
- Attempted attacks (firewall port scans, intrusion attempts) that target 100% of companies but fail to breach defenses (in our jargon: cold attacks)
- Active ongoing attacks: the threat has infiltrated the organization and is propagating, but carries no active payload yet or has not managed to cause an impact. Here again, 100% of our clients have experienced an infection at some point! (hot attacks)
- Successful attacks that cause tangible financial or operational damage: ransomware demands, malware disruption, data theft, service downtime (these are qualified attacks)
Naturally, many organizations prefer not to disclose these incidents, and we strictly honor that confidentiality.
Among those that have suffered successful attacks, the damage is distributed as follows:
- 75% experience service degradation
- The average cost of a successful attack is estimated at €1.2 million for a mid-market enterprise (ETI).
A direct parallel can be drawn between the cost of security measures—implementing barrier controls—and the financial impact of a successful breach. On average, a client invests €25k per year in cyber defense, thereby mitigating an expected loss exceeding one million euros.
Put simply, every euro invested in cybersecurity prevents a loss of €40, with a 100% success rate. Cybersecurity shifts from a cost center to a high-yield investment.
Did you know that the majority of suspicious attacks originate internally?
The most prevalent attack vectors are phishing / malware (90%), internal denial of service, and application or network vulnerabilities.
The highest-impact vectors include: DGA, DNS tunneling, XSS, default guest accounts, and unencrypted, easily accessible Active Directory password databases. (See ITrust’s white paper on the top 10 security vulnerabilities link)
This points to a vital finding: we can derive empirical safety measures capable of neutralizing, according to our data, more than 90% of malicious activities!
These extend far beyond basic hygiene guidelines, such as enforcing strong passwords (a clever mix of numbers and special characters that remains memorable), eliminating default credentials on devices and applications (which we still encounter far too often!), or patching software and systems regularly.
Let’s call these fundamental hygiene rules, to continue our opening parallel. It is critical to adopt more advanced, technical protective measures. While 100% of companies face threat attempts and 78% sustain compromised incidents,
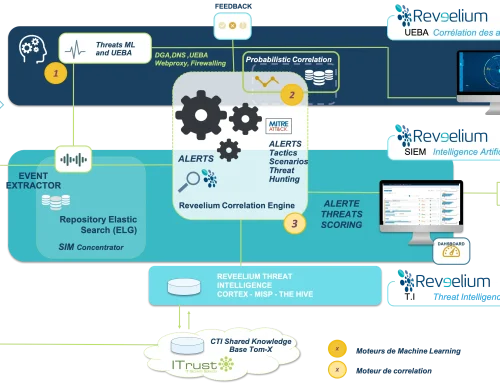
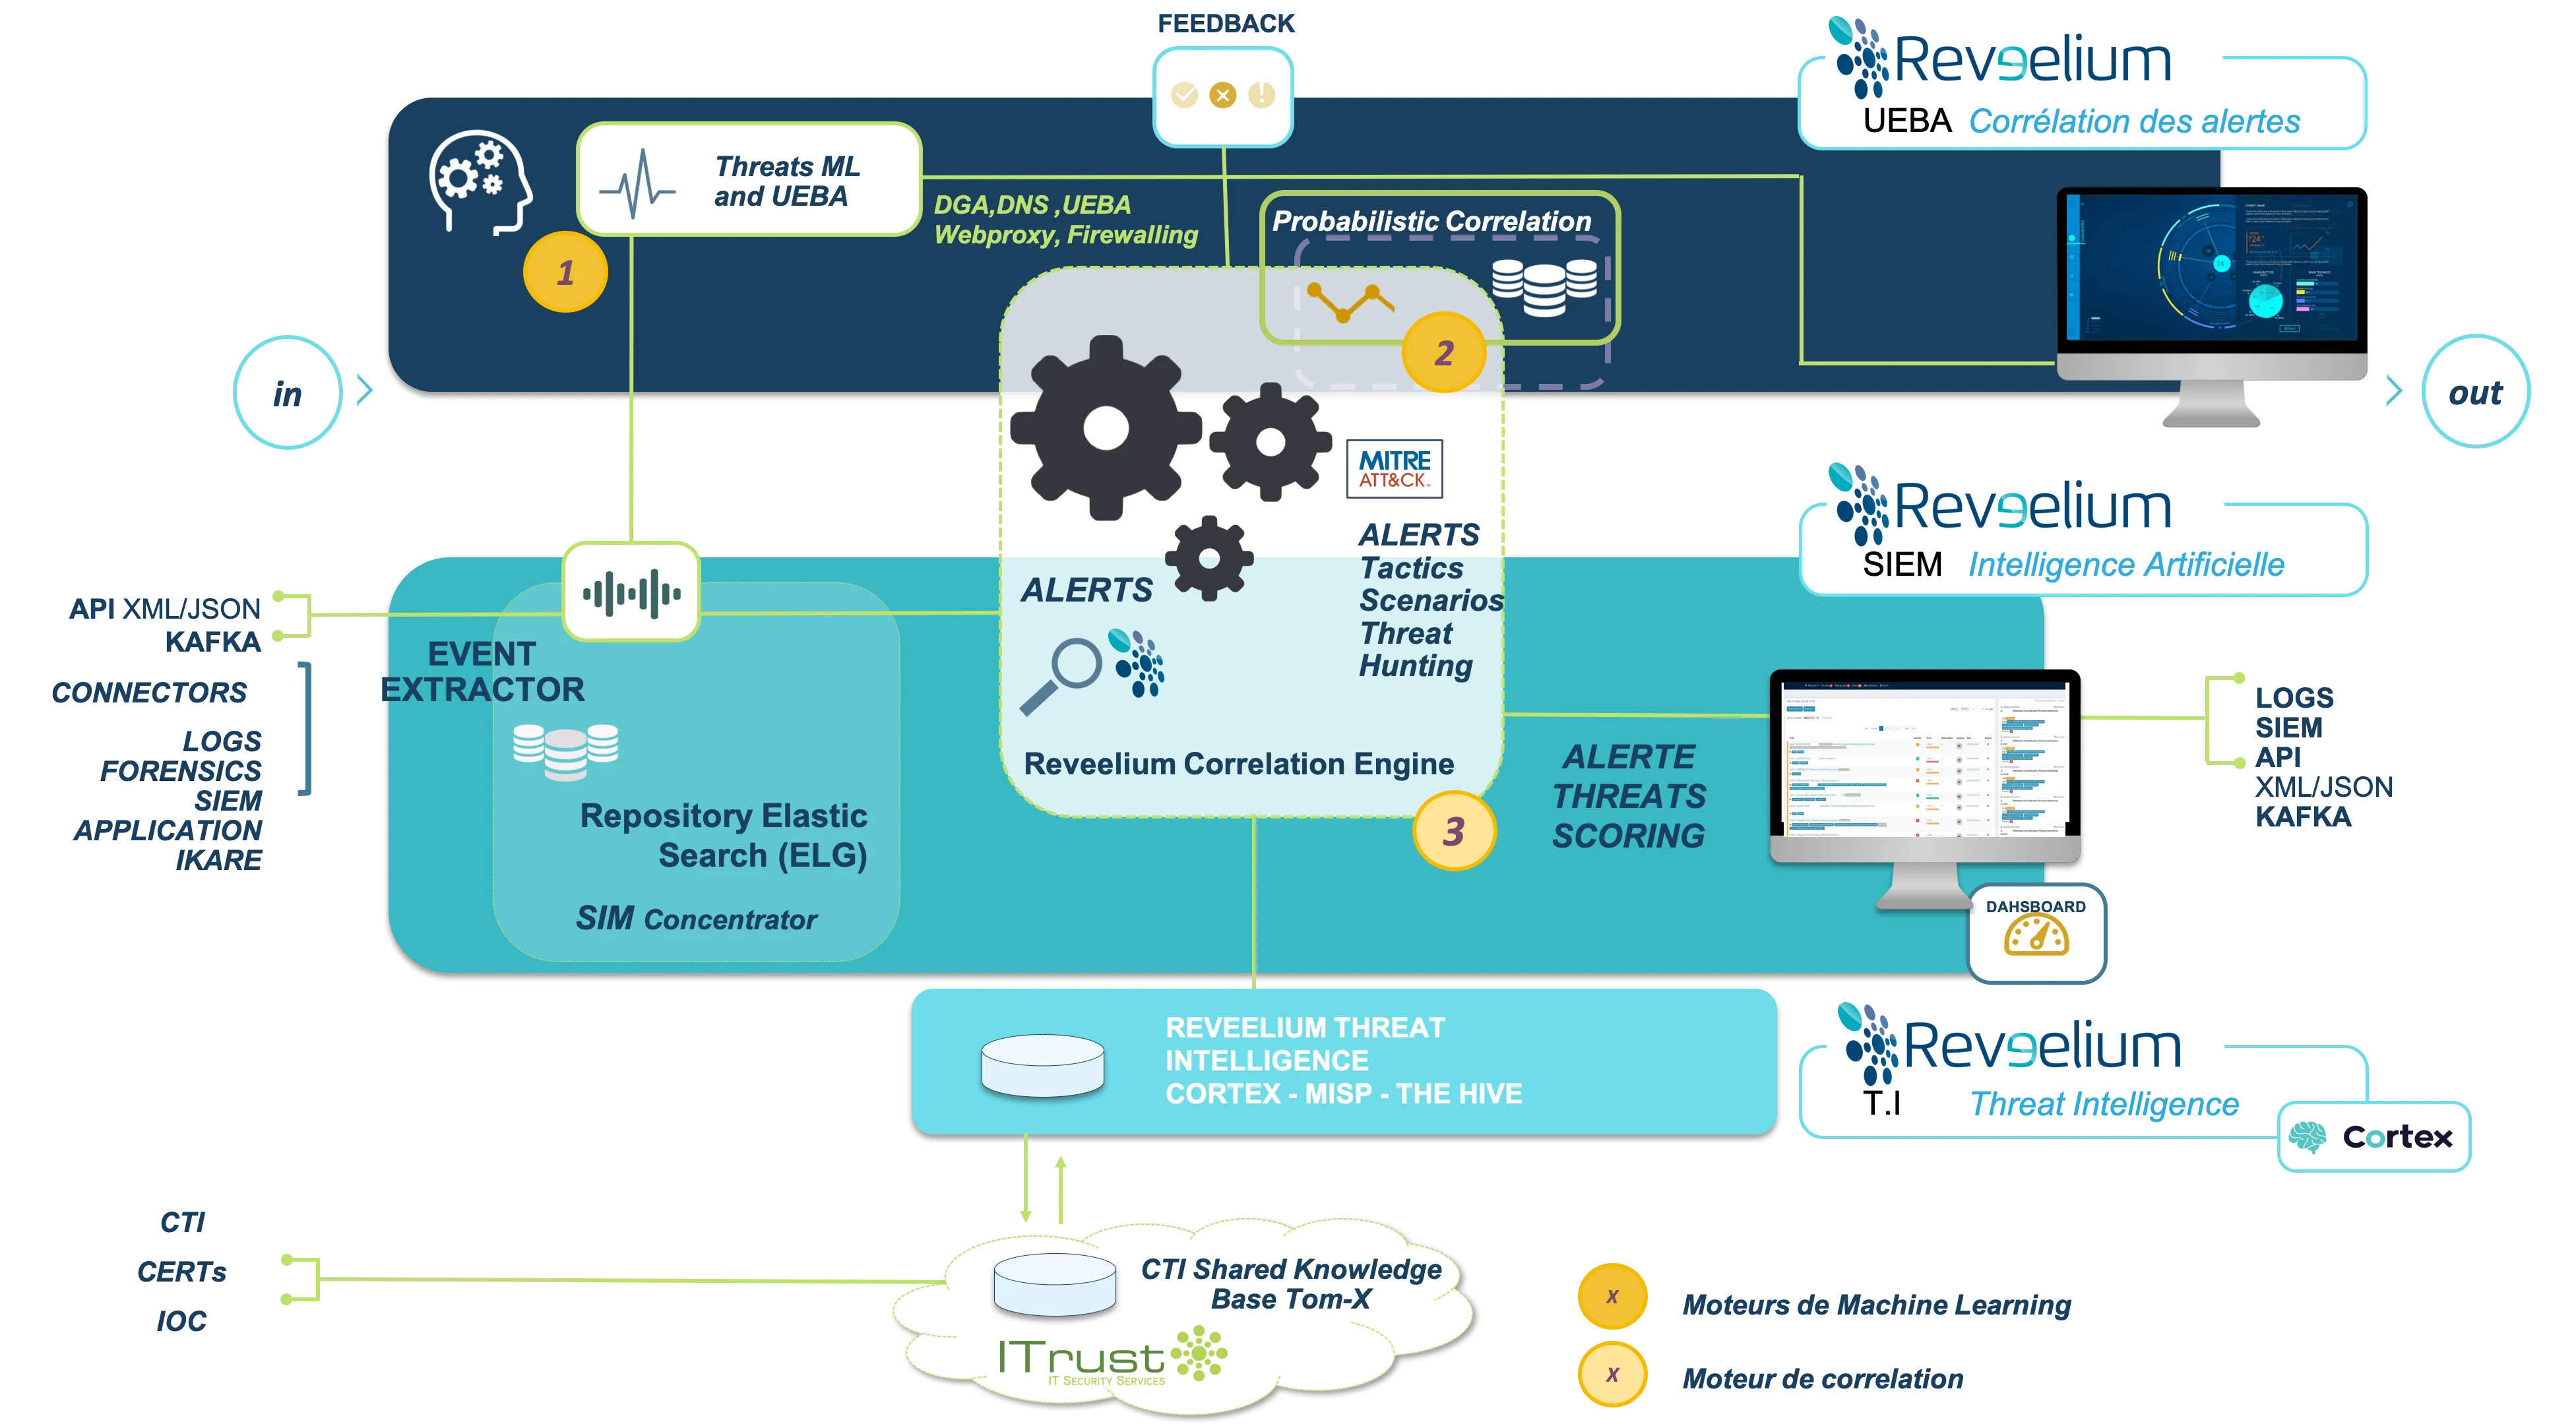
YET none (0%), absolutely none, suffers a successful attack when its perimeter is proactively monitored through continuous vulnerability assessments and a SOC. (ITrust client statistics over 2 years, covering more than 300 clients).
YET none (0%), absolutely none, suffers a successful attack when its perimeter is proactively monitored through continuous vulnerability assessments and a SOC. (According to ITrust client statistics over 2 years, covering more than 300 clients).
It is therefore high time to deploy a vaccine that is, in this case, already fully operational.
To facilitate its deployment across all organizations, support executives in this strategic initiative, restore the peace of mind required to focus on business resilience and growth, and relieve them of undue liability through pragmatic, robust, and accessible support during these uncertain times.
Pointing fingers only leads to fragmentation and harm.
Safeguarding our expertise and domestic capabilities has become an absolute priority. While it may seem less visceral than this virus that directly impacts our families and communities, it is just as insidious, leaving lasting damage on employment and our economic fabric—which certainly cannot bear additional strain.
At ITrust, we have developed agile, tailored, specialized solutions. Yet to defend companies effectively, financial resources must be allocated, which are currently being channeled—often understandably—into other emergency priorities. However, time is not on our side, and cybercriminals show no empathy. They exploit the storm to profit at the expense of our businesses, the true engines of future value creation.
In the midst of the COVID crisis, we all recognize the necessity of barrier measures, of giving purpose to our actions, and of protecting our loved ones. We are confronting unprecedented events that can permanently alter our trajectories.
A biological virus? A digital one? An enterprise losing its intellectual property and jobs, impacting the next generation working within it? If the modest cost of a mask or sanitizer is obvious compared to the vital protection it affords our daily lives and loved ones, the exact same logic applies to cybersecurity: safeguarding our digital perimeter is far more critical and central than most realize.
“Protection has a cost. Neglecting it costs far more.” Q.E.D.
Jean-Nicolas PIOTROWSKI – Founder of ITrust