


Freebox Pro: How Artificial Intelligence enables automated anomaly detection
ITrust's SOC (Security Operations Center) teams rely on our Reveelium tool, which incorporates powerful proprietary algorithms and artificial intelligence [...]
New Freebox Pro: how ITrust leverages Threat Intelligence resources to ensure your protection
Launched on January 14, the new Freebox Pro includes numerous innovations to optimally secure your business. Among others, a database of [...]
ITrust x Free Pro: New Freebox Pro cybersecurity!
The New Freebox Pro: A Blend of Technology and Security for Businesses. Performance, security, and innovation: the new Freebox Pro pushes boundaries to support [...]
Focus on Perfctl: The Malware Targeting Linux Systems
Perfctl is a relatively recent malware that has rapidly demonstrated its ability to infiltrate complex environments, especially enterprise Linux servers. Over the past three to [...]
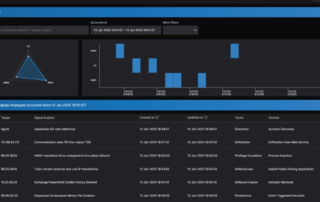
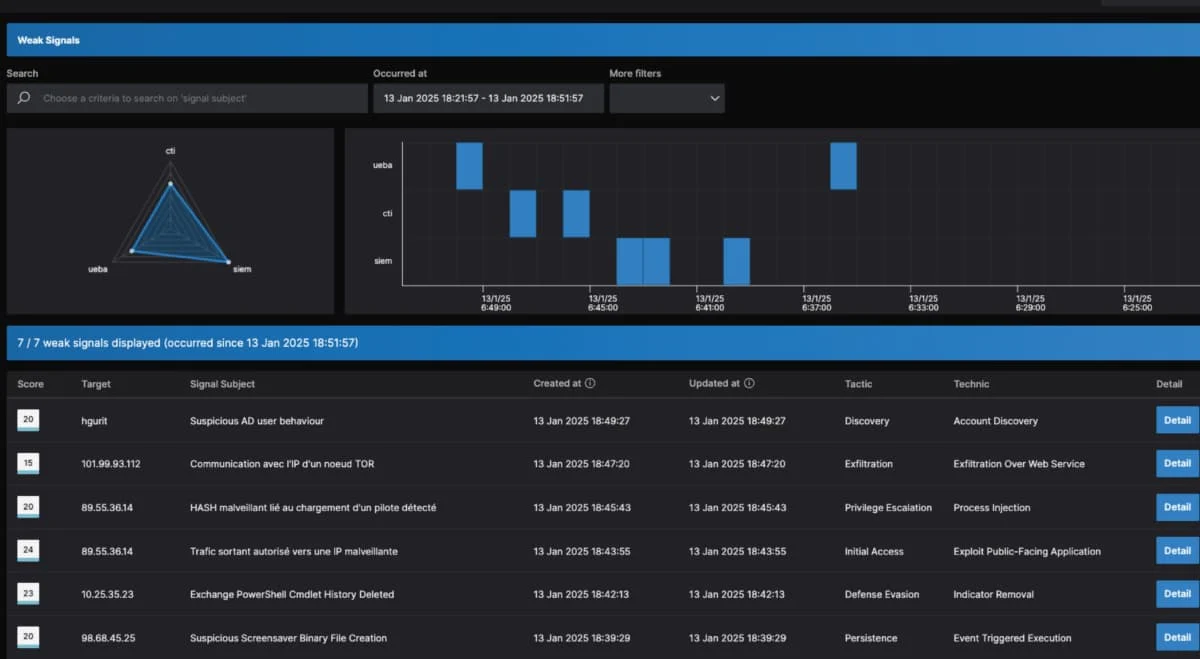
Reveelium Features: The Weak Signals database
Weak Signals: a major breakthrough in Reveelium V12. One of the main challenges of Reveelium version 12 was to redefine the threat qualification framework. The [...]
How Reveelium, the French SIEM XDR, leverages the MITRE ATT&CK® framework to strengthen its detection capabilities
Adopted by thousands of organizations worldwide, the MITRE ATT&CK knowledge base is regularly updated to reflect the latest evolutions in cyber threats thanks to [...]
MitM Attack Focus: Evil Twin
The Evil Twin attack is a type of Man-in-the-Middle (MitM) attack targeting public Wi-Fi networks. Its name comes from the fact that an attacker creates [...]
Malware Spotlight: Agent Tesla
Agent Tesla stands out as an advanced Remote Access Trojan (RAT), frequently utilized for malicious purposes. This malware, operating as both a keylogger and an information stealer, is capable of [...]
Malware Spotlight: Steelfox
In current cyber news, one name is causing both intrigue and concern: Steelfox. This malware, with its enigmatic name evoking steel and vulpine cunning, perfectly symbolizes [...]
Malware Spotlight: The Zergeca Botnet
Zergeca is a type of malware discovered in 2024. It is a network of infected devices (botnet) designed to launch DDoS (Distributed Denial of Service) [...]