About ITrust

This author has not yet filled in any details.
So far ITrust has created 141 blog entries.

RaaS Group Focus: Play

Since its emergence in 2022, the Play group has established itself as a major player in the ransomware landscape. Operating under a Ransomware-as-a-Service (RaaS) model, Play targets organizations across diverse sectors, primarily in North America, Europe (notably Germany and France), and Latin America. The group is recognized for its advanced intrusion techniques, its reliance on living-off-the-land binaries (LOLBins), and its double-extortion strategy. Tactics, Techniques, and Procedures (TTPs) of Play 1. Initial access and privilege escalation Play exploits known vulnerabilities to breach target systems, notably: Fortinet SSL [...]
RaaS Group Focus: Play2025-10-23T16:11:28+02:00

8 Signs It's Time to Change Your SIEM

A SIEM (Security Information and Event Management) solution is one of the pillars of your cybersecurity strategy. However, like any tool, a SIEM can become an impediment if it no longer keeps pace with current security, performance, and compliance requirements. Here are 8 signals—sometimes critical—indicating that it may be time to replace your current SIEM. 1. Your SIEM no longer keeps up with evolving threats If your team struggles to adapt the SIEM to new attack vectors (sophisticated ransomware, lateral movements, stealth exfiltration, insider threats), it means your solution lacks flexibility or [...]

8 Signs It's Time to Change Your SIEM2026-09-16T17:06:28+02:00

How does Threat Hunting accelerate incident response?

Threat Hunting is a core pillar of the ITrust SOC: technical, strategic, and resolutely proactive. This threat hunting shortens incident response times, curbs dwell time, and enhances Reveelium's detection capabilities by enriching the data analyzed during hunting sessions. Methodology, operational processes, feedback: step inside the daily operations of a Threat Hunter. Threat Hunting vs. Threat Intelligence While fundamentally distinct, these two disciplines are complementary. Threat Hunting explores, Threat Intelligence enlightens, and together, they mutually enrich one another to reinforce the defensive posture against increasingly complex threats [...]

How does Threat Hunting accelerate incident response?2025-10-23T16:11:58+02:00

Ransomware Group Focus: Inc Ransom

Inc Ransom does not stop at encryption: it orchestrates its attacks as a service, leveraging structured methodologies, professional tooling, and an exfiltration strategy designed to bypass traditional defenses. In just a year and a half, this emerging threat actor has already struck more than 220 organizations. In this article, we provide an in-depth analysis of their operating procedures, initial access, persistence, and impact tactics, as well as the technical mechanisms deployed to evade detection and coerce victims. A well-oiled model, from phishing to encryption The Inc Ransom group operates according to a classic yet ruthlessly effective cyberattack schema, combining [...]

Ransomware Group Focus: Inc Ransom2025-10-23T16:12:03+02:00

ITrust showcases its new collaborative French XDR platform at the InCyber Forum

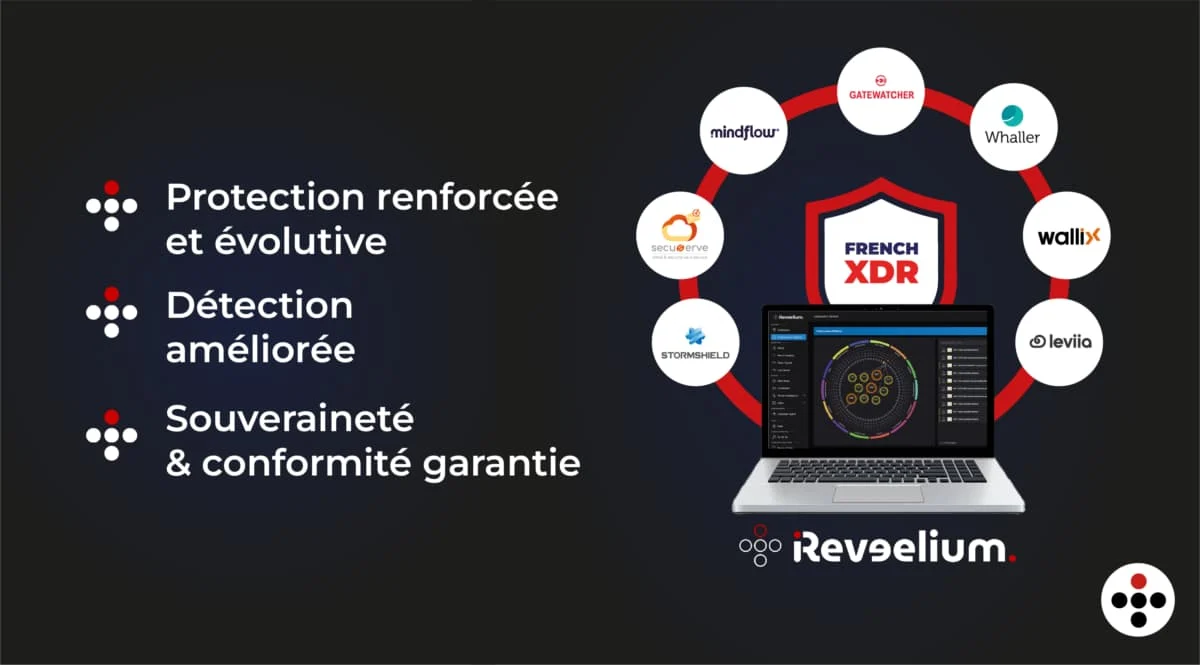
ITrust, a leading cybersecurity authority for 18 years and the B2B cybersecurity center of expertise of the iliad Group, will present its new French XDR platform at the InCyber Forum, to be held in Lille from April 1 to 3. Through its shared and intelligent approach, this 100% sovereign solution represents a major breakthrough for companies and organizations looking to strengthen their cybersecurity posture. A major innovation for French cybersecurity ITrust spearheaded the French XDR collaborative platform, which aggregates the services of several specialized French cybersecurity partners, thereby enabling enhanced threat detection, faster [...]

ITrust showcases its new collaborative French XDR platform at the InCyber Forum2026-04-14T09:29:11+02:00

Cybersecurity in Transportation: Challenges, Threats, and Solutions

The rapid digital transformation of the transport sector has profoundly reshaped technical infrastructures, management methods, and user interactions. While this modernization has delivered agility, efficiency, and connectivity, it has also introduced massive exposure to cyber threats. Transport operators are now prime targets for threat actors. Particularly vulnerable critical infrastructures In modern transport systems, IT and OT networks are now interconnected. Embedded software, ticketing platforms, cloud infrastructures, IoT sensors, fleet management, remote monitoring... All these components expand the attack surface. The growing complexity of architectures [...]

Cybersecurity in Transportation: Challenges, Threats, and Solutions2026-04-14T08:51:42+02:00

Zero Trust: Essential Paradigm or Passing Trend?

At a time when cyber threats are proliferating and traditional IT perimeters are dissolving, the Zero Trust model is establishing itself as an imperative for businesses. But is it truly a strategic evolution or merely a passing trend? An in-depth look. A trend firmly establishing itself within organizations With 30% of organizations already committed to a Zero Trust strategy in 2024, and 27% currently deploying one (source: Statista), the trend is unequivocal: this model is becoming the standard. It is neither a buzzword nor a technological utopia. It serves as a lever for secure digital transformation, [...]

Zero Trust: Essential Paradigm or Passing Trend?2025-10-23T16:13:39+02:00

Cyber Threat Landscape in the Healthcare Sector: Analysis of the ANSSI Report (2024)

Today, the healthcare sector is one of the most exposed to cyberattacks. The criticality of infrastructures, the sensitivity of medical data, and the proliferation of connected devices make it a prime target for cybercriminals. The French National Cybersecurity Agency (ANSSI) has just published an assessment of cyber threats in this sector, shedding light on recent trends and upcoming challenges. A sector under high digital pressure ANSSI highlights the fragmentation and heterogeneity of healthcare stakeholders, making homogeneous IT systems security difficult to achieve. This sector notably encompasses: [...]

Cyber Threat Landscape in the Healthcare Sector: Analysis of the ANSSI Report (2024)2026-04-14T09:42:25+02:00

Renewal of our PASSI qualification

We are proud to announce the renewal of our PASSI RGS (Information Systems Security Audit Provider) qualification, awarded by the French National Cybersecurity Agency (ANSSI). This accreditation testifies to our compliance with the most stringent security audit standards and our ability to effectively support organizations in safeguarding their information systems. Valid from January 21, 2025, to January 20, 2028, this renewal is the culmination of a rigorous assessment process attesting to the technical expertise of our teams and our alignment with the regulatory and methodological standards required by ANSSI. A strict regulatory framework [...]

Renewal of our PASSI qualification2026-02-17T16:34:00+01:00

Freebox Pro: Behind the scenes of the alert emails you receive

As soon as a malicious flow is identified entering your local network or malicious traffic is generated from your local network, you receive an automated alert. This alert is sent via email complete with diagnostics and recommendations for remediation actions. Behind this seemingly straightforward process lies a cyber acronym: SOAR. Explanations. SOAR: definition The acronym SOAR (Security Orchestration, Automation, and Response) describes technologies that safeguard information systems against threats. Integrated into our Reveelium tool [...]

Freebox Pro: Behind the scenes of the alert emails you receive2026-04-14T09:29:54+02:00
Go to Top