About ITrust

This author has not yet filled in any details.
So far ITrust has created 141 blog entries.

Top 10 Criteria for Choosing a Vulnerability Scanner

Choosing the right vulnerability scanner is a critical step in strengthening the security of your information system. Faced with proliferating cyber threats and increasingly complex IT environments, not all tools are created equal. In this article, discover the 10 essential criteria for selecting a high-performance vulnerability scanner tailored to your technical environment and compliant with your security and privacy requirements. 1. Data Sovereignty Above all, it is essential to verify where the data collected by the scanner—such as logs, vulnerabilities, and configurations—is stored. Prioritize hosting located within [...]
Top 10 Criteria for Choosing a Vulnerability Scanner2025-10-28T09:18:31+01:00

Interoperability and sovereignty: Reveelium connects to 100% of the market via API

Are SIEM connectors the vital link in detection? In the cybersecurity arsenal, the SIEM holds a strategic position for collecting, normalizing, and analyzing events from multiple sources in real time. However, no matter how powerful a SIEM is, it cannot operate effectively without an essential component: connectors and their various key functions: Multi-source aggregation and event centralization: making sense of isolated events Advanced threat detection: connectors enable the correlation of weak signals scattered across the IS. Guarantee of an efficient run Reliable and contextualized reporting of logs to the platform [...]

Interoperability and sovereignty: Reveelium connects to 100% of the market via API2025-10-23T14:56:07+02:00

Case Study: An SME targeted by Kryptis avoids €500,000 in losses thanks to Reveelium

One of our clients was targeted by a Kryptis cyberattack.  €500,000 in losses: that is the estimated cost for this legal sector SME if the attack had succeeded (data loss, ransom demand, potential CNIL fine). The indirect impact is harder to quantify: loss of client trust (with their data exposed in the wild), tarnished brand reputation… In this article, discover how we were able to detect and block this cyberattack by leveraging the triptych of Reveelium XDR SIEM UEBA, Threat Intelligence, and human expertise. Focus on Kryptis: stealth malware [...]

Case Study: An SME targeted by Kryptis avoids €500,000 in losses thanks to Reveelium2025-10-23T15:15:36+02:00

Reveelium V12.3: A new release for intelligent, sovereign, and accessible monitoring

Reveelium V12.3 is the new release of our next-generation SIEM XDR! With this iteration, we reaffirm our ambition: to provide organizations with proactive, intelligent, and sovereign protection against increasingly sophisticated cyber threats. Already proven by numerous public and private clients, the new Reveelium V12.3 version reaffirms its position among the most powerful XDR platforms on the market. Designed for all businesses and organizations and developed by our France-based experts, this next-generation release incorporates more than 150 functional improvements. Key new features in Reveelium V12.3: Our teams have integrated into [...]

Reveelium V12.3: A new release for intelligent, sovereign, and accessible monitoring2025-10-23T15:24:09+02:00

French alternative to Splunk: 5 reasons to migrate in 2026

More than half (57%) of French SMBs have experienced at least one cyberattack over the past 12 months *. Faced with these escalating threats, organizations are increasingly turning to local, sovereign cybersecurity solutions. Why? To align with their ethical values and/or comply with increasingly strict regulatory requirements. ITrust positions itself as a strategic and effective alternative to major international solutions such as Splunk, highlighting its French identity and strong commitment to digital sovereignty. Why compare ITrust to Splunk [...]

French alternative to Splunk: 5 reasons to migrate in 20262026-09-17T10:53:14+02:00

CaRe Program: Domain 2 "Business Continuity and Disaster Recovery Strategy" is now open!

Business continuity and disaster recovery are vital challenges for healthcare institutions. It is within this context of urgency and digital transformation that Domain 2 of the CaRE program operates, officially launched on July 16, 2025. Its objective: to enable public and private healthcare organizations to prepare effectively for a digital outage scenario by providing them with structured operational and financial support. Why is Domain 2 so strategic? The healthcare sector remains one of the most targeted by cybercriminals, right behind local authorities and SMBs. In [...]

CaRe Program: Domain 2 "Business Continuity and Disaster Recovery Strategy" is now open!2026-04-14T09:43:14+02:00

Malware Focus: BlackSuit

 In 2023, BlackSuit established itself as one of the major ransomware threats: first, it steals your most sensitive data, then it locks down your systems, putting you under maximum pressure. Operating under the so-called "double extortion" model, this group first exfiltrates sensitive data before encrypting the victims' systems, thereby maximizing pressure to secure ransom payments. Renowned for its speed of execution and heavy reliance on offensive pentesting tools, BlackSuit primarily targets critical infrastructure and strikes where it hurts the most. Genesis and shared origin with Royal The [...]

Malware Focus: BlackSuit2025-10-23T16:09:00+02:00

Use Case: How Reveelium Meets the Needs of All Users Through Multi-Level Cyber Supervision

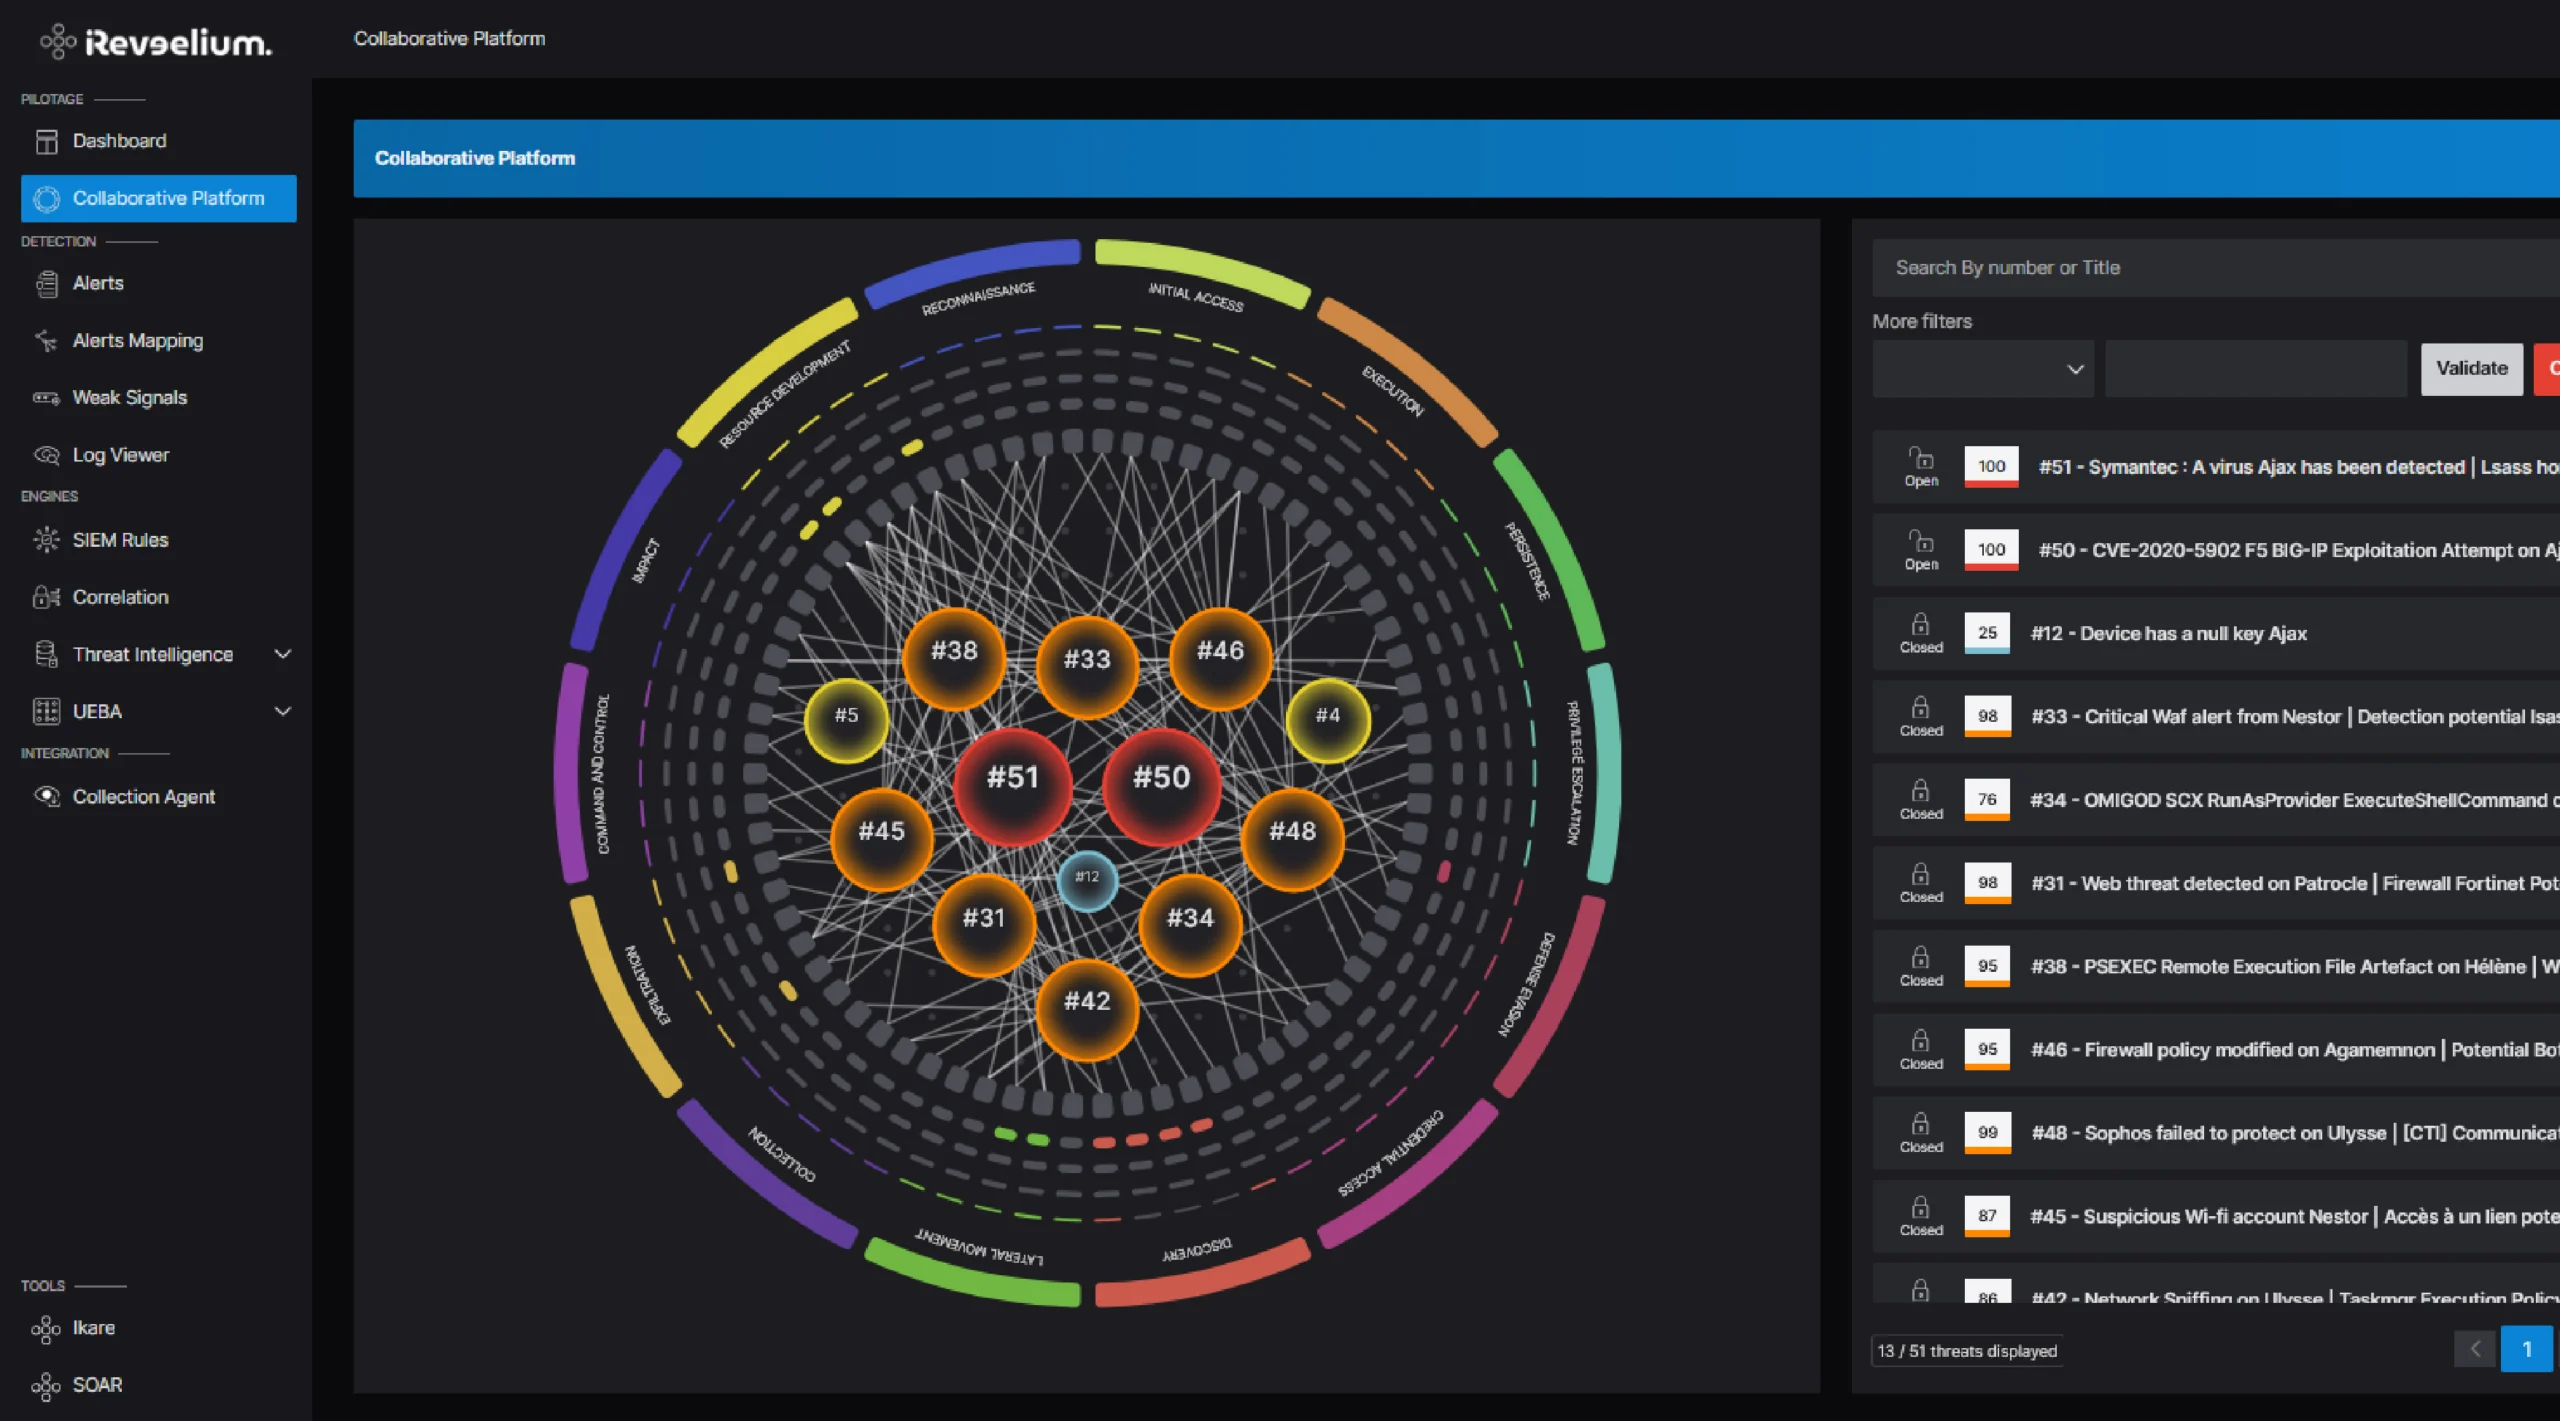
Reveelium is a SIEM XDR technology that detects known and unknown cyber threats and traces the footprints of cyberattacks. Its interface provides a secure collaborative workspace, granting real-time access to the same level of information across various stakeholders (Lead CIOs, SOC analysts, etc.). Multi-tier monitoring tailored to every profile Reveelium incorporates dashboards designed to adapt to different governance and operational tiers. Every user can access the strategic or technical indicators and views aligned with their specific scope of action. Strategic Monitoring: CIOs, CISOs, and executive committee members have access to [...]

Use Case: How Reveelium Meets the Needs of All Users Through Multi-Level Cyber Supervision2025-10-23T16:10:47+02:00

Malware Focus: SparkCat

SparkCat is a mobile malware identified in 2024, capable of automatically extracting sensitive data from screenshots stored on Android and iOS devices. Utilizing optical character recognition (OCR) mechanisms, it represents a stealthy, targeted threat capable of bypassing traditional protections by legitimately exploiting permissions granted to applications. Application infection vectors and abuse of mobile permissions The infection chain relies on distributing seemingly harmless applications via official stores or through sideloading. These applications request access to multimedia files (photo library, screenshots) under functional pretexts such as [...]

Malware Focus: SparkCat2025-10-23T16:10:53+02:00

ITrust launches "Channel First": a partner program centered on Reveelium v12.3

ITrust, a leading cybersecurity provider, unveils "Channel First", its new Partner Program for MSSPs, Resellers, and Distributors. Centered around Reveelium v12.3, the sovereign SIEM XDR developed in France, this program stands out as a genuine alternative to dominant American solutions. Designed as a high-value "private club", Channel First is tailored for channel players looking to deliver a sovereign, high-performing, and cost-effective solution to their clients. A market seeking simplicity and sovereignty As the European SIEM/XDR market undergoes significant transformation, organizations are actively seeking solutions [...]

ITrust launches "Channel First": a partner program centered on Reveelium v12.32026-04-14T09:58:53+02:00
Go to Top