About ITrust

This author has not yet filled in any details.
So far ITrust has created 141 blog entries.

Freebox Pro: How Artificial Intelligence enables automated anomaly detection

ITrust's SOC (Security Operations Center) teams rely on our Reveelium tool, which combines powerful internally developed algorithms and artificial intelligence to analyze massive volumes of data in real time and identify current or emerging threats. These algorithms enable incident detection as well as automated responses to accelerate reaction times. AI and Cybersecurity Amid the widespread adoption of Artificial Intelligence, malicious actors are increasingly leveraging AI in their attacks. AI facilitates the execution of complex tasks, considerably enhancing the sophistication and [...]
Freebox Pro: How Artificial Intelligence enables automated anomaly detection2025-10-23T16:15:39+02:00

New Freebox Pro: how ITrust leverages Threat Intelligence resources to ensure your protection

Launched on January 14, the new Freebox Pro includes numerous innovations to optimally protect your business. Among others, a Threat Intelligence database containing more than four million malicious traffic signatures, sourced from over fifty feeds, enables real-time detection of threats and anomalies. What is Threat Intelligence? Threat Intelligence is the process of collecting, processing, and analyzing data to understand the motives, behaviors, and targets of threat actors. The objective is to provide actionable intelligence to prevent and counter [...]

New Freebox Pro: how ITrust leverages Threat Intelligence resources to ensure your protection2026-04-14T09:28:13+02:00

ITrust x Free Pro: New Freebox Pro cybersecurity!

The New Freebox Pro: A Concentration of Technology and Security for Businesses Performance, security, and innovation: the new Freebox Pro pushes the boundaries to support businesses in their digital challenges. Designed by Free Pro, it incorporates best-in-class technologies to deliver ultra-fast connectivity and cutting-edge cybersecurity. With Essential Cybersecurity, developed in partnership with ITrust, this box goes far beyond internet access by providing real-time protection against cyber threats. A major leap forward for VSEs and SMEs, which now have access to a high-performance cybersecurity solution typically reserved for [...]

ITrust x Free Pro: New Freebox Pro cybersecurity!2025-10-24T12:08:34+02:00

Focus on Perfctl: The Malware Targeting Linux Systems

Perfctl is a relatively recent malware that has rapidly demonstrated its ability to infiltrate complex environments, particularly corporate Linux servers. Over the past three to four years, Perfctl has reportedly targeted millions of Linux servers, exploiting nearly 20,000 vulnerable configurations, such as exposed credentials or poorly secured management interfaces. Far more than a simple malicious script, Perfctl stands out due to its modular architecture and advanced evasion techniques, making its detection and neutralization particularly challenging. Chronological Overview and Victimology of Perfctl Perfctl was first detected [...]

Focus on Perfctl: The Malware Targeting Linux Systems2026-04-14T10:12:29+02:00

Reveelium Features: The Weak Signals database

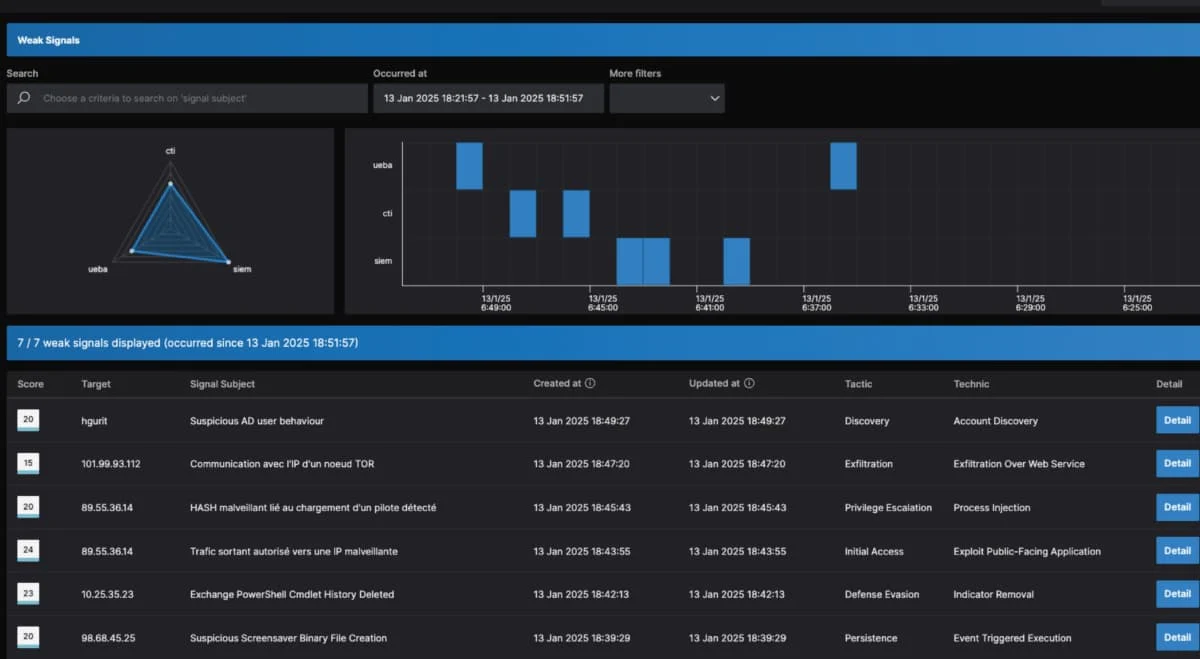
Weak Signals: A Major Breakthrough in Reveelium V12 One of the key priorities for version 12 of Reveelium was to redefine the threat qualification structure. Today, the process relies on a structured, optimized lifecycle: from logs, weak signals are identified and subsequently requalified into alerts. These alerts are then analyzed by SOC experts to create incident tickets—termed "threats"—enabling targeted, rapid interventions for clients. Weak signal detection also gains significant performance with v12 thanks to a Weak Signals database integrated into [...]

Reveelium Features: The Weak Signals database2026-04-14T08:55:40+02:00

How Reveelium, the French SIEM XDR, leverages the MITRE ATT&CK® framework to strengthen its detection capabilities

Adopted by thousands of organizations worldwide, the MITRE ATT&CK knowledge base is regularly updated to reflect the latest evolutions in cyber threats, driven by thousands of contributions from the cybersecurity community and shared threat intelligence. Its integration into the Reveelium platform enhances its detection and investigation capabilities, enabling teams to efficiently identify, analyze, and respond to the tactics and techniques employed by cyberattackers. MITRE ATT&CK: An Essential Technical Framework for Cybersecurity Experts The MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) framework is an open-source model documenting the tactics, [...]

How Reveelium, the French SIEM XDR, leverages the MITRE ATT&CK® framework to strengthen its detection capabilities2026-04-14T09:08:01+02:00

MitM Attack Focus: Evil Twin

The Evil Twin attack is a form of Man-in-the-Middle (MitM) attack targeting public Wi-Fi networks. Its name comes from the fact that an attacker sets up a rogue Wi-Fi access point mimicking a legitimate network to deceive users. Once connected, sensitive data such as credentials, passwords, or banking information are intercepted. According to studies, more than 15% of attacks on public Wi-Fi networks involve this method, and nearly 70% of users connect without verifying the network's authenticity. Particularly widespread in cafes, hotels, airports, and [...]

MitM Attack Focus: Evil Twin2026-04-14T10:11:29+02:00

Malware Spotlight: Agent Tesla

Agent Tesla stands out as an advanced Remote Access Trojan (RAT), frequently deployed for malicious purposes. Operating as both a keylogger and an information stealer, this malware can monitor user activities, exfiltrate sensitive data, and severely compromise victim security. With an estimated global impact of 3%, understanding its operation, features, and use cases is essential to mount an effective defense. How the Malware Works: A Well-Oiled Machine. Agent Tesla follows a methodical process to infect, establish persistence, collect, and exfiltrate data. Here is a detailed breakdown of [...]

Malware Spotlight: Agent Tesla2026-04-13T16:16:09+02:00

Malware Spotlight: Steelfox

In current cyber news, one name is sparking both curiosity and concern: Steelfox. This malware, with an enigmatic name evoking the strength of steel and the cunning of a fox, perfectly reflects its nature: stealthy, resilient, and remarkably effective. But where does this malicious software originate? Its origins raise as many questions as theories. To fully grasp this threat and anticipate its next moves, our cybersecurity experts break it down. Chronological Overview of the Malware. First spotted in 2023, SteelFox has shown rapid propagation and continuous development: February 2023: Initial identification. [...]

Malware Spotlight: Steelfox2026-04-14T10:14:41+02:00

Malware Spotlight: The Zergeca Botnet

Zergeca is a type of malware discovered in 2024. It is a network of compromised machines (botnet) engineered to execute Distributed Denial of Service (DDoS) attacks, while also featuring capabilities far broader than conventional botnets. Developed in Golang—an open-source language created by Google—Zergeca shares traits reminiscent of the Mirai botnet, notably the reuse of command and control (C2) infrastructure, suggesting a common author or potential connections between threat actors. Its name, derived from "ootheca" (an insect egg capsule) discovered within its servers [...]

Malware Spotlight: The Zergeca Botnet2026-04-13T16:06:22+02:00
Go to Top