The MITRE ATT&CK knowledge base, adopted by thousands of organizations worldwide, is regularly updated to reflect the latest evolutions in cyber threats thanks to thousands of contributions from the cybersecurity community and shared intelligence. Its integration into the Reveelium platform enriches its detection and investigation capabilities to efficiently identify, analyze, and respond to cyber attackers' tactics and techniques.
MITRE ATT&CK: An essential technical framework for cybersecurity experts
The MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) framework is an open-source framework documenting the tactics, techniques, and procedures (TTPs) used by threat actors in real-world intrusion scenarios. Structured in matrices, it covers multiple environments: Enterprise, Mobile, and ICS (Industrial Control Systems). The Enterprise matrix, for example, includes 14 tactics and 193 techniques, while the Mobile version comprises 16 tactics and 123 techniques. MITRE ATT&CK relies on the analysis of real-world adversary behavior, enabling cyber kill chain modeling and the enhancement of defense strategies. Regular updates, such as version 16 which introduced 18 new sub-techniques, demonstrate its ability to evolve alongside emerging attack methods. A reference tool for SOC analysts, threat hunters, and offensive security experts, MITRE ATT&CK facilitates detection, adversary emulation, and precise vulnerability identification.
The MITRE ATT&CK framework at the core of the Reveelium platform
Reveelium strategically integrates the MITRE ATT&CK framework, enriching it with multiple advanced capabilities. This integration enables Reveelium to enhance its detection, correlation, and incident response capabilities.
360° threat visualization
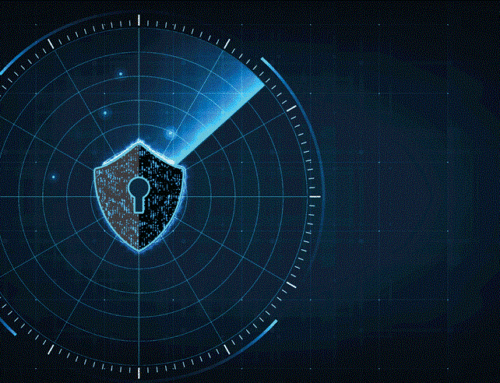
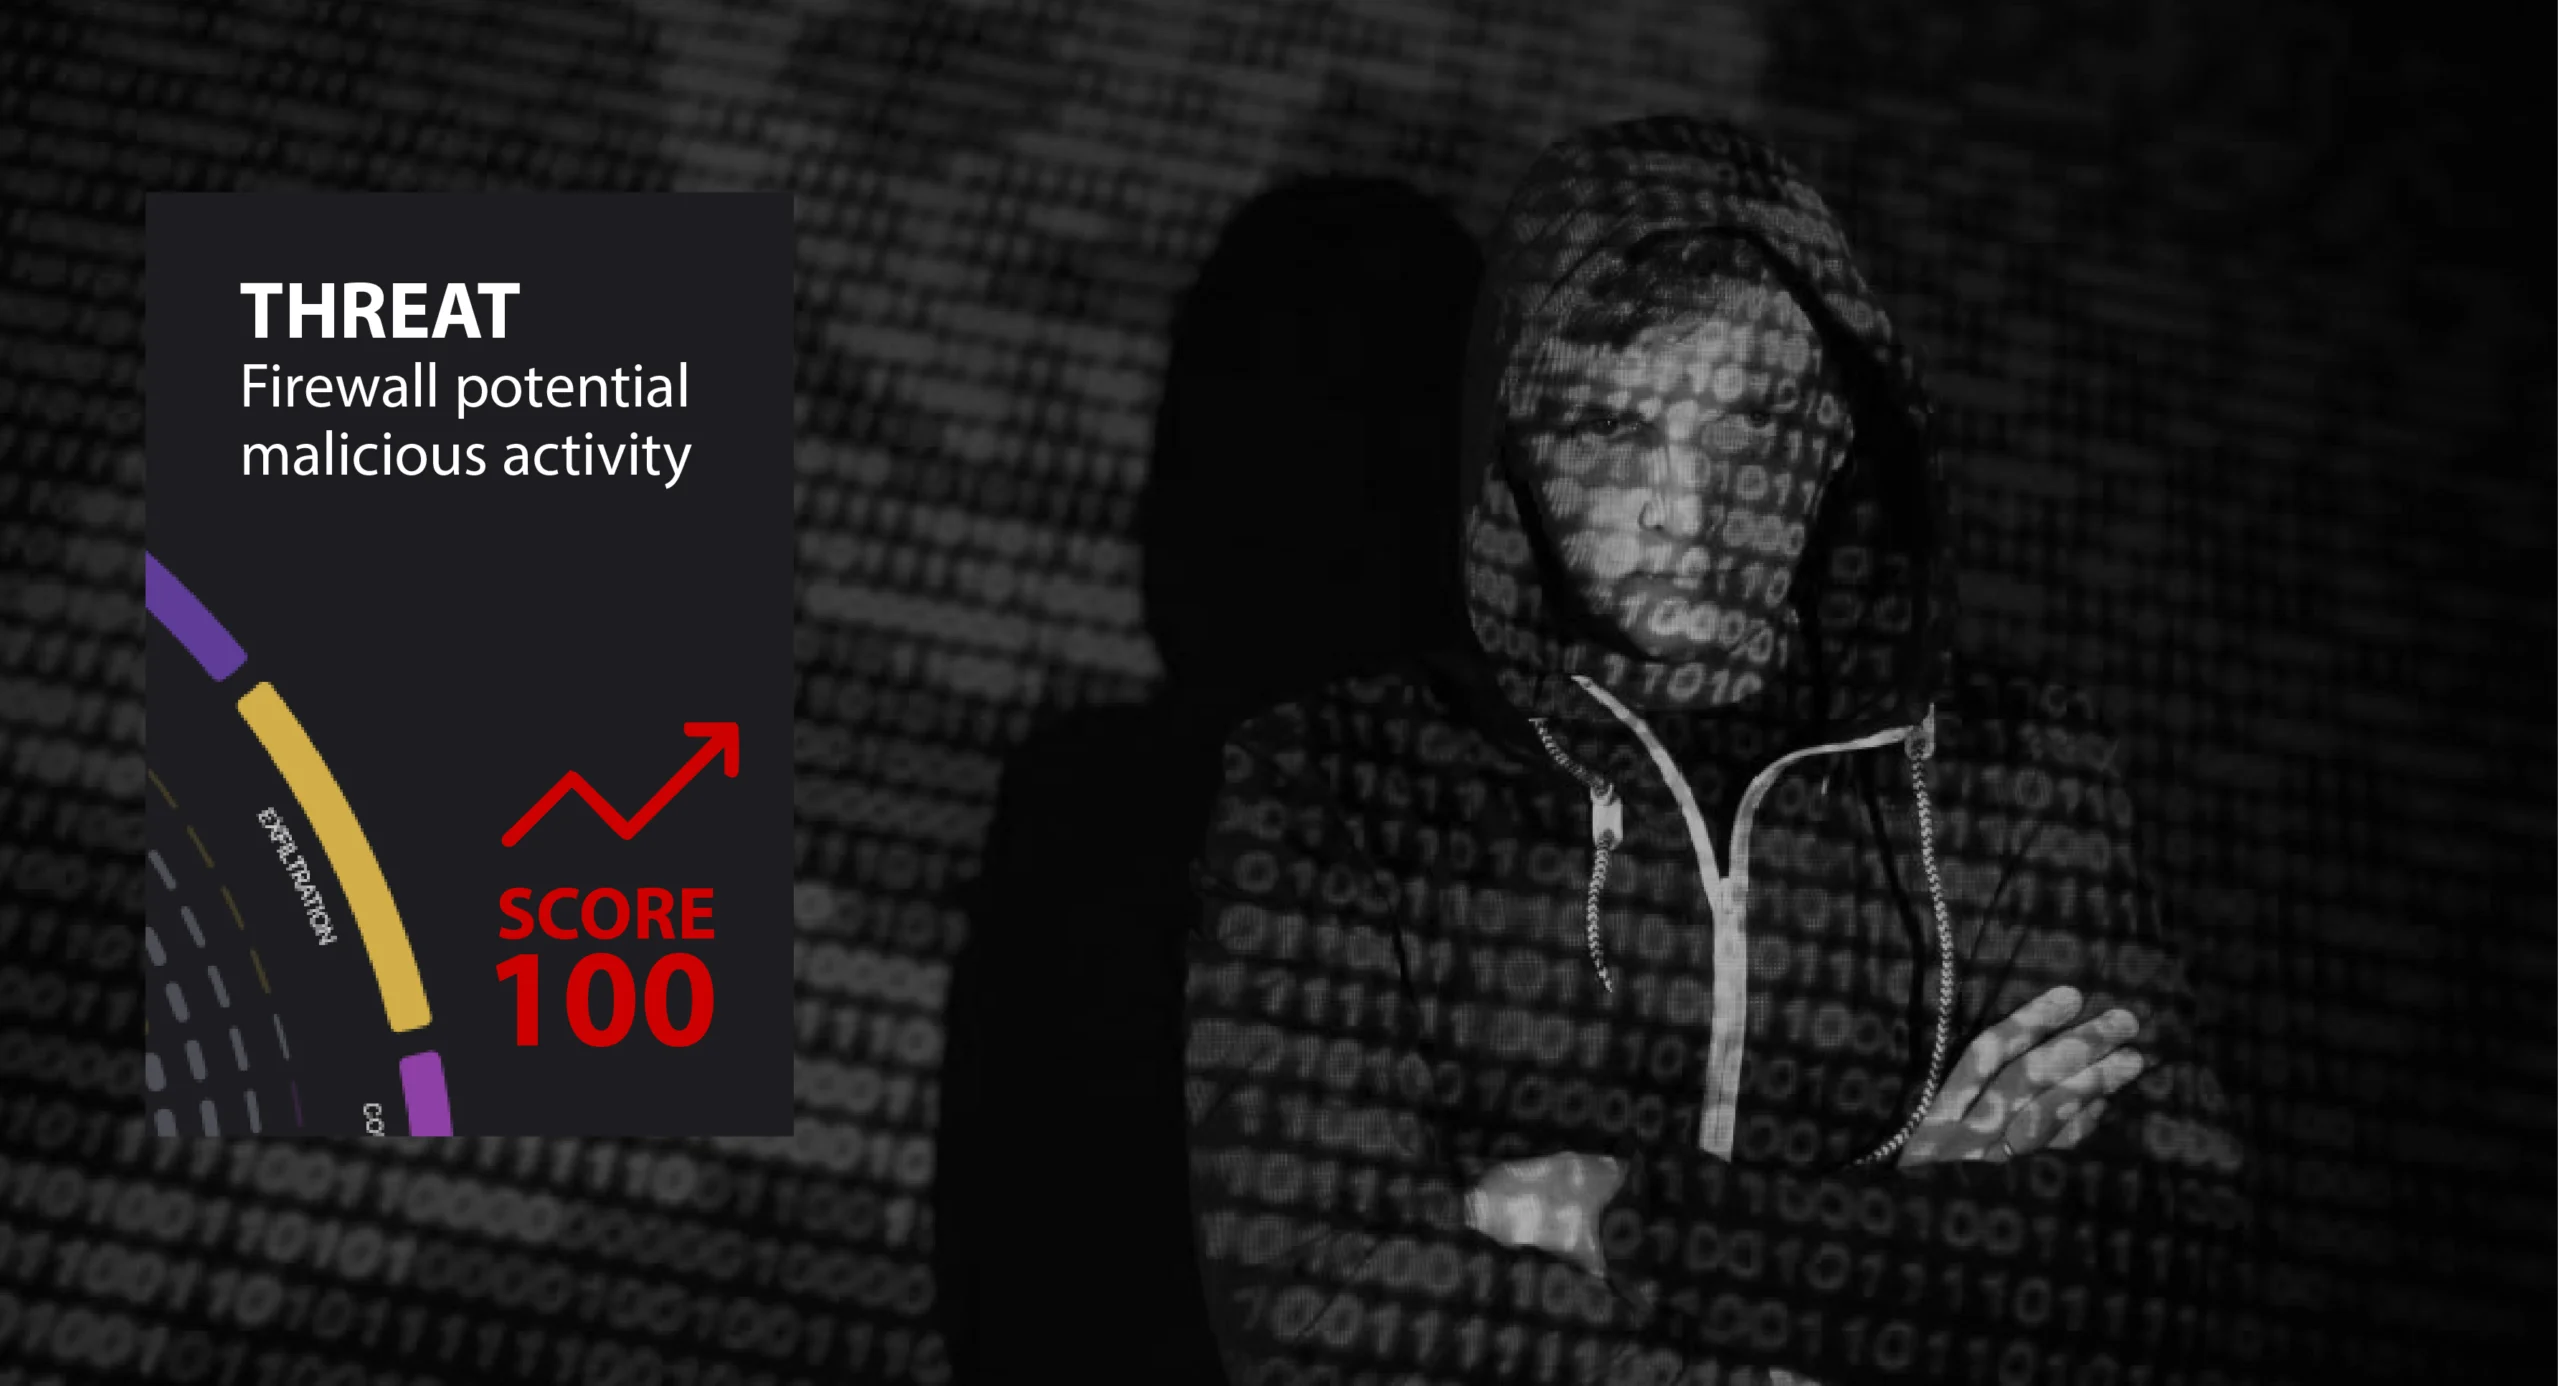
Threat mapping in the form of a target/radar view is a major feature of the Reveelium platform. This visualization leverages the MITRE ATT&CK framework to provide a clear, structured representation of detected attacks. It plots tactics along its perimeter, offering a clear and detailed view of the attack vectors exploited by threat actors. This intuitive visualization streamlines threat analysis by cross-referencing events from various log sources, incorporating a timeline perspective, and accurately assessing their criticality level.
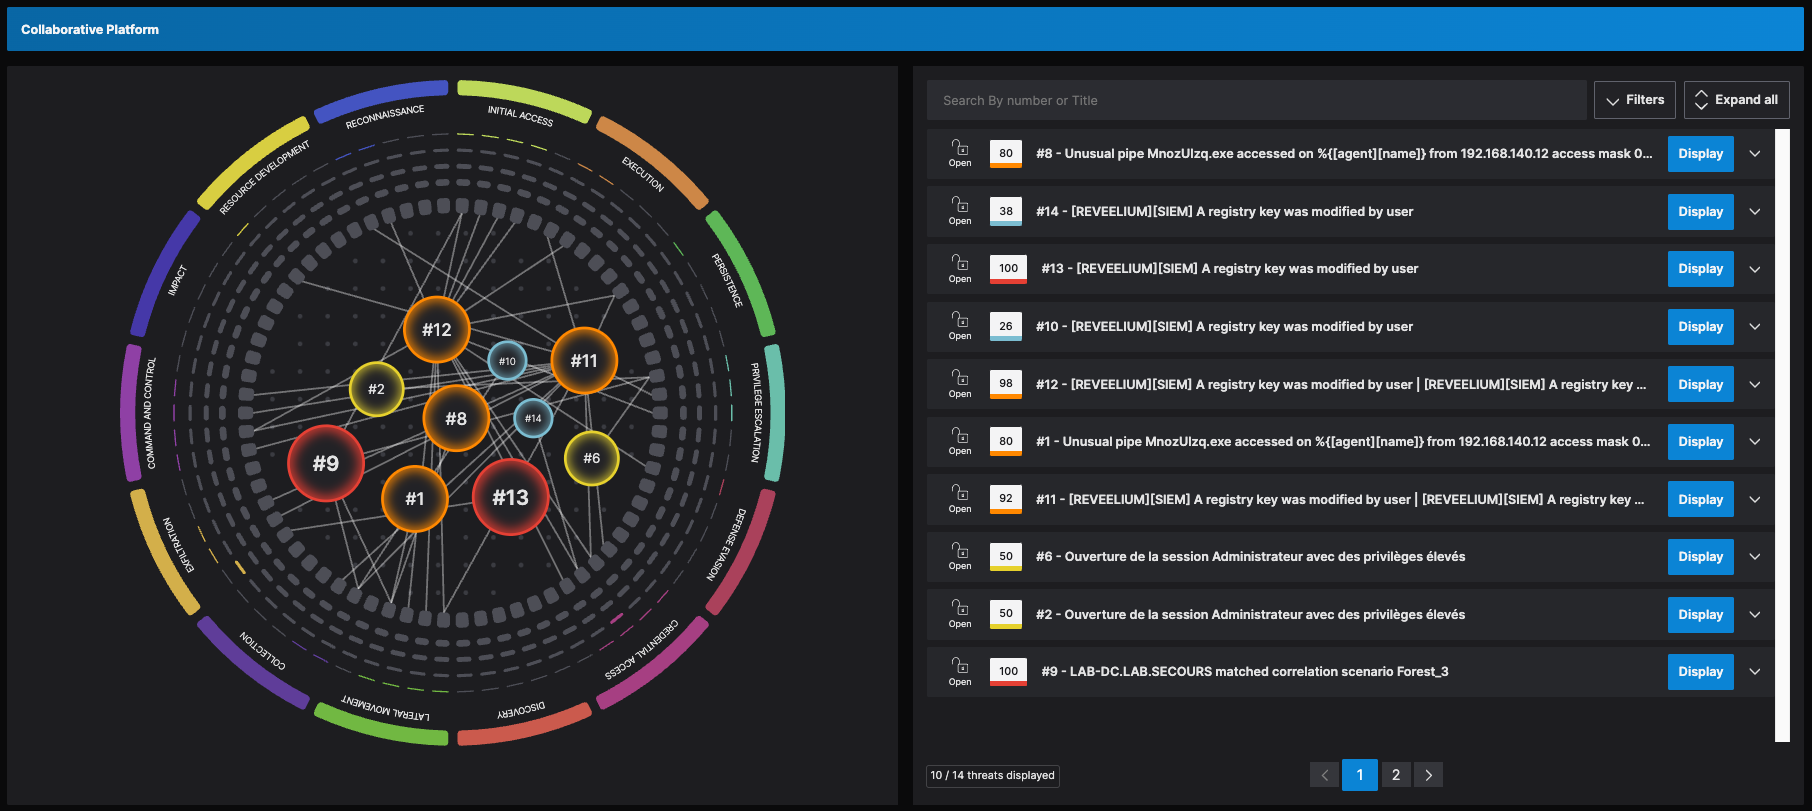
Collaborative Platform Reveelium x MITRE ATT&CK (demo)
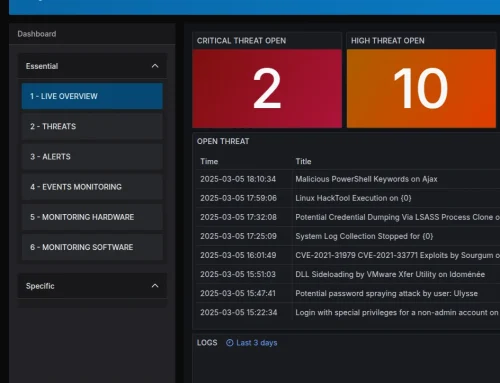
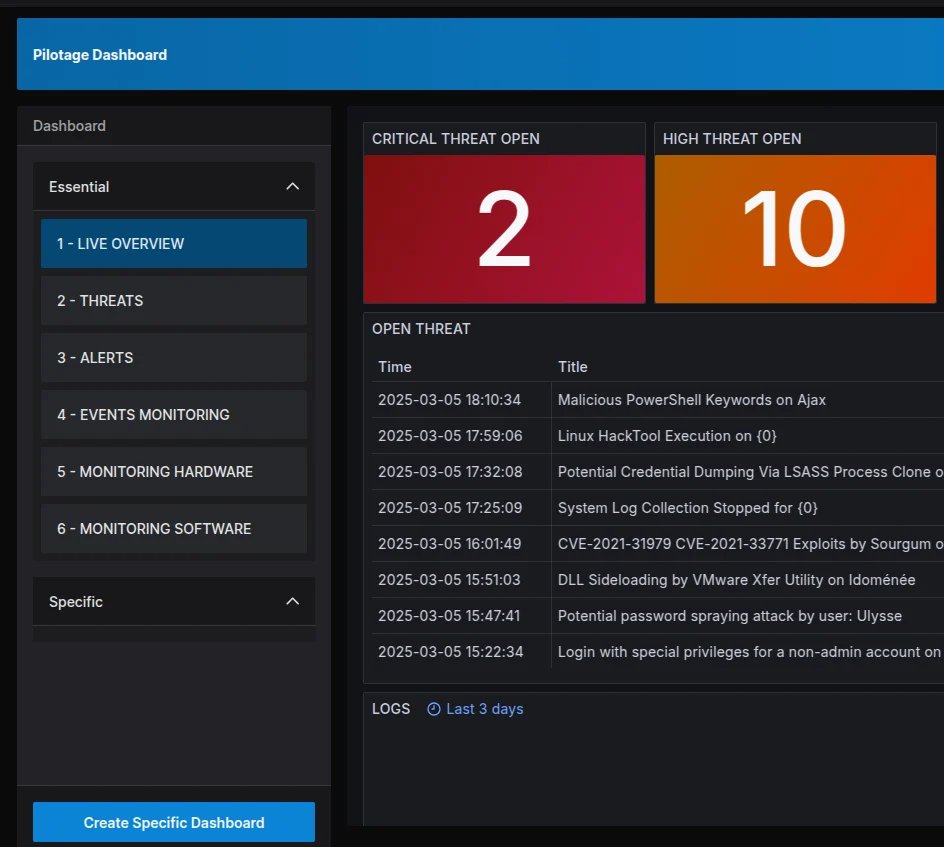
In addition to the target view, Reveelium provides detailed information on each detected threat. This data includes tactics and techniques derived from the MITRE ATT&CK framework. With a single click, users can access their position within the intrusion chain as well as associated references, enabling a clear understanding of the attack's progression.
An IOC database contextualized by the MITRE ATT&CK matrix
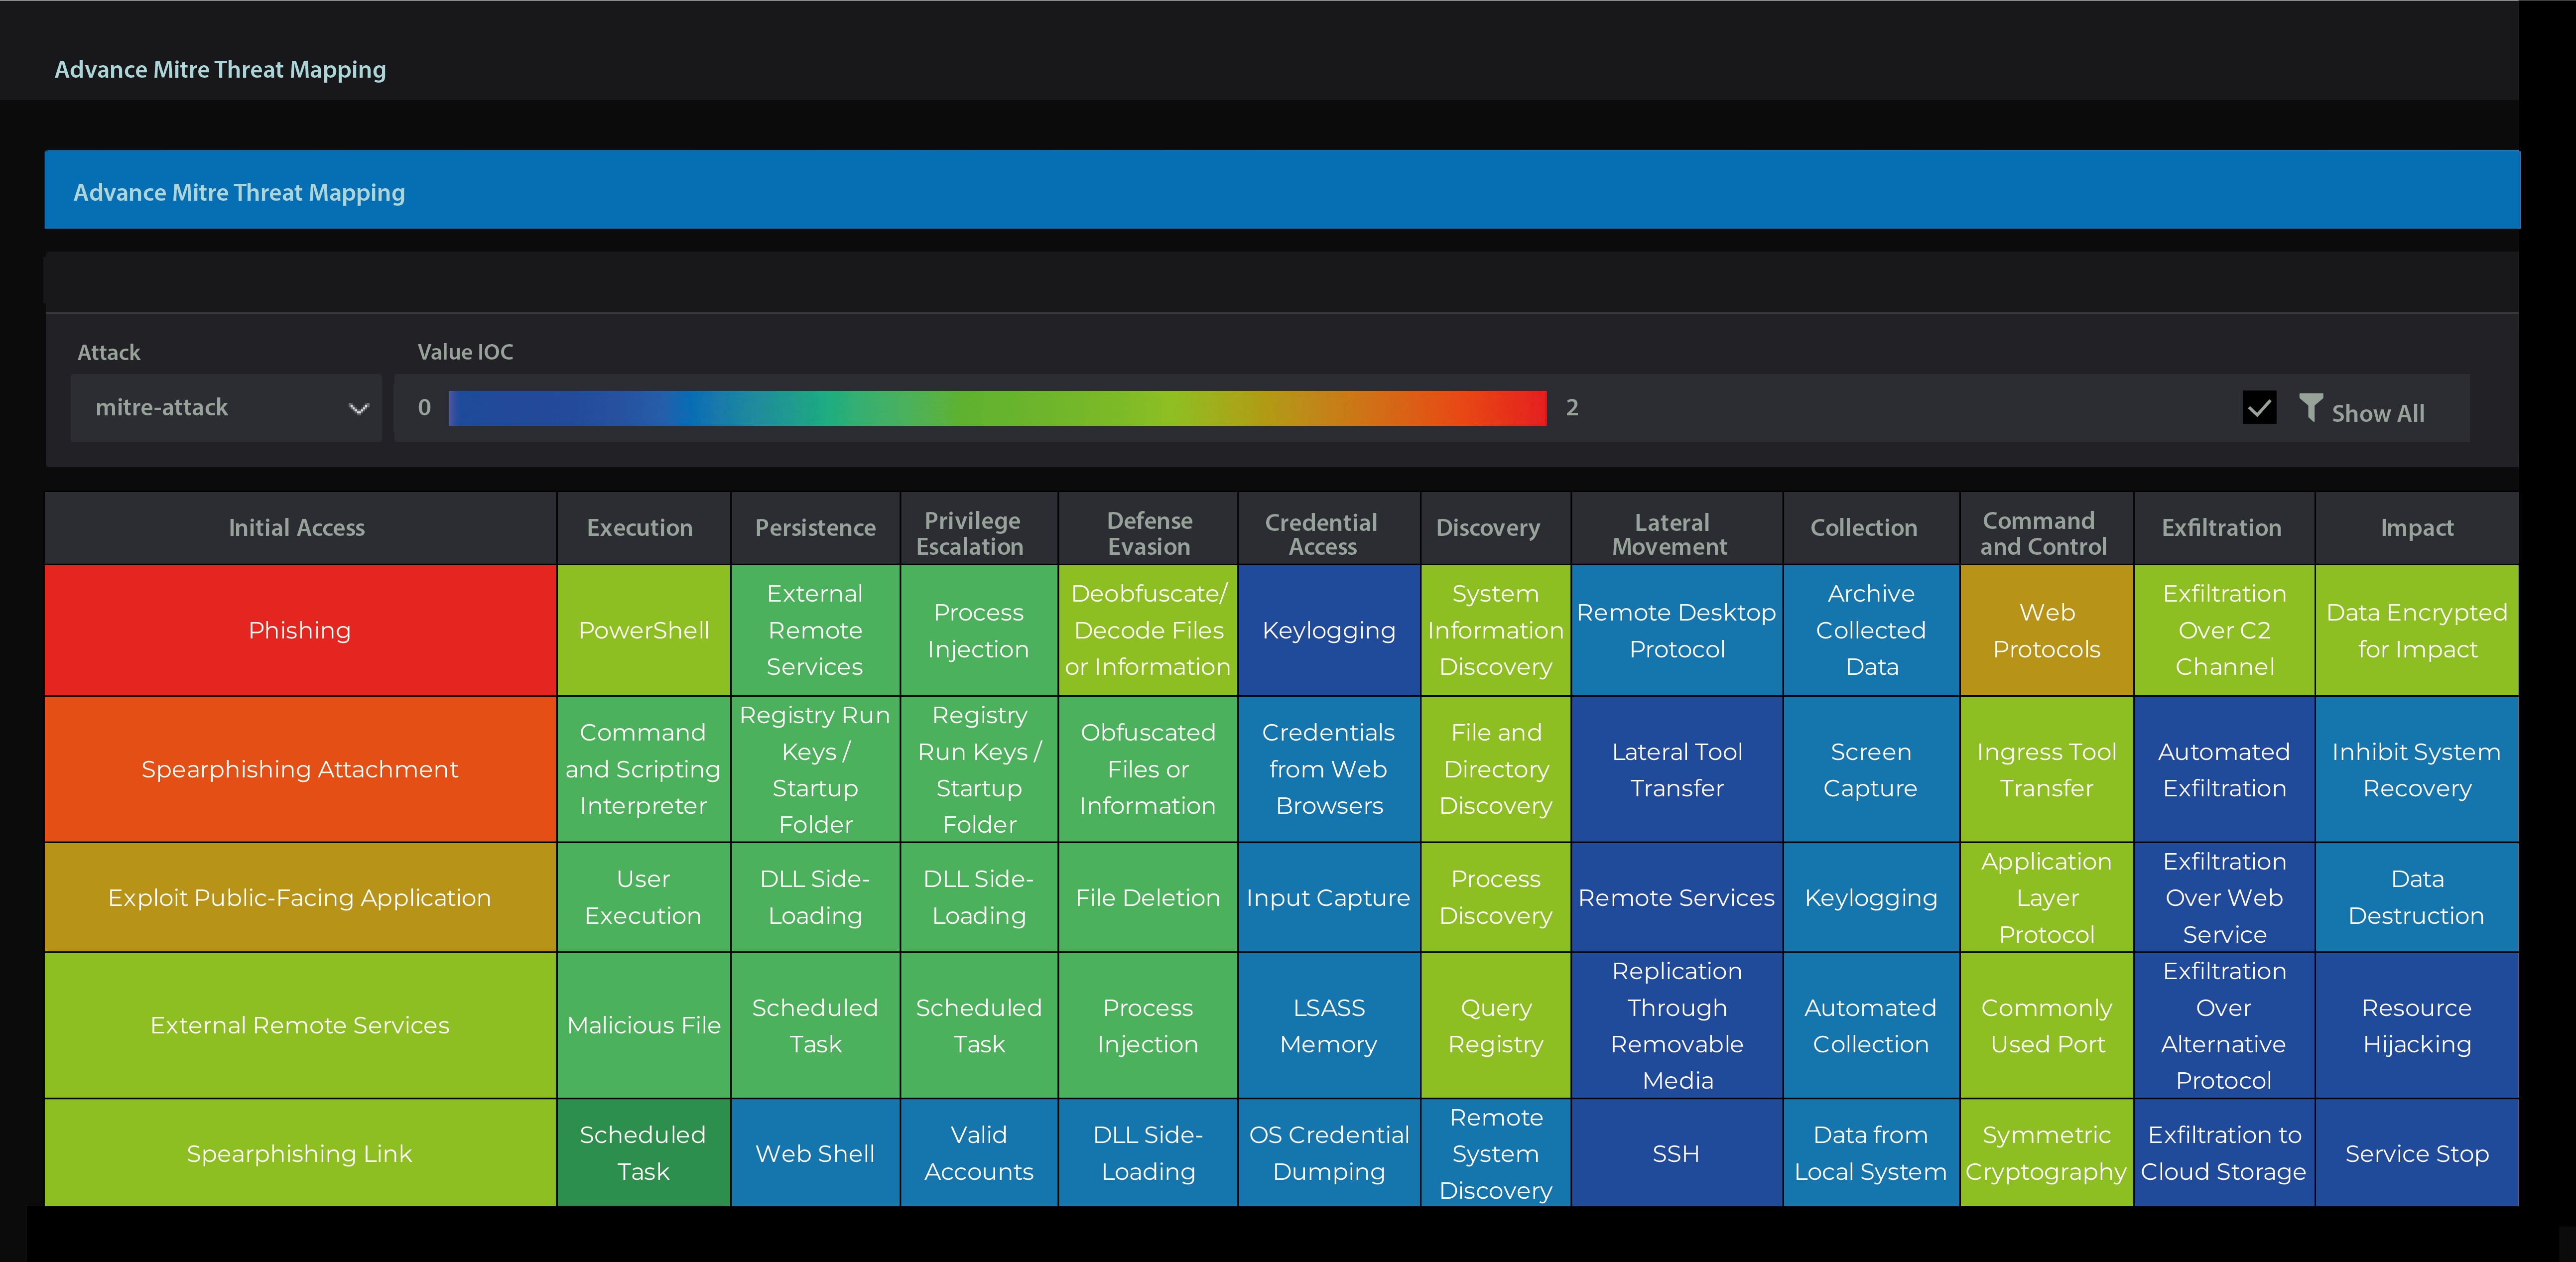
Advanced event correlation with the MITRE ATT&CK filter
The synergy between Reveelium and MITRE ATT&CK
While the MITRE ATT&CK knowledge base is a benchmark for categorizing and analyzing known adversary techniques, it has limitations due to its reliance on pre-documented threats. This model, based on previously observed techniques, cannot detect or anticipate emerging (unknown) threats, such as zero-day attacks (novel, undocumented). Furthermore, the static nature of MITRE ATT&CK does not allow for real-time identification of anomalies specific to a given environment. The full added value of Reveelium lies in this complementarity, integrating advanced behavioral analysis and artificial intelligence to deliver a dynamic, proactive approach.