Threat Actor Spotlight: ZeroBytes

Active in France since at least July 2026, ZeroBytes is a cybercrime group specializing in data theft and resale. Operating across social media platforms, it targets both public and private organizations without any specific sector bias. Its modus operandi relies primarily on exploiting compromised credentials and legitimate access, enabling the exfiltration of sensitive data without necessarily exploiting critical vulnerabilities or deploying malware. This approach underscores the critical role of digital identity in attack chains. Compromised credentials as the primary access vector The operational model detailed by ZeroBytes relies mainly on leveraging previously [...]
Threat Actor Spotlight: ZeroBytes2026-10-15T08:39:37+02:00

Reverse Engineering of a Recent PureLogs Stealer Campaign

Among the daily attacks monitored by SOC analysts during their surveillance operations, stealer-type malware occupies a prominent position. These malicious programs, designed to harvest passwords stored insecurely on endpoints, are heavily utilized by threat actors in credential-harvesting campaigns. The attacks are straightforward, rapid, and easily scalable. Infostealers include well-known variants such as Lumma Stealer, Vidar, RedLine, and others. Around mid-July 2026, an EDR instance deployed at a client site blocked network traffic resulting from the execution of [...]

Reverse Engineering of a Recent PureLogs Stealer Campaign2026-09-02T10:41:15+02:00

Threat Actor Spotlight: The Gentlemen

Emerging in 2025, The Gentlemen is a ransomware group linked to an internal split within the Qilin ecosystem. Operating on a RaaS (Ransomware-as-a-Service) model, this threat actor deploys a double-extortion strategy: data exfiltration followed by encryption of compromised systems. The group does not appear to follow a specific industry focus. Identified victims range from SMBs to larger enterprises, with operations spanning multiple geographic regions. This opportunistic approach primarily exploits internet-facing equipment and insufficiently secured environments. Massive exploitation of exposed access vectors The operations attributed to The [...]

Threat Actor Spotlight: The Gentlemen2026-05-25T16:06:34+02:00

DarkSword: iOS Zero-Day Exploit Exposes Millions of Apple Devices to Hacking

In brief, as of March 2026, the barrier between nation-state exploitation capabilities and organized cybercrime has collapsed. The simultaneous disclosure of two complete iOS exploit kits, Corona and DarkSword, within a single month indicates a saturation of the mobile vulnerability market. DarkSword, a full-chain exploit written in JavaScript, allows full compromise of iOS devices (versions 18.4 to 18.7) with minimal user interaction. Leveraged by suspected nation-state actors (UNC6353) and commercial surveillance vendors (PARS Defense, UNC6748), this kit exemplifies a critical trend: the [...]

DarkSword: iOS Zero-Day Exploit Exposes Millions of Apple Devices to Hacking2026-04-14T10:05:20+02:00

Malware Focus: BlackSuit

 In 2023, BlackSuit established itself as one of the major ransomware threats: first, it steals your most sensitive data, then it locks down your systems, putting you under maximum pressure. Operating under the so-called "double extortion" model, this group first exfiltrates sensitive data before encrypting the victims' systems, thereby maximizing pressure to secure ransom payments. Renowned for its speed of execution and heavy reliance on offensive pentesting tools, BlackSuit primarily targets critical infrastructure and strikes where it hurts the most. Genesis and shared origin with Royal The [...]

Malware Focus: BlackSuit2025-10-23T16:09:00+02:00

Malware Focus: SparkCat

SparkCat is a mobile malware identified in 2024, capable of automatically extracting sensitive data from screenshots stored on Android and iOS devices. Utilizing optical character recognition (OCR) mechanisms, it represents a stealthy, targeted threat capable of bypassing traditional protections by legitimately exploiting permissions granted to applications. Application infection vectors and abuse of mobile permissions The infection chain relies on distributing seemingly harmless applications via official stores or through sideloading. These applications request access to multimedia files (photo library, screenshots) under functional pretexts such as [...]

Malware Focus: SparkCat2025-10-23T16:10:53+02:00

RaaS Group Focus: Play

Since its emergence in 2022, the Play group has established itself as a major player in the ransomware landscape. Operating under a Ransomware-as-a-Service (RaaS) model, Play targets organizations across diverse sectors, primarily in North America, Europe (notably Germany and France), and Latin America. The group is recognized for its advanced intrusion techniques, its reliance on living-off-the-land binaries (LOLBins), and its double-extortion strategy. Tactics, Techniques, and Procedures (TTPs) of Play 1. Initial access and privilege escalation Play exploits known vulnerabilities to breach target systems, notably: Fortinet SSL [...]

RaaS Group Focus: Play2025-10-23T16:11:28+02:00

Ransomware Group Focus: Inc Ransom

Inc Ransom does not stop at encryption: it orchestrates its attacks as a service, leveraging structured methodologies, professional tooling, and an exfiltration strategy designed to bypass traditional defenses. In just a year and a half, this emerging threat actor has already struck more than 220 organizations. In this article, we provide an in-depth analysis of their operating procedures, initial access, persistence, and impact tactics, as well as the technical mechanisms deployed to evade detection and coerce victims. A well-oiled model, from phishing to encryption The Inc Ransom group operates according to a classic yet ruthlessly effective cyberattack schema, combining [...]

Ransomware Group Focus: Inc Ransom2025-10-23T16:12:03+02:00

Focus on Perfctl: The Malware Targeting Linux Systems

Perfctl is a relatively recent malware that has rapidly demonstrated its ability to infiltrate complex environments, particularly corporate Linux servers. Over the past three to four years, Perfctl has reportedly targeted millions of Linux servers, exploiting nearly 20,000 vulnerable configurations, such as exposed credentials or poorly secured management interfaces. Far more than a simple malicious script, Perfctl stands out due to its modular architecture and advanced evasion techniques, making its detection and neutralization particularly challenging. Chronological Overview and Victimology of Perfctl Perfctl was first detected [...]

Focus on Perfctl: The Malware Targeting Linux Systems2026-04-14T10:12:29+02:00

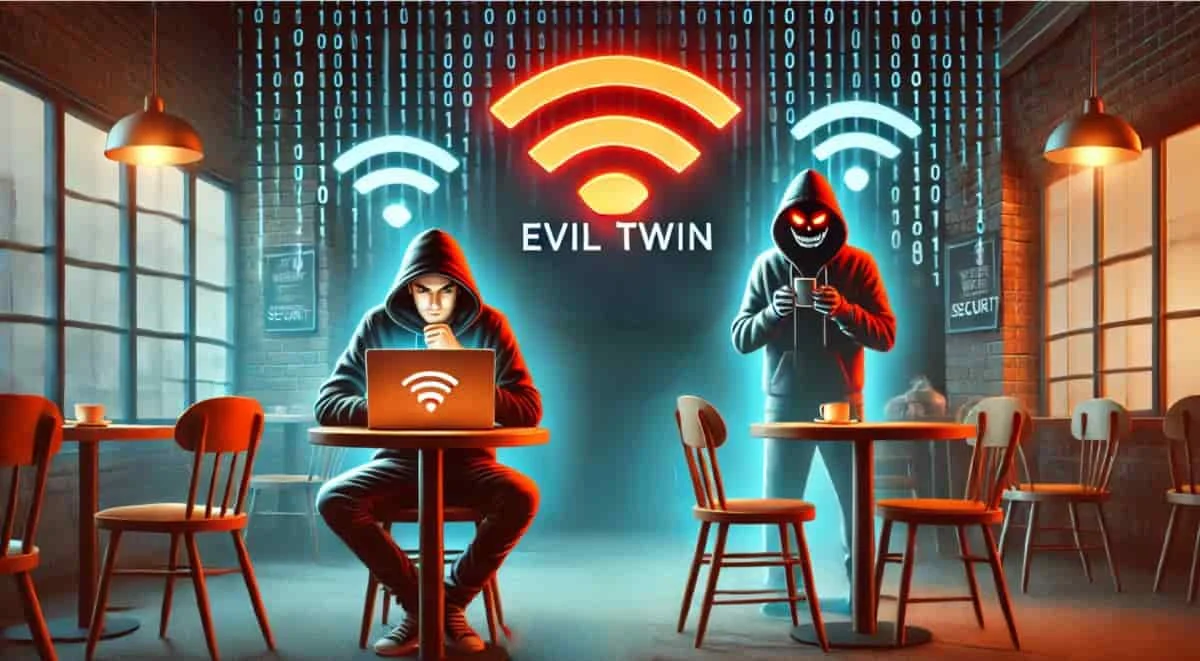
MitM Attack Focus: Evil Twin

The Evil Twin attack is a form of Man-in-the-Middle (MitM) attack targeting public Wi-Fi networks. Its name comes from the fact that an attacker sets up a rogue Wi-Fi access point mimicking a legitimate network to deceive users. Once connected, sensitive data such as credentials, passwords, or banking information are intercepted. According to studies, more than 15% of attacks on public Wi-Fi networks involve this method, and nearly 70% of users connect without verifying the network's authenticity. Particularly widespread in cafes, hotels, airports, and [...]

MitM Attack Focus: Evil Twin2026-04-14T10:11:29+02:00
Go to Top