About ITrust

This author has not yet filled in any details.
So far ITrust has created 143 blog entries.

ISO 9001 chez ITrust : décryptage d’une démarche qualité au service des clients

Chez ITrust, la certification ISO 9001 ne se résume pas à une reconnaissance officielle. Elle traduit une démarche collective visant à maîtriser les processus, améliorer les prestations et renforcer la satisfaction client. À travers ses pratiques, ses engagements et les résultats de son dernier audit, ITrust revient sur la place de la qualité dans ses activités de cybersécurité. ISO 9001 : une norme internationale axée sur la qualité Reconnue à l'échelle internationale, la norme ISO 9001 définit les exigences d'un système de management de la qualité. Elle vise à aider les organisations à structurer et maîtriser leurs processus, à [...]
ISO 9001 chez ITrust : décryptage d’une démarche qualité au service des clients2026-10-30T15:42:22+01:00

TrendAI Vision One™ × Reveelium.ai Defend : deux plateformes, une vision unifiée de la menace

Sur un endpoint, une activité suspecte peut être détectée avec un niveau de détail particulièrement fin. Mais pour un analyste SOC, cette détection n’est souvent qu’une pièce du puzzle : authentifications, flux réseau, événements cloud, logs applicatifs ou alertes issues d’autres solutions de sécurité peuvent être nécessaires pour comprendre l’incident dans son ensemble. C’est tout l’intérêt de la complémentarité entre TrendAI Vision One™ Endpoint Security et Reveelium.ai Defend : exploiter la richesse des informations issues de la protection endpoint et les corréler avec les autres signaux disponibles dans le système d’information. De l’endpoint au contexte global de l’incident TrendAI [...]

TrendAI Vision One™ × Reveelium.ai Defend : deux plateformes, une vision unifiée de la menace2026-10-26T09:21:40+01:00

How Reveelium turns analyzed threats into actionable knowledge for future ones

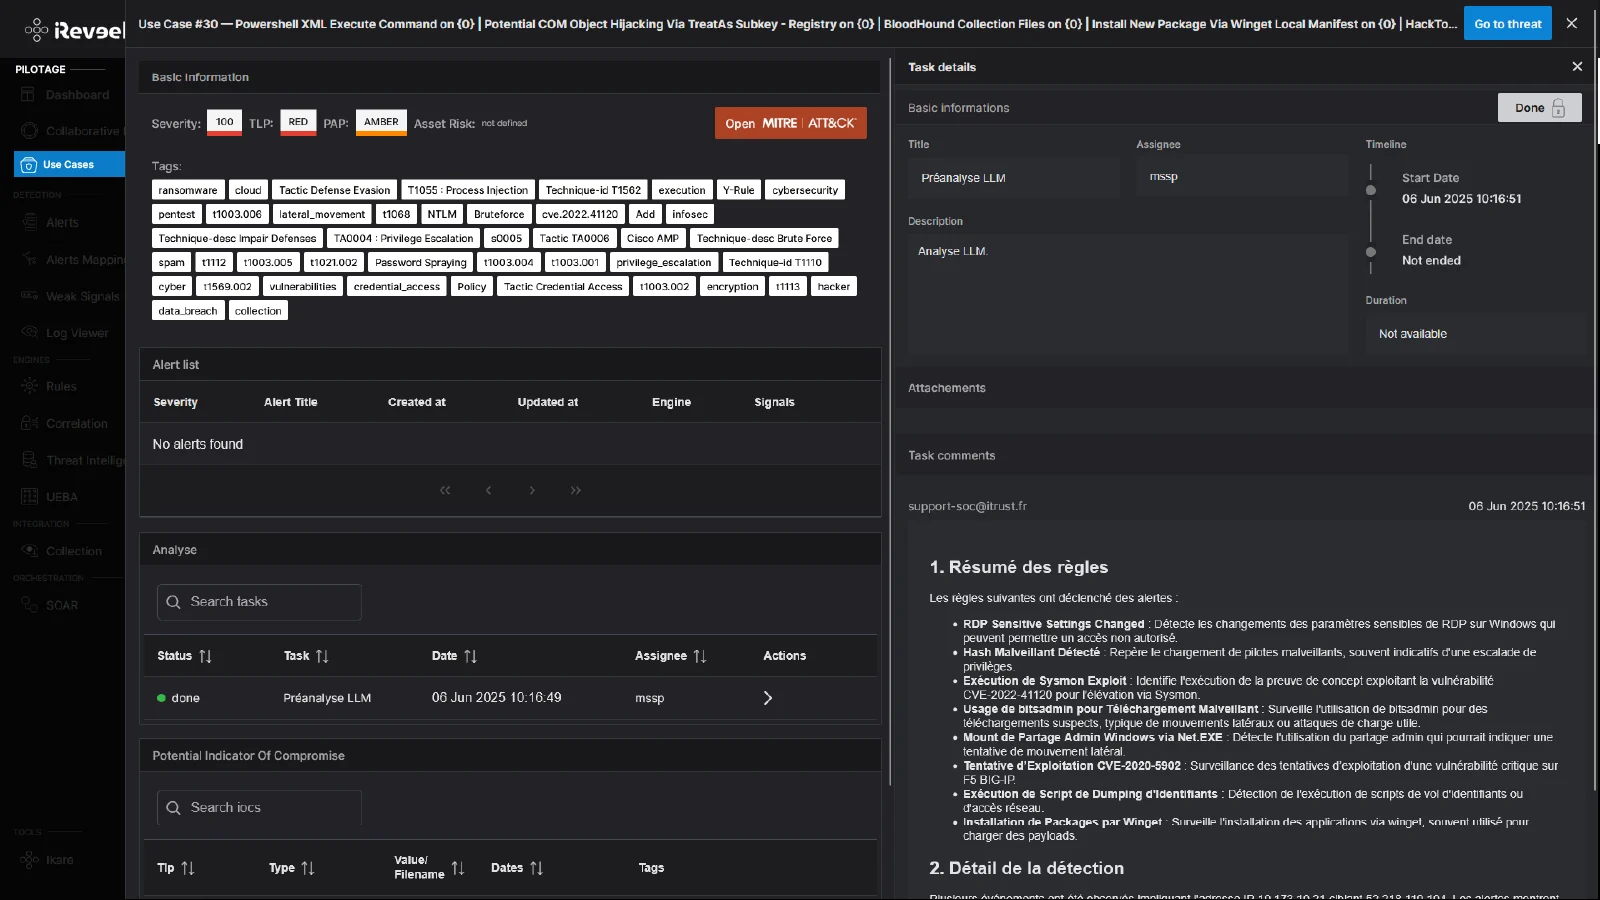
A threat is flagged in the SOC. The analyst investigates it, interacts with the client to gather the necessary contextual elements, draws a conclusion, and closes the alert. The analysis is complete, but it has also generated valuable intelligence about the client's environment. What happens to this knowledge when a similar scenario occurs a few weeks later? With the Use Case feature of Reveelium v12.5, insights gained from a previously analyzed and qualified threat can now be capitalized upon and leveraged during future analyses. Turning a closed threat into actionable intelligence With Reveelium v12.5, an identified, qualified, and closed threat can be [...]

How Reveelium turns analyzed threats into actionable knowledge for future ones2026-10-15T09:23:29+02:00

Mandatory electronic invoicing: what are the cyber risks for businesses?

As of September 1, 2026, the electronic invoicing reform has officially come into effect in France. All VAT-registered businesses must now be able to receive electronic invoices, while large corporations and mid-caps must also issue them in this format. SMEs and micro-enterprises will join this framework starting September 1, 2027. Behind this regulatory change lies a major cybersecurity challenge. The affected B2B invoices now transit through accredited platforms, either directly or via compatible solutions. For organizations, this introduces a potential multiplication [...]

Mandatory electronic invoicing: what are the cyber risks for businesses?2026-10-15T08:52:11+02:00

ITrust CERT Joins InterCERT France

Following its participation in the second cohort of the InterCERT incubator in 2024, the ITrust CERT has formalized its membership in InterCERT France, the premier French community of Computer Emergency Response Teams (CERTs). This marks a new milestone in expanding our incident response operations and our commitment to the French cyber ecosystem. InterCERT France: strengthening cooperation among incident response teams Established in 2021, the InterCERT France association unites cybersecurity incident detection and response teams (CERT/CSIRT) from both public and private organizations. Its objective is to foster operational cooperation, knowledge [...]

ITrust CERT Joins InterCERT France2026-10-14T17:33:16+02:00

Threat Actor Spotlight: ZeroBytes

Active in France since at least July 2026, ZeroBytes is a cybercrime group specializing in data theft and resale. Operating across social media platforms, it targets both public and private organizations without any specific sector bias. Its modus operandi relies primarily on exploiting compromised credentials and legitimate access, enabling the exfiltration of sensitive data without necessarily exploiting critical vulnerabilities or deploying malware. This approach underscores the critical role of digital identity in attack chains. Compromised credentials as the primary access vector The operational model detailed by ZeroBytes relies mainly on leveraging previously [...]

Threat Actor Spotlight: ZeroBytes2026-10-15T08:39:37+02:00

Reverse Engineering of a Recent PureLogs Stealer Campaign

Among the daily attacks monitored by SOC analysts during their surveillance operations, stealer-type malware occupies a prominent position. These malicious programs, designed to harvest passwords stored insecurely on endpoints, are heavily utilized by threat actors in credential-harvesting campaigns. The attacks are straightforward, rapid, and easily scalable. Infostealers include well-known variants such as Lumma Stealer, Vidar, RedLine, and others. Around mid-July 2026, an EDR instance deployed at a client site blocked network traffic resulting from the execution of [...]

Reverse Engineering of a Recent PureLogs Stealer Campaign2026-09-02T10:41:15+02:00

Cyber Resilience Act: manufacturers face the September 2026 deadline and new ETSI standards

The Cyber Resilience Act (CRA) is no longer merely a legislative framework on the distant horizon. It is decisively entering its operational phase. On August 17, 2026, ETSI (European Telecommunications Standards Institute) officially initiated the approval process for 17 key European standards designed to support the implementation of the regulation. These standards cover a broad spectrum, ranging from operating systems to connected objects (IoT), tangibly defining what "security by design" entails for any product with digital elements marketed within the European Union. The pitfall of overlapping deadlines: an initial milestone before 2027 A distinctive feature [...]

Cyber Resilience Act: manufacturers face the September 2026 deadline and new ETSI standards2026-08-18T10:37:39+02:00

DORA: what concretely changes for financial sector cybersecurity and compliance in 2026

The European Digital Operational Resilience Act (DORA), which came into force on January 17, 2025, is now fully embedded within the financial sector's supervisory framework. Following a year in 2025 largely dedicated to assisting financial entities in implementing their new obligations, 2026 marks a phase of heightened supervision. Competent authorities, including the ACPR in France, are notably stepping up their audits of incident management, ICT risk management frameworks, and relationships with third-party IT service providers. DORA thus establishes a harmonized framework aimed at strengthening the digital operational resilience of entities [...]

DORA: what concretely changes for financial sector cybersecurity and compliance in 20262026-08-18T16:45:36+02:00

NIS2 in 2026: how to anticipate compliance despite transposition delays in France

As we enter the second half of 2026, the French transposition of the NIS2 (Network and Information Security) Directive remains pending. This delay compared to the initial schedule has triggered infringement proceedings by the European Commission. However, for the thousands of essential and important entities affected, waiting for the final publication of the law in the Official Journal would be a strategic mistake. The urgency is not legislative; it is operational. The trap of waiting: why ANSSI is not awaiting the law While the national legal framework is still under discussion, the National Cybersecurity Agency of France [...]

NIS2 in 2026: how to anticipate compliance despite transposition delays in France2026-08-18T10:35:44+02:00
Go to Top