About ITrust

This author has not yet filled in any details.
So far ITrust has created 141 blog entries.

🚨 LEVEL 1 SOC ALERT – Critical Microsoft Windows “PrintNightmare” Vulnerability

Critical Microsoft Windows “PrintNightmare” Vulnerability On June 29, 2021, a zero-day flaw affecting the Windows Print Spooler was widely disclosed. Currently unpatched, this critical vulnerability affects servers running Windows 7 and subsequent versions. An initial patch was released on July 8 by the vendor. What are the risks to your business? This flaw enables remote code execution, resulting in system-level privilege escalation for any user with an Active Directory account. An attacker could install programs, view, modify, or delete data, or create new accounts with full [...]
🚨 LEVEL 1 SOC ALERT – Critical Microsoft Windows “PrintNightmare” Vulnerability2025-10-23T16:34:18+02:00

[Replay 🎬] – Healthcare & Cybersecurity Meeting: Preventing attacks using a vulnerability scanner

ITrust and the Centrale d'Achat de l'Informatique Hospitalière (C.A.I.H) provide concrete solutions to address the waves of cyberattacks hitting the healthcare sector. Our upcoming joint webinar will focus on the vulnerability scanner. As the first line of defense, the scanner enables you to assess your IS security posture on a daily basis. Leveraging scoring and intuitive dashboards, IKare clearly highlights your strengths and provides details on vulnerabilities requiring prompt remediation. This ensures not only the compliance of your IS, but also [...]

[Replay 🎬] – Healthcare & Cybersecurity Meeting: Preventing attacks using a vulnerability scanner2025-10-23T16:35:10+02:00

New ways of working: how EDR can protect mobile and (hyper)connected workstations

The widespread adoption of remote work over recent months has further accelerated enterprise mobility trends. From SMEs to large corporations, all must address increased cyber risks stemming from endpoints operating outside the control of technical teams, more frequent external connections, and employees with limited cybersecurity awareness left to their own devices… These challenges were already present for international organizations or those with a substantial number of staff regularly working off-site (sales reps, consultants, etc.). Managing such a dispersed IS can rapidly become an [...]

New ways of working: how EDR can protect mobile and (hyper)connected workstations2026-04-14T09:18:31+02:00

Healthcare data security: why is this sector specifically targeted by cyberattacks? (1/1)

Since 2020, not a week goes by without a new cyberattack targeting a hospital or another healthcare stakeholder. In this article, we examine cyberattacks targeting healthcare institutions and organizations, from hospitals to pharmaceutical laboratories. The first section will focus on how threat actors monetize these attacks. The second will provide an overview of the current state of information systems security within the French healthcare sector. Incentives for attackers In France, an average of one successful attack [...]

Healthcare data security: why is this sector specifically targeted by cyberattacks? (1/1)2025-10-23T16:35:40+02:00

🚨 LEVEL 1 SOC ALERT – REMEMBER – ONCE AGAIN – TO PATCH YOUR EXCHANGE SERVERS!

NEW MICROSOFT EXCHANGE SERVER VULNERABILITIES Microsoft yesterday released security patches addressing new zero-day vulnerabilities. Just one month after the ProxyLogin vulnerability, Exchange Server versions 2013, 2016, and 2019 are once again affected by critical flaws. These vulnerabilities could allow an attacker to gain control of the Exchange server and potentially the Active Directory domain. What are the risks to your business? The full extent of the potential consequences of these vulnerabilities is not yet fully determined. However, threat actors may already be exploiting them. The flaws allow an attacker to execute [...]

🚨 LEVEL 1 SOC ALERT – REMEMBER – ONCE AGAIN – TO PATCH YOUR EXCHANGE SERVERS!2025-10-23T16:35:48+02:00

ITrust and the Ministerial Department for Artificial Intelligence sign an agreement to enhance AI security.

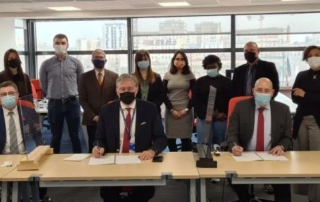
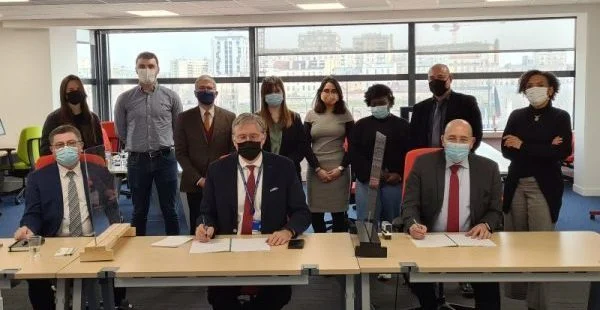
Prefect JASPERS and Mr. David OFER sign the agreement, in the presence of Member of Parliament Mr. MIS   Prefect JASPERS, head of cybersecurity projects at the DMIA, and Mr. David OFER, Vice President of ITrust, signed a partnership agreement on Tuesday, March 9, 2021, to foster the development and security of algorithms and Artificial Intelligence.   In the presence of MP J.M. MIS, ITrust and the DMIA initiated a collaboration on strategic shared study topics:   A working group bringing together Data Scientists from the DMIA and ITrust, focusing on [...]

ITrust and the Ministerial Department for Artificial Intelligence sign an agreement to enhance AI security.2025-10-23T16:36:03+02:00

Who is the Winner? The MITRE Matrix-Based Benchmark of the Best Protective Technologies

Field Feedback: CIOs, CISOs, or executives frequently ask us what best practices to adopt to ensure swift, effective protection. The first answer I provide is to identify risks and establish a streamlined organization (CISO, DPO, ISSP) tailored to how the organization operates. At ITrust for the past 14 years, we have had time to develop strong convictions regarding best practices, correlating them with those recognized by ANSSI, ENISA, or SANS. We hold firm convictions, and we set out to validate them through a mini-study based [...]

Who is the Winner? The MITRE Matrix-Based Benchmark of the Best Protective Technologies2025-10-23T16:36:20+02:00

New Version of the Reveelium SOC: ITrust Strengthens Its SOC with New Algorithms

4 times more attacks against organizations in 2020, a +255% increase in ransomware attack reports to ANSSI*, a major national cyber plan announced: IT security is an ever-growing challenge for organizations of all sizes. To safeguard you against known and unknown threats (APTs, emerging malware, data theft, etc.), ITrust has developed an innovative security solution: Reveelium UEBA. By combining AI, Threat Hunting, Threat Intelligence, and SOAR, Reveelium leverages events that could threaten your information system to proactively anticipate them. Discover the security solution developed by ITrust through a [...]

New Version of the Reveelium SOC: ITrust Strengthens Its SOC with New Algorithms2025-10-23T16:36:28+02:00

🚨 LEVEL 1 SOC ALERT – CHANGE YOUR PASSWORDS!

COMB Data Breach: CHANGE YOUR PASSWORDS! The largest data breach ever recorded was recently exposed. More than 3 billion personal and professional login credentials and passwords for Gmail, Hotmail, LinkedIn, and Netflix have been made accessible to cybercriminals. Dubbed COMB for “Compilation of Many Breaches,” this dataset is actually a compilation aggregated from multiple attacks against major corporations. The scale of the published information is so vast that we recommend changing your credentials—both personal and professional—as soon as possible. What are the risks to your [...]

🚨 LEVEL 1 SOC ALERT – CHANGE YOUR PASSWORDS!2025-10-23T16:36:37+02:00

IP address spoofing: old tricks are still the best

IP address spoofing is an age-old issue that has generated endless discussion, yet remains highly relevant today. Being able to impersonate another entity on a network confers significant leverage and considerable potential for harm. IP spoofing therefore involves spoofing at Layer 3 of the OSI model. Here are the risks you face if you do not prevent IP address spoofing: - INTERNAL INTERCEPTION: Redirecting traffic to an attacker-controlled machine that logs everything. The attacker replaces the legitimate network gateway address with that of an unauthorized machine configured to relay everything to the [...]

IP address spoofing: old tricks are still the best2025-10-23T16:36:52+02:00
Go to Top