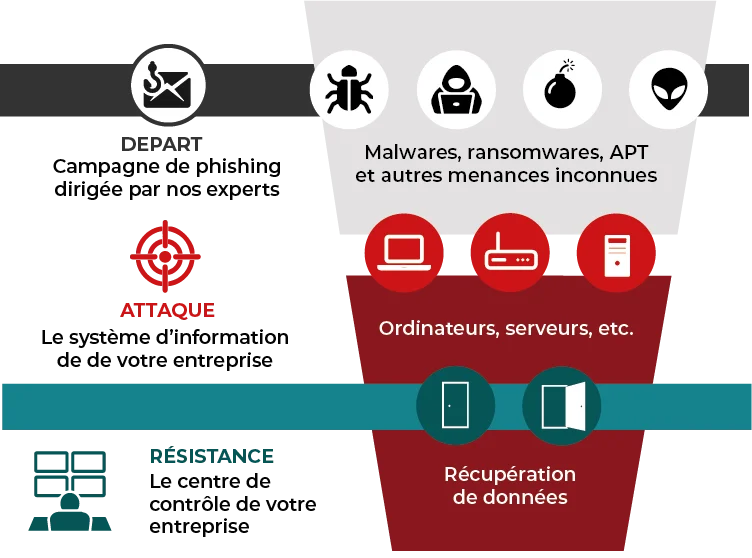
Process of the SOC Stress Test
Beyond compliance requirements, ITrust can support you in testing the detection capabilities of your SOC. A team of penetration testers and developers will assist you throughout this project.
Facing a surge in cybercrime risks, a series of regulatory frameworks require organizations to secure their information systems and data.
GDPR, HDS monitoring, and the Military Planning Law (LPM) directives are establishing new legislative standards for protecting:
- Personal data
- Information systems of vital importance (Order of June 10, 2016)
- Healthcare data protection
Although distinct, these regulatory mandates require notifying the CNIL and ANSSI of any data breach or malicious incident affecting the organization.
You have deployed a SOC or are considering implementing one. You want to verify:
- The detection performance of SOC tools: SIEM, alerting mechanisms, scanners, network probes, etc.
- Decision-making workflows and SLAs of your internal teams or external SOC provider
- That the SOC is configured according to security best practices (PDIS, legal log retention, basic attack detection)
- That the SOC effectively detects emerging threats such as ransomware, APTs, data exfiltration (DLP), espionage, phishing, malware, DNS tunneling, and more…
You require assurance and need to evaluate the capabilities of your internal SOC, your provider's SOC, or a SOC solution you are planning to deploy.
We test it for you (in production or during the POC phase) utilizing the latest attack techniques
Facing a surge in cybercrime risks, a series of regulatory frameworks require organizations to secure their information systems and data.
GDPR, HDS monitoring, and the Military Planning Law (LPM) directives are establishing new legislative standards for protecting:
- Personal data
- Information systems of vital importance (Order of June 10, 2016)
- Healthcare data protection
Although distinct, these regulatory mandates require notifying the CNIL and ANSSI of any data breach or malicious incident affecting the organization.
You have deployed a SOC or are considering implementing one. You want to verify:
- The detection performance of SOC tools: SIEM, alerting mechanisms, scanners, network probes, etc.
- Decision-making workflows and SLAs of your internal teams or external SOC provider
- That the SOC is configured according to security best practices (PDIS, legal log retention, basic attack detection)
- That the SOC effectively detects emerging threats such as ransomware, APTs, data exfiltration (DLP), espionage, phishing, malware, DNS tunneling, and more…
You require assurance and need to evaluate the capabilities of your internal SOC, your provider's SOC, or a SOC solution you are planning to deploy.
We test it for you (in production or during the POC phase) utilizing the latest attack techniques
Contact us
An initial consultation with our team will allow us to fully understand your requirements and provide you with a tailored quote.