Penetration testing – Pentest
Assess the resilience of your network against cyberattacks originating from the Internet or internally, whether by malicious personnel, an intern, etc.
We offer various approaches: external, internal, black box, or white box penetration tests…
External Penetration Test
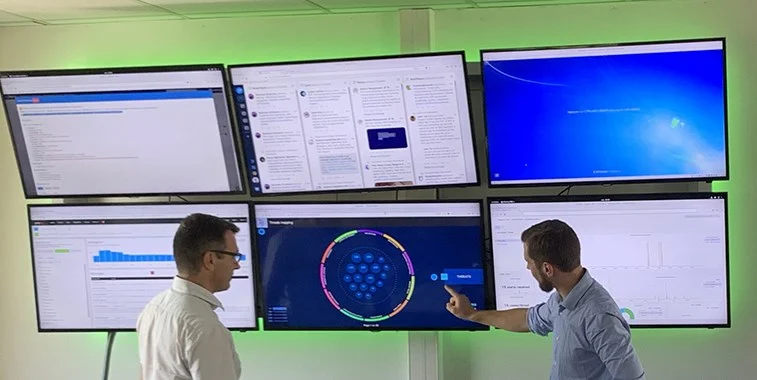
A penetration test aims to evaluate the exposure of your infrastructure on the Internet, assess the resilience of your information system against attacks conducted externally or internally, and provide a set of actionable recommendations to enhance your security posture. To achieve this, security engineers attempt to access supposedly sensitive or confidential data.
The external penetration test is conducted in successive, optimized phases, leveraging the expertise and proven track record of ITrust consultants based on a methodology refined since 2007 and deployed across more than 500 audits:
Internal Penetration Test
An internal penetration test assesses the resilience of your network against attacks originating from within your perimeter. To achieve this, security engineers attempt to access sensitive or confidential data.
Through the provisioning of a privileged account on the network, the tests can extract configuration and installation data from target systems, yielding a more comprehensive evaluation of the internal network's security posture.
Also referred to as a user account audit, the internal penetration test measures internal threat capacity: rogue employees or compromised workstation scenarios.
Our Approach to Penetration Testing
The black box penetration test simulates an external attacker targeting your organization without prior knowledge. We initiate the assessment with minimal information, identify the attack surface, and validate the discovered assets with you before launching more offensive operations.
During a white box penetration test, you provide full scope and architectural details at the onset of the engagement.
ITrust deploys senior security auditors who also possess extensive experience in designing, implementing, and operating technical infrastructures. These certified professionals are seasoned infrastructure engineers capable of diagnosing technical flaws in real time and promptly recommending architectural mitigations, workarounds, or remediation solutions.
Our methodology adheres to industry-recognized standards: OSSTMM for network and systems infrastructure, and OWASP for web application security. ITrust is a co-founder of the FPTI (French Federation of Penetration Testing Professionals).
Quality Above All!
Our engineers are vetted and proven specialists forming the ITrust RedTeam. All team members are permanent employees based in France. We do not subcontract our engagements to external engineers, except under exceptional circumstances and with explicit client authorization.


Strong Commitment to the PASSI Standard and Critical National Infrastructures (OIV)
As part of safeguarding sovereign French data assets and industrial leaders, ITrust is committed to certification processes overseen by ANSSI:
– CSPN certification for its Ikare platform (vulnerability scanning, asset management, and risk scoring),
– PASSI qualification for security audit services.
ITrust holds the France Cybersecurity label.
Our capital is 100% French.
Our engineers are exclusively based on French territory.
Independence, Ethics, and Continuous Expertise
To guarantee uncompromised service quality and complete vendor neutrality regarding third-party vendors and software publishers, ITrust guarantees:
⇒ Absolute independence from third-party software publishers and service providers:
– ITrust’s capital and professional services are entirely independent from software publishers and
systems integrators (see Code of Ethics);
– Our ethical charter ensures absolute impartiality in our auditing services and security recommendations.
⇒ Enforced quality frameworks and operational rigor through:
– Its proprietary Man 3 methodology;
– Its code of ethics, signed by every employee;
– Its formal integrity policy.
⇒ Active participation in ISO 27001, EBIOS, and RGS working groups through corporate memberships in bodies such as:
– PRISSM, cybersecurity professional think tank;
– CLUSIF;
– Club 27001;
– OSSIR;
– Cercle Européen de la Sécurité;
– ECSO (European Cyber Security Organisation).
⇒ Regular contributions to major conferences as an exhibitor and keynote speaker on advanced cybersecurity topics, including:
– Botconf (2014, 2018);
– DEF CON / Black Hat Las Vegas (2009, 2018);
– CRIP;
– Cloud Conference;
– French National Assembly: Hearings on Cloud computing and cybersecurity.
Code of Ethics
ITrust enforces a strict code of ethics governing every engagement, ensuring that:
– Audit operations are conducted with integrity, discretion, impartiality, and complete independence;
– Auditors exclusively use methodologies, frameworks, and tooling validated by ITrust;
– Auditors are bound by strict confidentiality and shall not disclose any audit-generated data, even to uninvolved internal personnel, without explicit client consent;
– Auditors will immediately notify the client of any clearly unlawful findings uncovered during the assessment;
– Auditors adhere strictly to applicable laws, regulatory mandates, and professional auditing best practices (ISO 19011);
– All auditors are individual signatories to our code of ethics.