Definition of a SOC: Understanding the Security Operations Center
What is a SOC?
A SOC (Security Operations Center, or Centre Opérationnel de Sécurité in French) is an essential component of corporate security architecture. It is a centralized platform, typically composed of a team of cybersecurity experts, advanced monitoring tools, and procedures designed to detect, analyze, and respond to security threats. The primary role of a SOC is to ensure the continuous protection of the organization's information systems and sensitive data against cyberattacks, security incidents, and potential breaches.
SOC Operations and Objectives
The SOC operates by collecting and analyzing data from a wide range of sources: firewalls, intrusion detection systems (IDS/IPS), server logs, endpoint detection and response (EDR), and other network devices. This data collection enables real-time monitoring of events that could indicate anomalous behavior or intrusion attempts.
Key Components of a SOC
An effective SOC relies on three major pillars: people, processes, and technology.
1. People
Security analysts, engineers, and SOC managers form the core of this structure. They provide the expertise required to interpret data, identify anomalies, and coordinate incident response. The SOC encompasses several tiers of expertise:
- Tier 1 (L1): Alert intake and triage.
- Tier 2 (L2): In-depth incident analysis.
- Tier 3 (L3): Handling complex incidents, threat hunting, and authoring advanced SIEM rules.
2. Processes
The SOC follows well-defined processes for threat detection and response. Standard procedures such as Incident Response and Disaster Recovery Plans are systematically implemented to ensure a swift and effective response.
Playbooks (standard operating procedures) are essential in SOCs to standardize actions when a specific incident is detected.
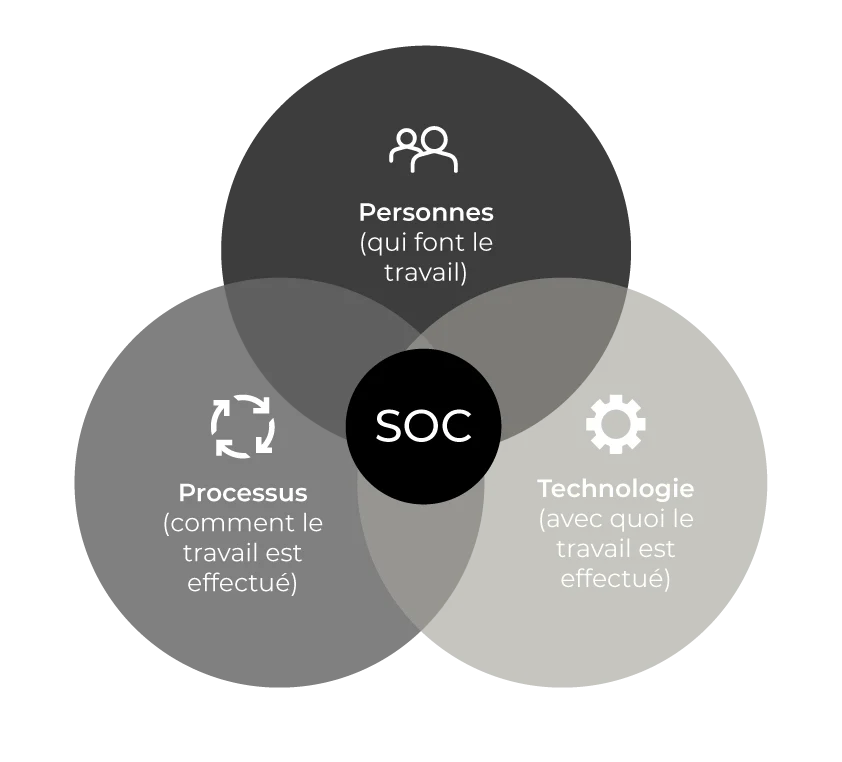
3. Technology
The SOC relies on a suite of advanced technologies to automate monitoring, enhance detection, and reduce response times. Key tools include:
- SIEM (Security Information and Event Management): Centralizes and correlates security events from multiple sources.
- EDR (Endpoint Detection and Response): Monitors endpoints to detect malicious behavior.
- NDR (Network Detection and Response): Analyzes network traffic to identify threats.
- SOAR (Security Orchestration, Automation, and Response): Automates specific response tasks, optimizing the SOC's operational efficiency.
How a Security Operations Center Uses MITRE ATT&CK to Improve Detection
A Security Operations Center (SOC) utilizes the MITRE ATT&CK framework to structure and enhance its detection capabilities based on an in-depth understanding of adversaries' tactics, techniques, and procedures (TTPs). By leveraging this comprehensive knowledge base, a SOC can identify suspicious behaviors across different stages of an attack, going beyond simple Indicators of Compromise (IoCs). Using MITRE ATT&CK thus allows organizations to map attack techniques to deployed security solutions, identifying detection gaps and implementing more robust defensive strategies.
To maximize detection effectiveness, combining different security tools is crucial. Each tool provides specific, complementary coverage. By combining these technologies, the SOC achieves comprehensive visibility and more proactive detection, thereby enhancing its ability to rapidly identify and respond to complex and advanced threats.

How a SOC Uses MITRE ATT&CK
The Importance of Automation and Machine Learning in Modern SOCs
Modern SOCs increasingly rely on automation and artificial intelligence technologies to enhance their detection and threat response capabilities. Because alert volumes are frequently overwhelming, machine learning algorithms help prioritize incidents, identify new or advanced threats, and reduce analyst workloads.
Automation systems, such as SOAR, are essential for orchestrating rapid responses, enabling the SOC to handle large-scale or multiple incidents effectively. This improves not only response speed, but also the precision of the actions taken.
Contact us
An initial consultation with our team will allow us to fully understand your requirements and provide you with a tailored quote.