How Reveelium turns analyzed threats into actionable knowledge for future ones
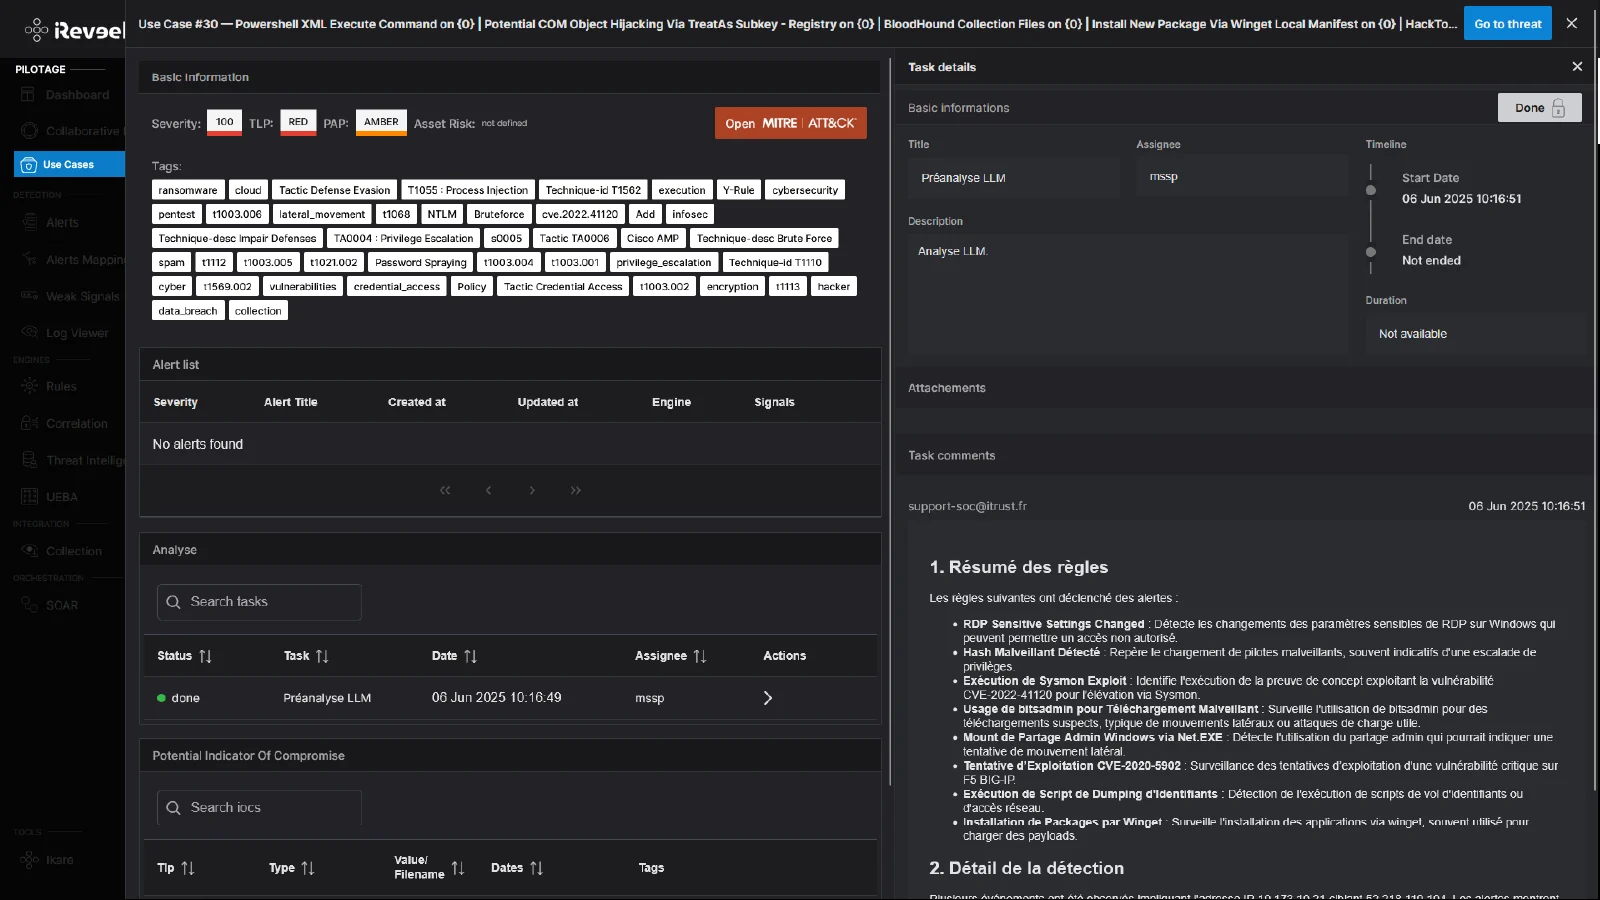
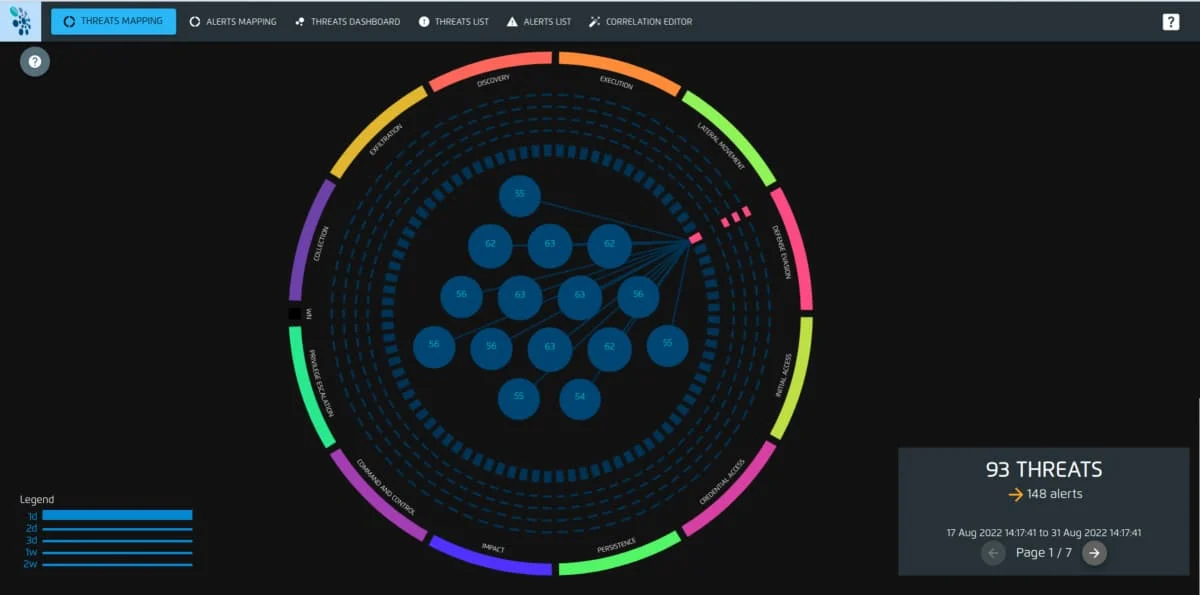
A threat is flagged in the SOC. The analyst investigates it, interacts with the client to gather the necessary contextual elements, draws a conclusion, and closes the alert. The analysis is complete, but it has also generated valuable intelligence about the client's environment. What happens to this knowledge when a similar scenario occurs a few weeks later? With the Use Case feature of Reveelium v12.5, insights gained from a previously analyzed and qualified threat can now be capitalized upon and leveraged during future analyses. Turning a closed threat into actionable intelligence With Reveelium v12.5, an identified, qualified, and closed threat can be [...]