Purple Team: when AI orchestrates defense

In April 2026, ITrust presented the findings of a research project conducted by its SOC team at the InCyber Forum (FIC). Thomas Bourthoumieux, SOC Director, and Félix Billières, Tier 3 SOC Analyst, shared the work carried out by the Tier 3 team and ITrust's broader Blue Team: embedding recent advancements in artificial intelligence into the SOC operational workflow. This initiative directly addresses a widely acknowledged industry challenge: traditional purple team cycles are too slow, fragmented, and poorly reproducible to keep pace with threat actors. The goal was to empower a [...]
Purple Team: when AI orchestrates defense2026-04-14T10:44:56+02:00

Case Study: An SME targeted by Kryptis avoids €500,000 in losses thanks to Reveelium

One of our clients was targeted by a Kryptis cyberattack.  €500,000 in losses: that is the estimated cost for this legal sector SME if the attack had succeeded (data loss, ransom demand, potential CNIL fine). The indirect impact is harder to quantify: loss of client trust (with their data exposed in the wild), tarnished brand reputation… In this article, discover how we were able to detect and block this cyberattack by leveraging the triptych of Reveelium XDR SIEM UEBA, Threat Intelligence, and human expertise. Focus on Kryptis: stealth malware [...]

Case Study: An SME targeted by Kryptis avoids €500,000 in losses thanks to Reveelium2025-10-23T15:15:36+02:00

Use Case: How Reveelium Meets the Needs of All Users Through Multi-Level Cyber Supervision

Reveelium is a SIEM XDR technology that detects known and unknown cyber threats and traces the footprints of cyberattacks. Its interface provides a secure collaborative workspace, granting real-time access to the same level of information across various stakeholders (Lead CIOs, SOC analysts, etc.). Multi-tier monitoring tailored to every profile Reveelium incorporates dashboards designed to adapt to different governance and operational tiers. Every user can access the strategic or technical indicators and views aligned with their specific scope of action. Strategic Monitoring: CIOs, CISOs, and executive committee members have access to [...]

Use Case: How Reveelium Meets the Needs of All Users Through Multi-Level Cyber Supervision2025-10-23T16:10:47+02:00

How does Threat Hunting accelerate incident response?

Threat Hunting is a core pillar of the ITrust SOC: technical, strategic, and resolutely proactive. This threat hunting shortens incident response times, curbs dwell time, and enhances Reveelium's detection capabilities by enriching the data analyzed during hunting sessions. Methodology, operational processes, feedback: step inside the daily operations of a Threat Hunter. Threat Hunting vs. Threat Intelligence While fundamentally distinct, these two disciplines are complementary. Threat Hunting explores, Threat Intelligence enlightens, and together, they mutually enrich one another to reinforce the defensive posture against increasingly complex threats [...]

How does Threat Hunting accelerate incident response?2025-10-23T16:11:58+02:00

How Reveelium, the French SIEM XDR, leverages the MITRE ATT&CK® framework to strengthen its detection capabilities

Adopted by thousands of organizations worldwide, the MITRE ATT&CK knowledge base is regularly updated to reflect the latest evolutions in cyber threats, driven by thousands of contributions from the cybersecurity community and shared threat intelligence. Its integration into the Reveelium platform enhances its detection and investigation capabilities, enabling teams to efficiently identify, analyze, and respond to the tactics and techniques employed by cyberattackers. MITRE ATT&CK: An Essential Technical Framework for Cybersecurity Experts The MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) framework is an open-source model documenting the tactics, [...]

How Reveelium, the French SIEM XDR, leverages the MITRE ATT&CK® framework to strengthen its detection capabilities2026-04-14T09:08:01+02:00

How ITrust Helped a Major Ministry Strengthen Its Cyber Defense

How ITrust Helped a Major Ministry Strengthen Its Cyber Defense In an ever-evolving digital landscape, cybersecurity has become a vital imperative for organizations. With recognized expertise and an innovative Managed SOC, ITrust played a pivotal role in strengthening the cyber defense posture of a major French ministry. Concurrently, SOC (Security Operations Center) market trends are shifting rapidly, incorporating advanced technologies to counter increasingly sophisticated threats. LEARN MORE The Cyber Defense Challenge in the Modern World: Security threats are evolving faster [...]

How ITrust Helped a Major Ministry Strengthen Its Cyber Defense2026-04-14T09:07:25+02:00

XDR: The solution to block all attacks

IT security teams must now manage data originating from an extended and increasingly complex network encompassing multiple clouds and SaaS (Software-as-a-Service) applications, a growing number of sites with new SD-WAN connections, connected devices (IoT), OT systems, mobile workers and devices, and now, dozens or even hundreds of home offices. XDR, a Necessary Technology Today To adapt to data volume, velocity, and variety, Extended Detection and Response (XDR) technologies prove essential for collecting and processing [...]

XDR: The solution to block all attacks2026-04-14T09:20:13+02:00

What is a Managed EDR or MDR?

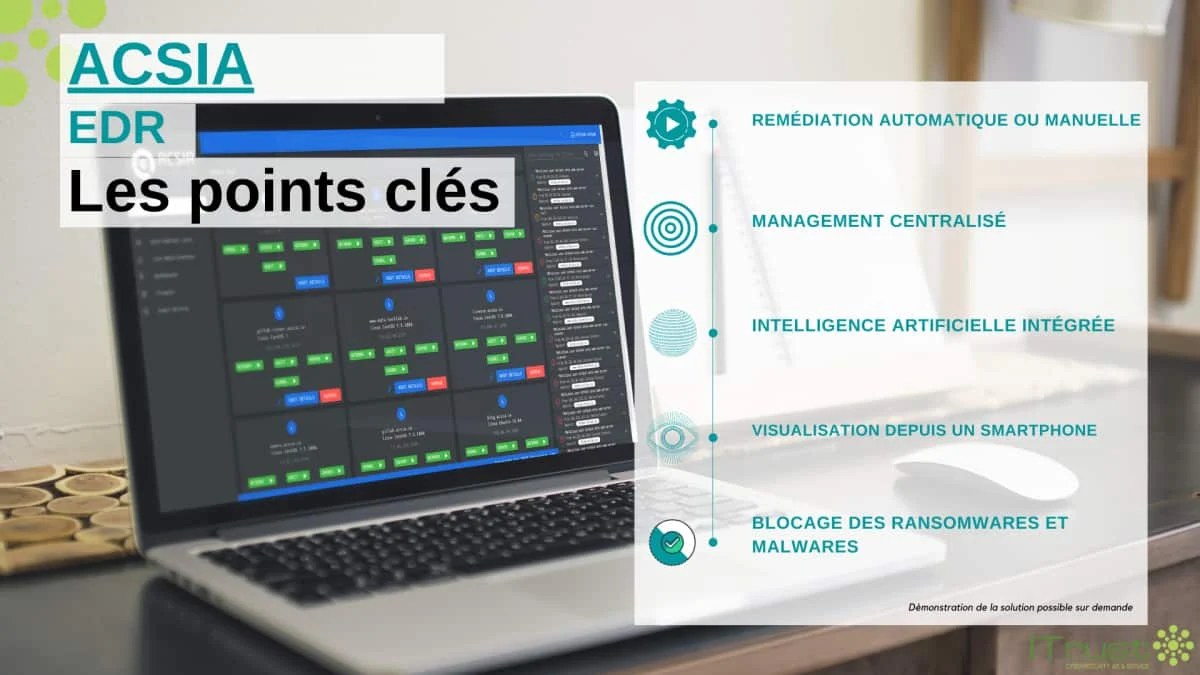
Deploying a managed EDR or MDR is more critical than ever today. Here is useful information to support you in your project to implement a managed EDR. What is an EDR solution? Endpoint Detection and Response (EDR) is a suite of cybersecurity tools designed to detect and eliminate any malware or other malicious activity directed at endpoints connected to your corporate network. Indeed, endpoints and workstations are the preferred targets of cyberattacks since they constitute the weak link in an enterprise network. For example, [...]

What is a Managed EDR or MDR?2026-04-14T09:19:42+02:00

Concrete Use Case of AI in Cybersecurity: The DGA Algorithm

Since 2018 and the release of the 1st version of Reveelium, the team at ITrust has been convinced of the value of Artificial Intelligence for cybersecurity. In recent years, market trends have proven us right: from SMEs to industry giants, all rely on this technology to increase their threat detection capabilities tenfold. What do we mean by AI? Reveelium is not yet able to think like a human, and therefore does not replace the expertise of an accomplished SOC analyst. That being said, the practice of AI at ITrust goes far beyond the IF/THEN rules, even optimized, that have long [...]

Concrete Use Case of AI in Cybersecurity: The DGA Algorithm2026-04-14T09:18:56+02:00

New ways of working: how EDR can protect mobile and (hyper)connected workstations

The widespread adoption of remote work over recent months has further accelerated enterprise mobility trends. From SMEs to large corporations, all must address increased cyber risks stemming from endpoints operating outside the control of technical teams, more frequent external connections, and employees with limited cybersecurity awareness left to their own devices… These challenges were already present for international organizations or those with a substantial number of staff regularly working off-site (sales reps, consultants, etc.). Managing such a dispersed IS can rapidly become an [...]

New ways of working: how EDR can protect mobile and (hyper)connected workstations2026-04-14T09:18:31+02:00
Go to Top